
A Truck, a Laptop and No Password: What a Connected Vehicle Test Actually Revealed
Introduction
Picture a pickup truck moving at around 30 kilometres an hour down a straight country road outside Canberra. A journalist is driving it. Somewhere nearby, a researcher sits with a laptop, and without touching the vehicle, he switches the headlights off while it is still moving, in the dark, turns them back on, activates the wipers at full speed, sprays the windscreen washer, and plays sound through the cabin speakers. That scene, broadcast in September 2026 as part of an ABC Four Corners investigation into connected car security, is the starting point for a conversation that extends well beyond the one vehicle involved. (It was a commissioned cybersecurity demonstration, authorised and arranged by ABC's Four Corners as part of their journalistic investigation titled "Asleep at the Wheel.").
What the test actually found
The vehicle at the centre of the investigation was a BYD Shark 6, a plug-in hybrid pickup, which ABC's Four Corners programme provided to automotive cybersecurity researcher Dan Hreszczuk, co-founder of Canberra based Fortify Labs, for a two week authorised assessment. Hreszczuk later described the access point he found in notably simple terms: it did not require a password at all.
Over the course of the test, Hreszczuk demonstrated remote interaction with the vehicle's headlights, windscreen wipers, door locks, cabin speakers and infotainment display. He also tracked the vehicle's real time location and accessed its cabin microphone, which raised concerns beyond vehicle control and into personal surveillance, since a compromised in car microphone can expose private conversations rather than just dashboard functions. It is worth being precise about what the test did not reach. Hreszczuk said he could not access the brakes or the vehicle's cameras, describing those systems as well protected, and the demonstration did not amount to complete remote control of the vehicle.
Following the broadcast, BYD ran its own internal investigation and confirmed a software defect in the Shark 6's infotainment system. The company's engineers reproduced the access path and traced it to Android Debug Bridge, a standard Android development tool that is meant to be disabled in production vehicles but had been left reachable through the defect, alongside a separate route through the vehicle's CAN bus network. BYD has said it will issue an over the air software update to close the gap. Fortify Labs, for its part, stated its objective had been to simulate the kind of remote access a vehicle manufacturer itself typically holds over a connected car, and to demonstrate how that same level of access could be misused if it fell into the wrong hands.
This context matters because it distinguishes a controlled, authorised research exercise, conducted over two weeks with extended physical access to a single vehicle, from an active criminal compromise. No malware was involved, and no evidence has emerged of this technique being used against vehicles outside the test. The finding is nonetheless significant precisely because it shows what becomes possible once a single weak point in a vehicle's software stack is identified and deliberately explored.
The questions this raises, beyond one vehicle
The useful questions are structural ones. How is authentication actually enforced across every vehicle facing service, not just the ones a manufacturer assumes a researcher might look at? Are a vehicle's internal networks and external facing services properly segmented, so that compromising an infotainment system does not create an unobstructed path toward a vehicle's core control units? Are commands subject to strong authorisation and validation at every layer, rather than relying on obscurity or an assumption that a particular access route would be too obscure to find? Is the principle of least privilege consistently applied, so that a development tool left active in a production vehicle, as appears to have happened here, does not carry the same level of access a factory engineer would have? How are unusual remote behaviours actually detected and investigated in real time, rather than discovered after the fact through an external test? And how are vulnerabilities tracked and patched across a vehicle's entire operational lifecycle, given that a car, unlike a phone, is expected to remain in active use for well over a decade after it leaves the factory floor.
A rulebook already exists. The gap is enforcement, not ignorance
None of this had to be worked out from scratch after the Four Corners broadcast. The industry has had a binding answer to most of these questions sitting on the books since 2021, when the World Forum for Harmonization of Vehicle Regulations adopted UN Regulation No. 155, known in the industry simply as R155. It requires any manufacturer seeking vehicle type approval to run a certified Cybersecurity Management System covering the car's entire life, from the drawing board through production and all the way to the vehicle still being driven a decade later, and to pass a dedicated cybersecurity assessment before that vehicle type can legally go on sale. Since July 2024 the rule has applied not just to new vehicle designs but to every new vehicle rolling off the line, across more than sixty countries that are party to the underlying 1958 UNECE agreement, a list that includes the European Union, Japan, South Korea, and Australia itself.
That last detail is where the picture gets genuinely interesting, and where a simple story stops being quite so simple. Australia sits among the countries that have signed on to the UNECE framework R155 belongs to, yet coverage of the Four Corners investigation reported something that sounds contradictory at first glance: that Australia has no minimum cybersecurity standard actually governing cars sold in the country. Both things can be true at once. Being a party to the 1958 Agreement establishes that a country participates in the broader regulatory architecture; it does not automatically mean every regulation born out of that architecture has been separately adopted into domestic law and is being actively enforced at the point of sale. R155's own companion standard, ISO/SAE 21434, is the detailed engineering playbook manufacturers actually use to meet the regulation's requirements, walking through how to assess threats, design around them, and keep monitoring for new ones long after a vehicle has left the factory. A framework that comprehensive existing on paper is only as useful as a given market's willingness to actually require manufacturers to follow it before a car reaches a driveway, and that gap between a regulation existing globally and a regulation being enforced locally is arguably the more unsettling finding buried inside this story than the hack itself.
The broader lesson
The real takeaway from this test has very little to do with the particular badge on the vehicle involved. It is a demonstration of what happens when any one interface in a complex, connected system is left weaker than the rest of the architecture around it. As vehicles continue absorbing more software, more connectivity and more remote functionality, security boundaries cannot be treated as a feature added once at launch. They need to be designed deliberately, enforced consistently, and monitored continuously across the entire lifecycle of the vehicle and the ecosystem of backend services it depends on, because the cost of getting that wrong is no longer confined to a screen or a server. It now extends to the physical vehicle itself, and the people inside it.
References
- https://www.pakwheels.com/blog/byd-shark-6-hacked-during-cybersecurity-test-in-australia/
- https://securityaffairs.com/199460/hacking/a-byd-shark-6-hack-shows-the-risks-of-connected-cars.html
- https://autotalk.co.nz/byd-confirms-shark-6-software-defect-after-four-corners-hack-ota-fix-coming/
- https://www.carexpert.com.au/car-news/byds-own-shark-6-hacking-investigation-reveals-software-defect
- https://yourlifechoices.com.au/technology/the-connected-car-warning-behind-byds-shark-6-software-fix
- https://arnav.au/2026/09/22/byd-got-hacked-what-really-happened/
- https://pakobserver.net/byd-shark-6-hacked-in-security-test-as-researcher-gains-access-to-car-systems/
- https://www.femalefirst.co.uk/motoring/byd-issue-security-update-shark-6-after-hacking-concerns-1451532.html
- https://finitestate.io/blog/buckle-up-for-security-a-look-at-the-un-r155-regulation-for-connected-vehicles
- https://www.arteris.com/learn/un-r155-2/

Related Blogs
Executive Summary
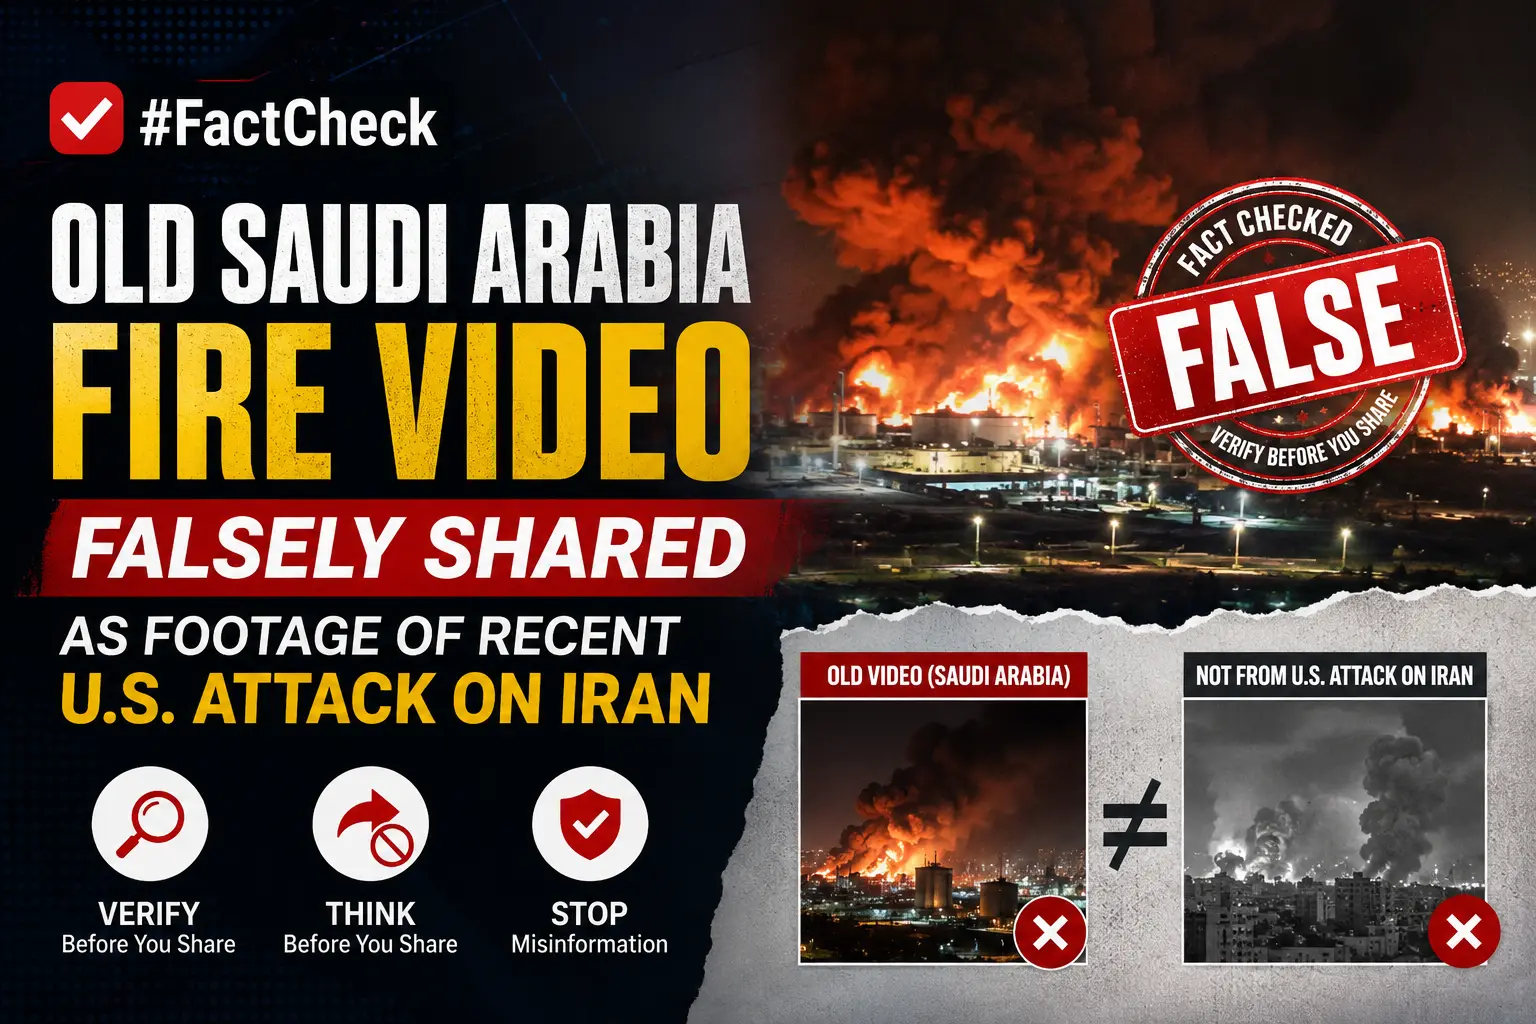
As tensions between the United States and Iran continue to escalate in West Asia, a video showing a massive fire engulfing an industrial facility is being widely circulated on social media. Several users claim that the footage shows the aftermath of a recent U.S. strike on Iran. CyberPeace Research Wing’s research found the claim to be false. Our research revealed that the viral video is not related to the current U.S.-Iran conflict. It actually shows a 2022 attack on Saudi Arabia's Aramco petroleum distribution facility in Jeddah, carried out by Yemen's Houthi rebels.
Claim
An X user shared the viral video on July 16, 2026, claiming that it shows a recent American attack on Iran. https://x.com/SonOfBharat7/status/2077823734069826027 , https://perma.cc/RPA9-YZ3C

Fact Check
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search using Google Lens. During the research, we found that the same video had been uploaded by Reuters on March 26, 2022. According to Reuters, Yemen's Houthi rebels claimed responsibility for attacks on Saudi Arabia's energy facilities. Reuters reported that the Saudi-led coalition confirmed an attack on Saudi Aramco's petroleum products distribution station in Jeddah, where two storage tanks caught fire. The incident caused significant damage but no casualties were reported. https://www.youtube.com/watch?v=-CAxj5tgZ_w

For further verification, we found another video of the same incident uploaded by the Qatar Day Facebook page on March 25, 2022, showing the fire from a different angle. According to the post, a massive blaze broke out at an oil depot in Jeddah, Saudi Arabia, after Yemen's Houthi rebels launched multiple drone and missile attacks targeting Saudi infrastructure. Thick black smoke could be seen rising over the city.

Additionally, The Sun also uploaded the same footage on March 26, 2022, identifying it as the attack on Jeddah, Saudi Arabia. https://www.youtube.com/watch?v=bFj5nDL0y7o

Conclusion
Our research found that the viral video does not show a recent U.S. attack on Iran.Although the United States and Iran have recently exchanged military strikes and attacks on civilian infrastructure have been reported, the viral footage predates the current conflict by several years. It actually shows the March 2022 Houthi attack on Saudi Aramco's petroleum distribution facility in Jeddah, Saudi Arabia. Therefore, the claim linking the video to the ongoing U.S.-Iran conflict is false and misleading.

Introduction
Romance scams have been rised in India. A staggering 66 percent of individuals in India have been ensnared by the siren songs of deceitful online dating schemes. These are not the attempts of yesteryears but rather a new breed of scams, seamlessly weaving the threads of traditional deceit with the sinew of cutting-edge technologies such as generative AI and deep fakes. A report by Tenable highlights the rise of romance scams in India, which now combine traditional tactics with advanced technologies like generative AI and deepfakes. Over 69% of Indians struggle to distinguish between artificial and authentic human voices. Scammers are using celebrity impersonations and platforms like Facebook to lure victims into a false sense of security.
The Romance Scam
A report by Tenable, the exposure management company, illuminates the disturbing evolution of these romance scams. It reveals a reality: AI-generated deep lakes have attained a level of sophistication where an astonishing 69 percent of Indians confess to struggling to discern between artificial and authentic human voices. This technological prowess has armed scammers with the tools to craft increasingly convincing personas, enabling them to perpetrate their nefarious acts with alarming success.
In 2023 alone, 43 percent of Indians reported falling victim to AI voice scams, with a staggering 83 percent of those targeted suffering financial loss. The scammers, like puppeteers, manipulate their digital marionettes with a deftness that is both awe-inspiring and horrifying. They have mastered the art of impersonating celebrities and fabricating personas that resonate with their targets, particularly preying on older demographics who may be more susceptible to their charms.
Social media platforms, which were once heralded as the town squares of the 21st century, have unwittingly become fertile grounds for these fraudulent activities. They lure victims into a false sense of security before the scammers orchestrate their deceitful symphonies. Chris Boyd, a staff research engineer at Tenable, issues a stern warning against the lure of private conversations, where the protective layers of security are peeled away, leaving individuals exposed to the machinations of these digital charlatans.
The Vulnerability of Individuals
The report highlights the vulnerability of certain individuals, especially those who are older, widowed, or experiencing memory loss. These individuals are systematically targeted by heartless criminals who exploit their longing for connection and companionship. The importance of scrutinising requests for money from newfound connections is underscored, as is the need for meticulous examination of photographs and videos for any signs of manipulation or deceit.
'Increasing awareness and maintaining vigilance are our strongest weapons against these heartless manipulations, 'safeguarding love seekers from the treacherous web of AI-enhanced deception.'
The landscape of love has been irrevocably altered by the prevalence of smartphones and the deep proliferation of mobile internet. Finding love has morphed into a digital odyssey, with more and more Indians turning to dating apps like Tinder, Bumble, and Hinge. Yet, as with all technological advancements, there lurks a shadowy underbelly. The rapid adoption of dating sites has provided potential scammers with a veritable goldmine of opportunity.
It is not uncommon these days to hear tales of individuals who have lost their life savings to a person they met on a dating site or who have been honey-trapped and extorted by scammers on such platforms. A new study, titled 'Modern Love' and published by McAfee ahead of Valentine's Day 2024, reveals that such scams are rampant in India, with 39 percent of users reporting that their conversations with a potential love interest online turned out to be with a scammer.
The study also found that 77 percent of Indians have encountered fake profiles and photos that appear AI-generated on dating websites or apps or on social media, while 26 percent later discovered that they were engaging with AI-generated bots rather than real people. 'The possibilities of AI are endless, and unfortunately, so are the perils,' says Steve Grobman, McAfee’s Chief Technology Officer.
Steps to Safeguard
Scammers have not limited their hunting grounds to dating sites alone. A staggering 91 percent of Indians surveyed for the study reported that they, or someone they know, have been contacted by a stranger through social media or text message and began to 'chat' with them regularly. Cybercriminals exploit the vulnerability of those seeking love, engaging in long and sophisticated attempts to defraud their victims.
McAfee offers some steps to protect oneself from online romance and AI scams:
- Scrutinise any direct messages you receive from a love interest via a dating app or social media.
- Be on the lookout for consistent, AI-generated messages which often lack substance or feel generic.
- Avoid clicking on any links in messages from someone you have not met in person.
- Perform a reverse image search of any profile pictures used by the person.
- Refrain from sending money or gifts to someone you haven’t met in person, even if they send you money first.
- Discuss your new love interest with your trusted friend. It can be easy to overlook red flags when you are hopeful and excited.
Conclusion
The path is fraught with illusions, and only by arming oneself with knowledge and scepticism can one hope to find true connection without falling prey to the mirage of deceit. As we navigate this treacherous terrain, let us remember that the most profound connections are often those that withstand the test of time and the scrutiny of truth.
References
- https://www.businesstoday.in/technology/news/story/valentine-day-alert-deepfakes-genai-amplifying-romance-scams-in-india-warn-researchers-417245-2024-02-13
- https://www.indiatimes.com/amp/news/india/valentines-day-around-40-per-cent-indians-have-been-scammed-while-looking-for-love-online-627324.html
- https://zeenews.india.com/technology/valentine-day-deepfakes-in-romance-scams-generative-ai-in-scams-romance-scams-in-india-online-dating-scams-in-india-ai-voice-scams-in-india-cyber-security-in-india-2720589.html
- https://www.mcafee.com/en-us/consumer-corporate/newsroom/press-releases/2023/20230209.html

Cyber attacks in India besides becoming common are also getting deadlier. Each strike has taken proportions to drive home the fact that no one is safe.
Hacker ‘John Wick’, hasn’t spared India’s PM or Paytm. Cyber intelligence firm Cyble which dredges the Dark Web has red-flagged hacking episodes at Truecaller, Dunzo, Unacademy, Naukri.com, Bharat Earth Movers Limited (BEML), LimeRoad and IndiaBulls.Picture this, Mumbai-based cybersecurity firm Sequretek, says in Covid-hit 2020, India has seen a 4000% spike in phishing emails and a 400% uptake in the number of policy violations that have grown over 400% as per the latest statistics.Besides the threat to crucial data, the cost suffered by companies is phenomenal. According to a report by IBM’s ‘Cost of a Data Breach Report 2020’ report, Indian companies witnessed an average $2 Mn total cost of data breach in 2020, this is an increase of 9.4% from 2019.
Another survey by Barracuda Networks revealed that 66% of Indian organisations have had at least one data breach or cybersecurity incident since shifting to a remote working model during the pandemic.
Indian Startups At Mercy Of Cyber Attacks
More recently personal data of 2.8 Lakh WhiteHat Jr students and teachers were exposed, where crucial details of minors have been made available on the dark web. Another major breach that took place this week and exclusively reported by Inc42 was when data of 1.4 Mn job seekers was leaked when jobs portal IIMjobs was hacked.
Vineet Kumar, the founder of Cyber Peace Foundation (CPF), a think tank of cybersecurity and policy experts, said that with the increased digitisation of companies and their processes, data has become the new oil.
“You get good money when you sell users data on the dark web. Hackers discovering vulnerabilities and using SQL injections to pull entire databases remains a common practice for hacking,” Kumar told Inc42.
The CyberPeace Foundation says from mid-April to the end of June it noticed 8,98,7841 attacks, July and August saw 64,52,898 attacks. Whereas September and October saw 1,37,37,516 attacks and 18,149,233 attacks respectively.
Speaking to Inc42, Pankit Desai, cofounder and CEO, Sequretek says, “Originally only a limited set of systems were being exposed, now with WFH all systems have to be exposed to the internet as all your processes are enabled remotely. WFH also creates an additional challenge where ‘personal assets are being used for professional purposes’ and ‘professional assets are being used for personal purposes.”
Malwares like SpyMax, Blackwater are being used as a combination of phishing mails and poorly secured home computers to harvest credentials. These credentials are then used for carrying out attacks. The number of attacks with harvested credentials is already up 30%, the company revealed.
Government data shows that in 2019 alone, India witnessed 3.94 lakh instances of cybersecurity breaches. In terms of hacking of state and central government websites, Indian Computer Emergency Response Team (CERT-In) data shows that a total of 336 websites belonging to central ministries, departments, and state governments were hacked between 2017 and 2019.
According to Nasscom’s Data Security Council of India (DSCI) report 2019, India witnessed the second-highest number of cyber attacks in the world between 2016 and 2018. This comes at a time when digitisation of the Indian economy is predicted to result in a $435 Bn opportunity by 2025.On September 22, the Ministry of Electronics and Information Technology (MeITY) told the Parliament that Indian citizens, commercial and legal entities faced almost 7 lakh cyberattacks till August this year.
The Indian Computer Emergency Response Team (CERT-In) has “reported 49,455, 50,362, 53,117, 208,456, 394,499 and 696,938 cybersecurity incidents during the year 2015, 2016, 2017, 2018, 2019 and 2020 (till August) respectively,” the MeITY said while responding to an unstarred question in the Lok Sabha regarding cyberattacks on Indian citizens and India-based commercial and legal entities.“
India also lacks a cohesive nation-wide cyber-strategy, policies, and procedures. Regulations around data privacy, protection, and penalty should be enacted and enforced as these measures will help businesses evaluate their cybersecurity posture and seek ways to improve. Currently, incident reporting is not mandatory. By making it compulsory, there will be a body of research data that can provide insights on threats to India and inform the government on strategies it can undertake to strengthen the nation’s cyber posture,” said Kumar Ritesh, founder and CEO, Cyfirma.The Internet Crime Report for 2019, released by the USA’s Internet Crime Complaint Centre of the Federal Bureau of Investigation (FBI), has revealed that India stands third in the world among top 20 countries that are victims of internet crimes.
Kumar attributes these numbers to Indian’s lack of basic cyber awareness. However, a poignant point is also the lack of a robust cybersecurity policy in India. Though the issue was touched upon by Prime Minister Narendra Modi during his Independence Day speech on Aug 15, 2020, not much movement has happened on that front.
“Cybersecurity is a very important aspect, which cannot be ignored. The government is alert on this and is working on a new, robust policy,” Modi said.The PM’s announcement was made in the backdrop of the government’s initiative to connect 1.5 lakh gram panchayats through an optical fiber network, thereby increasing the country’s internet connectivity.
With India pipped to take on the world with its IT prowess and increased digital integration the need for a robust policy is now more than ever.
Source: https://inc42.com/buzz/3-94-lakhs-and-counting-how-cyberattacks-are-a-worry-for-digital-india/
