
Net Neutrality: India
Introduction
In the age of digital technology, the concept of net neutrality has become more crucial for preserving the equity and openness of the internet. Thanks to net neutrality, all internet traffic is treated equally, without difference or preferential treatment. Thanks to this concept, users can freely access and distribute content, which promotes innovation, competition, and the democratisation of knowledge. India has seen controversy over net neutrality, which has led to a legal battle to protect an open internet. In this blog post, we’ll look at the challenges of the law and the efforts made to safeguard net neutrality in India.
Background on Net Neutrality in India
Net neutrality became a hot topic in India after a major telecom service provider suggested charging various fees for accessing different parts of the internet. Internet users, activists, and organisations in favour of an open internet raised concern over this. Millions of comments were made on the consultation document by the Telecom Regulatory Authority of India (TRAI) published in 2015, highlighting the significance of net neutrality for the country’s internet users.
Legal Battle and Regulatory Interventions
The battle for net neutrality in India acquired notoriety when TRAI released the “Prohibition of Discriminatory Tariffs for Data Services Regulations” in 2016. These laws, often known as the “Free Basics” prohibition, were created to put an end to the usage of zero-rating platforms, which exempt specific websites or services from data expenses. The regulations ensured that all data on the internet would be handled uniformly, regardless of where it originated.
But the legal conflict didn’t end there. The telecom industry challenged TRAI’s regulations, resulting in a flurry of legal conflicts in numerous courts around the country. The Telecom Regulatory Authority of India Act and its provisions of it that control TRAI’s ability to regulate internet services were at the heart of the legal dispute.
The Indian judicial system greatly helped the protection of net neutrality. The importance of non-discriminatory internet access was highlighted in 2018 when the Telecom Disputes Settlement and Appellate Tribunal (TDSAT) upheld the TRAI regulations and ruled in favour of net neutrality. The TDSAT ruling created a crucial precedent for net neutrality in India. In 2019, after several rounds of litigation, the Supreme Court of India backed the principles of net neutrality, declaring that it is a fundamental idea that must be protected. The nation’s legislative framework for preserving a free and open internet was bolstered by the ruling by the top court.
Ongoing Challenges and the Way Forward
Even though India has made great strides towards upholding net neutrality, challenges persist. Because of the rapid advancement of technology and the emergence of new services and platforms, net neutrality must always be safeguarded. Some practices, such as “zero-rating” schemes and service-specific data plans, continue to raise questions about potential violations of net neutrality principles. Regulatory efforts must be proactive and under constant watch to allay these worries. The regulatory organisation, TRAI, is responsible for monitoring for and responding to breaches of the net neutrality principles. It’s crucial to strike a balance between promoting innovation and competition and maintaining a free and open internet.
Additionally, public awareness and education on the issue are crucial for the continuation of net neutrality. By informing users of their rights and promoting involvement in the conversation, a more inclusive and democratic decision-making process is assured. Civil society organisations and advocacy groups may successfully educate the public about net neutrality and gain their support.
Conclusion
The legal battle for net neutrality in India has been a significant turning point in the campaign to preserve an open and neutral internet. A robust framework for net neutrality in the country has been established thanks to legislative initiatives and judicial decisions. However, due to ongoing challenges and the dynamic nature of technology, maintaining net neutrality calls for vigilant oversight and strong actions. An open and impartial internet is crucial for fostering innovation, increasing free speech, and providing equal access to information. India’s attempts to uphold net neutrality should motivate other nations dealing with similar issues. All parties, including politicians, must work together to protect the principles of net neutrality and ensure that the Internet is accessible to everyone.

Related Blogs
Introduction
Agentic AI systems are autonomous systems that can plan, make decisions, and take actions by interacting with external tools and environments. But they shift the nature of risk by blurring the lines among input, decision, and execution. A conventional model generates an output and stops. An agent takes input, makes plans, invokes tools, updates its state and repeats the cycle. This creates a system where decisions are continuously revised through interaction with external tools and environments, rather than being fixed at the point of input.
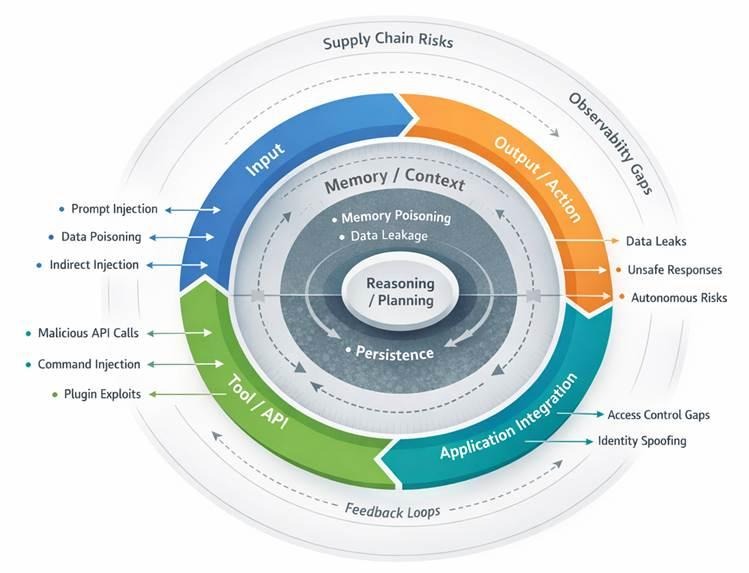
This means the attack surface expands in size and becomes more dynamic. Instead of remaining confined to components as in traditional computational systems, they spread in layers and can continue to grow through time. To understand this shift, the system can be analysed through functional layers such as inputs, memory, reasoning, and execution, while recognising that risk does not remain isolated within these layers but emerges through their interaction.
Agentic AI Attack Surface
A layered view of how risks emerge across input, memory, reasoning, execution, and system integration, including feedback loops and cross-system dependencies that amplify vulnerabilities.
Input Layer: Where Untrusted Data Becomes Control
The entry point of an agent is no longer one prompt. The documents, APIs, files, system logs and the outputs of other agents can now be considered input. This diversity is significant due to the fact that every source of input carries its own trust assumptions, and in the majority of cases, they are weak.
The most obvious threat is prompt injection, where inputs are treated as instructions rather than data. Since inputs are treated as instructions, a virus, a malicious webpage, or a document can contain instructions that override system goals without necessarily being detected as something harmful.
Indirect prompt injection extends this risk beyond direct user interaction. Instead of targeting the interface, attackers compromise the retrieval process by embedding malicious instructions within external data sources. When the agent retrieves and processes the data, it treats the embedded content as legitimate input. As a result, the attack is executed through normal reasoning processes, allowing the system to act on untrusted data without recognising the manipulation.
Data poisoning also occurs at runtime. In contrast to classical poisoning (where training data is manipulated), runtime poisoning distorts the agent’s perception of its environment as it runs. This can change decisions without causing apparent failures.
Obfuscation introduces another indirect attacker vector. Encoded instructions or complicated forms may bypass human review but remain readable to the model. This creates asymmetry whereby the system knows more about the attack than those operating it. Once compromised at this layer, the agent implements compromised instructions which affect downstream operations.
Context and Memory: Persistence of Influence
Agentic systems depend on memory to operate efficiently. They often retain context across sessions and frequently store information between sessions.
This introduces a different type of risk: persistence. Through memory poisoning, attackers can insert false or adversarial information into sorted context, which then influences future decisions. Unlike prompt injection, which is often limited to a single interaction, this effect carries forward. Over time, the agent begins to operate on a distorted internal state, shaping decisions in ways that may not be immediately visible.
Another issue is cross-session leakage. Information in a particular context may be replayed in a different context when memory is being shared or there is insufficient memory separation. This is specifically dangerous in those systems that combine retrieval and long-term storage. The context management in itself becomes a weakness. Agents are required to make decisions on what to retain and what to discard. This is susceptible to attackers who can flood the context or manipulate what is still visible and indirectly affect reasoning.
The underlying problem is structural. Memory turns data into a state. Once state is corrupted, the system cannot easily distinguish valid knowledge from adversarial influence.
The issue is structural. Memory converts temporary data into a persistent state. Once this state is weakened, the system cannot reliably separate valid information from adversarial influence, making recovery significantly more difficult.
Reasoning and Planning: Manipulating Intent Without Breaking Logic
The reasoning layer is where agentic AI stands apart from traditional systems. The model no longer reacts to inputs alone. It actively breaks down objectives, analyses alternatives, and ranks actions.
At the reasoning stage, the nature of risk shifts. The concern is no longer limited to injecting instructions, but to influencing how decisions are made. One example is goal manipulation, where the agent subtly reinterprets its objective and produces outcomes that are technically correct but strategically harmful. Reasoning hijacking operates within intermediate steps, altering how constraints are evaluated or how trade-offs are prioritised. The system may remain internally consistent, which makes such deviations difficult to detect.
Tool selection becomes a critical control point. Agents decide which tools to use and when, so influencing these choices can redirect execution without directly accessing the tools themselves. Hallucinations also take on a different role here. In static systems, they remain errors. In agentic systems, they can trigger actions. A perceived need or incorrect judgement can translate into real-world consequences.
This layer introduces probabilistic failure. The system is not fully weakened, but it is nudged towards decisions that appear reasonable yet are incorrect. The risk lies in how those decisions are justified.
Tool and Execution: When Decisions Gain Reach
Once an agent begins interacting with tools, its behaviour extends beyond the model into external systems. APIs, databases, and services become part of the execution path.
One key risk is the use of unauthorised tools. When agents operate with broad permissions, any manipulation of the upstream can be converted into real-world actions. This makes access control a central security concern. Command injection also takes a different form here. The agent generates commands based on its reasoning, so if that reasoning is compromised, the resulting actions may still appear valid despite being harmful.
External tool outputs introduce another risk. If these systems return corrupted or misleading data, the agent may accept it without verification and incorporate it into its decisions. It is also becoming increasingly reliant on third-part tools and plugins adds to this exposure. If these components are compromised, they can affect behaviour without directly attacking the core system, creating a supply-side risk.
At this stage, the agent effectively operates as an insider. It holds legitimate credentials and interacts with systems in expected ways, making misuse harder to identify.
Application and Integration: System-Level Exposure
Agentic systems rarely operate in isolation. They are embedded in larger environments, interacting with identity systems, business logic, and operational workflows.
Access control becomes a major vulnerability. Agents tend to operate across multiple systems with various permission models, creating irregularities that can be exploited. Risks also arise from identity and delegation. In case an agent is operating on behalf of a user, then any vulnerabilities in authentication or session management can allow attackers to assume that authority.
Workflow execution amplifies these risks. Agents can initiate multi-step processes such as transactions, updates, or approvals. Manipulating a single step can change the result of the entire workflow. As integrations increase, so do the number of interaction points, making cumulative risk harder to track.
At this layer, failures are not isolated. They propagate into business operations, making consequences harder to contain.
Output and Action: Where Failures Become Visible
The output layer is where failures become visible, though they rarely originate there.
Data leakage has been a key concern. Agents may disclose information they are allowed to access, especially when tasks boundaries are not clearly defined. Misinformation and unsafe outputs are also important, particularly when outputs directly influence actions or decisions.
Generated code and commands introduce execution risk. If outputs are used without validation, errors or manipulations can have system-level effects. The shift towards autonomous action increases this risk, as small upstream deviations can lead to significant consequences without human intervention. This layer reflects symptoms rather than root causes. Addressing it alone does not reduce the underlying risk.
Beyond Layers: The Missing Dimension
A layered view helps, but it does not capture the full picture. Agentic systems are defined by continuous interaction across layers.
The key missing dimension is the runtime loop. Inputs shape reasoning, reasoning drives action, and actions feed back into both reasoning and memory. These cycles create feedback loops, where small manipulations may escalate over time. This also reduces observability. With multiple interacting components, it becomes difficult to trace cause and effect or identify where failures originate.
Supply chain dependencies add another layer of risk. Models, datasets, APIs, and plugins each introduce their own points of failure. A compromise at any of these points can propagate across the system. The attack surface also includes governance. Weak supervision, unclear responsibility, or excessive autonomy increase overall risk. Human control is not external to the system; it is part of its security.
Conclusion: Structuring the Attack Surface
Agentic AI expands the attack surface beyond traditional systems. It is both recursive and stateful. Risk does not just accumulate across layers; it moves and changes as the system operates.
Any useful representation must go beyond a linear stack. It should capture feedback loops, persistent state, and cross-layer dependencies that characterise the way these systems actually behave. The system is not a pipeline but a cycle. That is where both its capability and its risk emerge.
Executive Summary
Iran’s Supreme Leader Ayatollah Ali Khamenei was reportedly killed in a major attack carried out by Israel and the United States, with claims circulating that Iranian state media confirmed his death early Sunday morning. Amid these claims, a video is being widely shared on social media. The viral video shows a body trapped under debris. Users sharing the clip claim that the body seen in the footage is that of Ayatollah Ali Khamenei. However, research conducted by CyberPeace found the viral claim to be false. Our research revealed that the video is not authentic but AI-generated.
Claim:
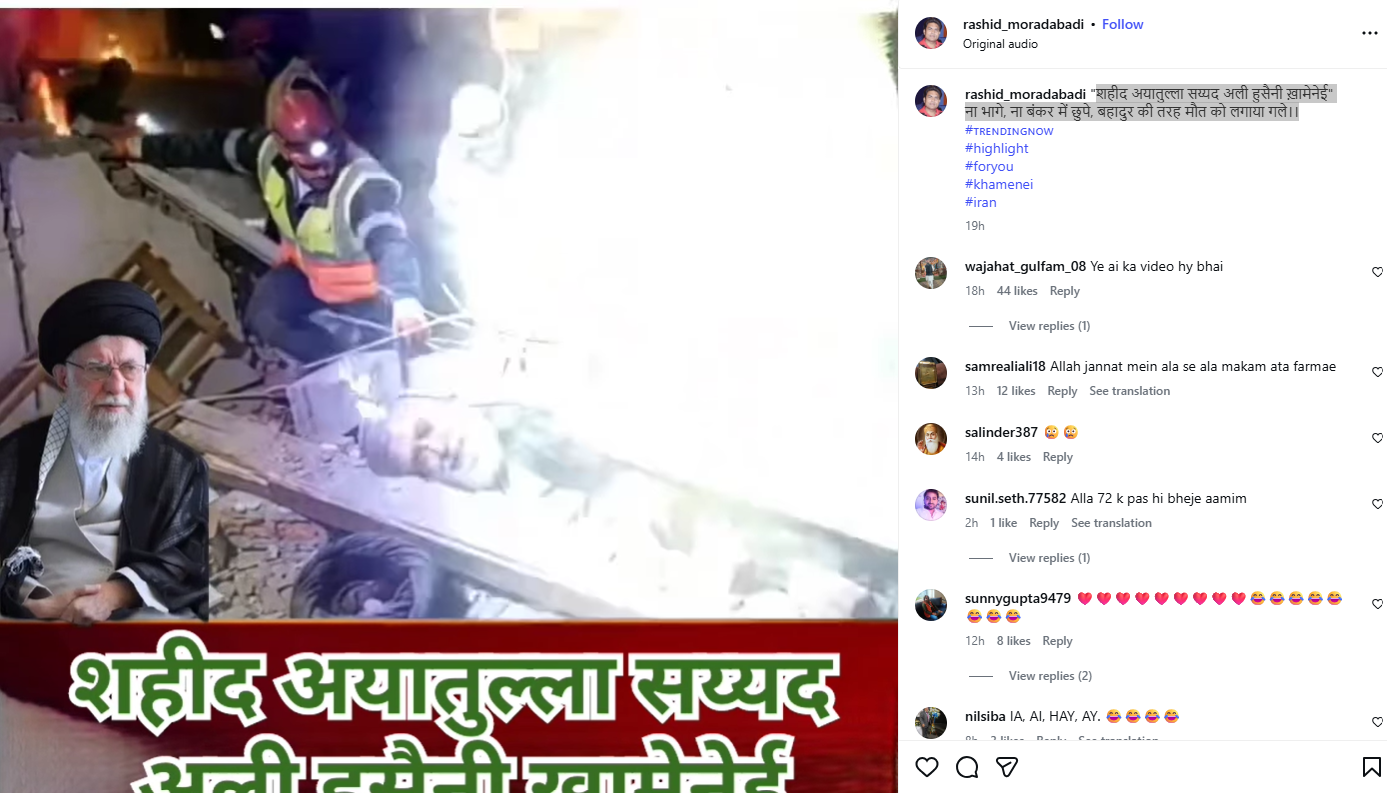
On March 1, 2026, an Instagram user shared the viral video with the caption: “Shaheed Ayatollah Sayyid Ali Hosseini Khamenei — Neither fled nor hid in a bunker, embraced death like a brave man.” The link to the post and its archived version are provided below along with a screenshot.
Fact Check:
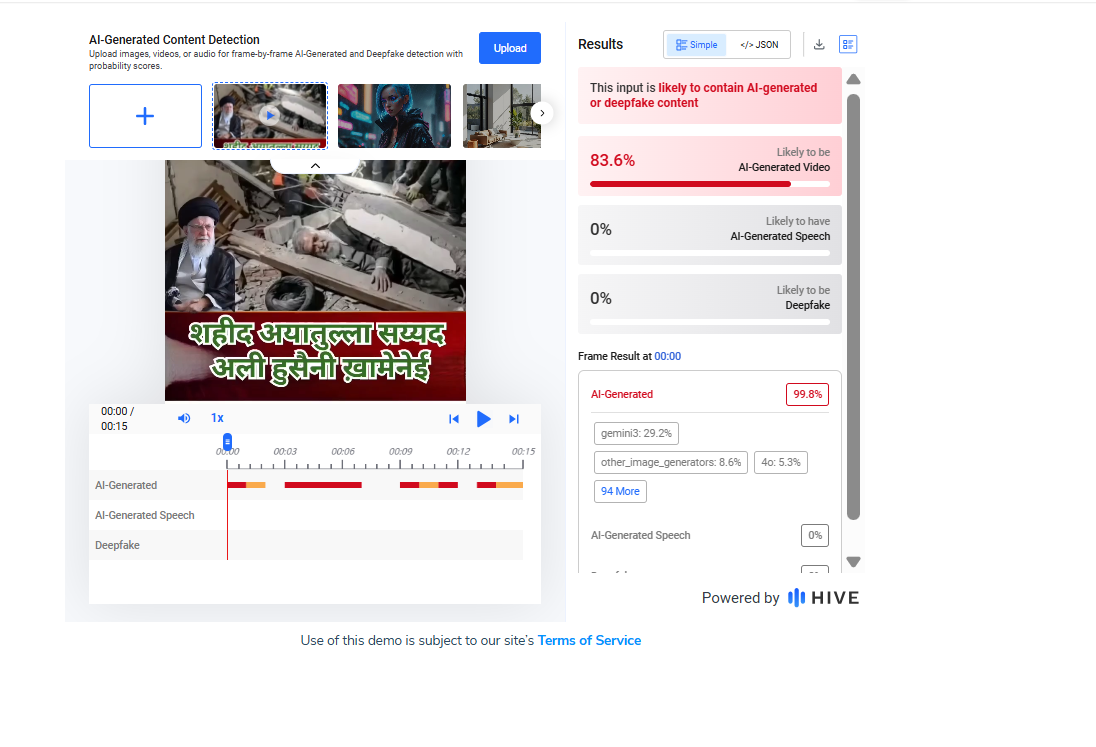
Upon closely examining the viral video, we noticed several visual irregularities and technical inconsistencies. This raised suspicion about its authenticity. We then scanned the video using the AI detection tool Hive Moderation. The results indicated that approximately 83 percent of the content showed signs of being AI-generated.
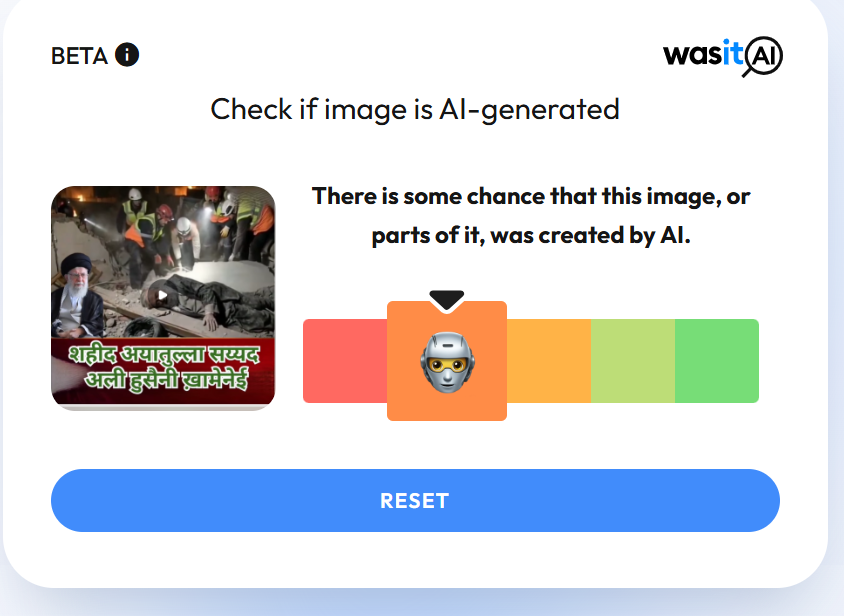
To further verify the claim, we also analyzed the video using another AI detection tool, WasItAI. The findings similarly suggested that the video was generated using artificial intelligence.
Conclusion:
Our research establishes that the viral video is not real. It has been artificially generated using AI and is being shared with misleading claims.

India’s online gaming industry has grown at lightning speed, drawing millions of users across age groups. From casual games and e-sports to fantasy leagues and online poker, digital entertainment has become both a social and economic phenomenon. But with this growth came rising concerns of addiction, financial loss, misleading ads, and even criminal misuse of gaming platforms for illegal betting. To address these concerns, the Government of India introduced the Promotion and Regulation of Online Gaming Act and draft Rules in October 2025. While the Act represents a crucial step toward accountability and user protection, it also raises difficult questions about freedom, innovation, and investor confidence.
The Current Legal Framework
The 2025 Act, along with corresponding changes in the Information Technology and GST laws, aims to create a safer and more transparent gaming environment.
1. Ban on real-money games:
Any online game where money is involved, whether it’s entry fees, bets, or prizes, is now banned, regardless of whether it is based on skill or chance. As a result, previously permitted formats such as fantasy sports, rummy, and poker once defended as “games of skill” now fall within the category of banned activities.
2. Promotion of e-sports and social gaming
Not all gaming is banned. Casual games, e-sports, and social games that don’t involve money are fully allowed. The government is encouraging these as part of India’s growing digital economy.
3. Advertising and financial restrictions: Banks, payment gateways, and advertisers cannot facilitate or promote real-money games. Any platform offering deposits or prize pools can be blocked.
4. Central regulatory authority: The law establishes a national body to classify games, monitor compliance, and address complaints. It has the power to order the locking of violative content and websites.
Why Regulation Was Needed
The push for regulation came after a surge in online betting scams, debt-related suicides, and disputes about whether certain apps were skill-based or chance-based. State governments had taken conflicting positions, some banning, others licensing such games. Meanwhile, offshore gaming apps operated freely in India’s grey market.
The 2025 Act thus attempts to impose uniformity, protect minors, and bring moral and fiscal discipline to a rapidly expanding digital frontier. Its underlying philosophy resembles that of the Digital Personal Data Protection Act, encouraging responsible use of technology rather than an unregulated free-for-all.
Key Challenges and Gaps
(a) Clarity of Definitions
The Act bans all real-money games, ignoring the difference between skill-based games and chance-based games. This could lead to legal challenges under Article 19(1)(g), which protects the right to do business. Games like rummy or fantasy cricket, which need real skill, arguably shouldn’t be banned outright
(b) Weak Consumer and Child Protection
Although age verification and KYC are mandated, compliance at the user-end remains uncertain. India needs a Responsible Gaming Code covering:
- Spending limits and cooling-off periods;
- Self-exclusion options;
- Transparent disclosure of odds; and
- Algorithmic fairness audits.
These measures can help mitigate addiction and prevent exploitation of minors.
(c) Federal Conflicts
“Betting and gambling” fall within the State List under India’s Constitution, yet the 2025 Act seeks national uniformity. States like Tamil Nadu and Karnataka already have independent bans. Without harmonisation, legal disputes between state and central authorities could multiply. A cooperative federal framework allowing states to adopt central norms voluntarily could offer flexibility without fragmentation.
(d) Regulatory Transparency
The gaming regulator has a lot of power, like deciding which games are allowed and blocking websites. But it’s not clear who chooses its members or how people can challenge its decisions. Including court oversight, public input, and regular reporting would make the regulator fairer and more reliable.
What’s Next for India’s Online Gaming
India’s online gaming scene is at a turning point. Banning all money-based games might reduce risks, but it also slows innovation and limits opportunities. A better approach could be to license skill-based or low-risk games with proper KYC and audits, set up a Responsible Gaming Charter with input from government, industry, and civil society, and create rules for offshore platforms targeting Indian players. Player data should be protected under the Digital Personal Data Protection Act, 2023, and the law should be reviewed every few years to keep up with new tech like the metaverse, NFTs, and AI-powered games.
Conclusion
CyberPeace has already provided its detailed feedback to MEITy as on 30th October, 2025 hopes the finalised rules are released soon with the acknowledgment of the challenges discussed. The Promotion and Regulation of Online Gaming Act, 2025, marks an important turning point since this is India’s first serious attempt to bring order to a chaotic digital arena. The goal is to keep players safe, stop crime, and hold platforms accountable. But the tricky part is moving away from blanket bans. We need rules that let new ideas grow, respect people’s rights, and keep players safe. With a few smart changes and fair enforcement, India could have a gaming industry that’s safe, responsible, and ready to compete globally.
References
- https://ssrana.in/articles/indias-online-gaming-bill-2025-regulation-prohibition-and-the-future-of-digital-play/
- https://www.google.com/amp/s/m.economictimes.com/news/economy/policy/new-online-gaming-law-takes-effect-money-games-banned-from-today/amp_articleshow/124255401.cms
- https://www.google.com/amp/s/timesofindia.indiatimes.com/technology/tech-news/government-proposes-to-make-violation-of-online-money-game-rules-non-bailable-draft-rules-ban-/amp_articleshow/124277740.cms
- https://www.egf.org.in/
- https://www.pib.gov.in/PressNoteDetails.aspx?NoteId=155075&ModuleId=3
