
#FactCheck: Phishing Scam on Jio is offering a ₹700 Holi reward through a promotional link
Executive Summary:
A viral post currently circulating on various social media platforms claims that Reliance Jio is offering a ₹700 Holi gift to its users, accompanied by a link for individuals to claim the offer. This post has gained significant traction, with many users engaging in it in good faith, believing it to be a legitimate promotional offer. However, after careful investigation, it has been confirmed that this post is, in fact, a phishing scam designed to steal personal and financial information from unsuspecting users. This report seeks to examine the facts surrounding the viral claim, confirm its fraudulent nature, and provide recommendations to minimize the risk of falling victim to such scams.
Claim:
Reliance Jio is offering a ₹700 reward as part of a Holi promotional campaign, accessible through a shared link.

Fact Check:
Upon review, it has been verified that this claim is misleading. Reliance Jio has not provided any promo deal for Holi at this time. The Link being forwarded is considered a phishing scam to steal personal and financial user details. There are no reports of this promo offer on Jio’s official website or verified social media accounts. The URL included in the message does not end in the official Jio domain, indicating a fake website. The website requests for the personal information of individuals so that it could be used for unethical cyber crime activities. Additionally, we checked the link with the ScamAdviser website, which flagged it as suspicious and unsafe.


Conclusion:
The viral post claiming that Reliance Jio is offering a ₹700 Holi gift is a phishing scam. There is no legitimate offer from Jio, and the link provided leads to a fraudulent website designed to steal personal and financial information. Users are advised not to click on the link and to report any suspicious content. Always verify promotions through official channels to protect personal data from cybercriminal activities.
- Claim: Users can claim ₹700 by participating in Jio's Holi offer.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Executive Summary
A video circulating on social media allegedly shows Uttar Pradesh Chief Minister Yogi Adityanath criticizing Bollywood actor Shah Rukh Khan and asking people not to watch his films. Users sharing the clip claim that these statements are recent. CyberPeace’s research has found the claim to be misleading. research revealed that the video is from 2015, long before Yogi Adityanath became the Chief Minister of Uttar Pradesh. At that time, he was serving as a Member of Parliament from Gorakhpur.
Claim
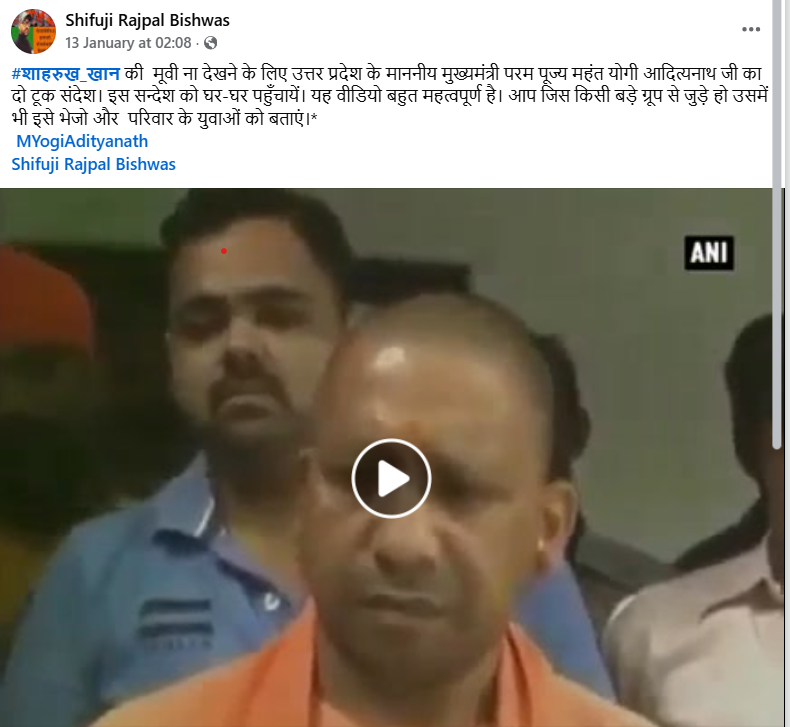
On January 13, 2026, a Facebook user shared the video with the caption: "A clear message from the Hon’ble Chief Minister of Uttar Pradesh, Param Pujya Mahant Yogi Adityanath, urging people not to watch Shah Rukh Khan’s movie. Share this message widely, send it to all groups you are part of, and inform the youth in your family."
Fact Check:
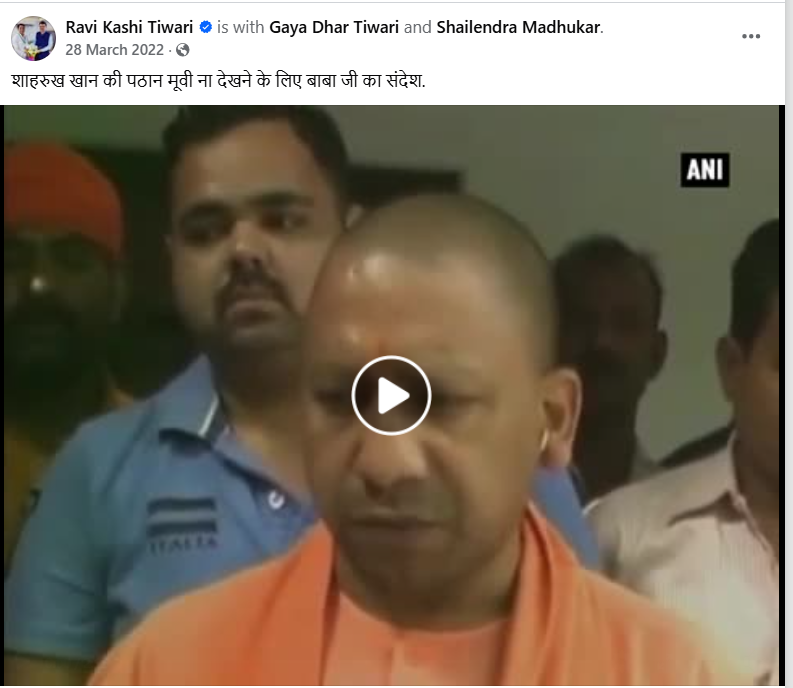
To verify the claim, keyframes from the viral video were extracted and reverse-searched using Google Lens. The same video was found in a Facebook post dated March 28, 2022, where it was shared with the caption: "Baba Ji’s message to not watch Shah Rukh Khan’s ‘Pathaan’ movie."
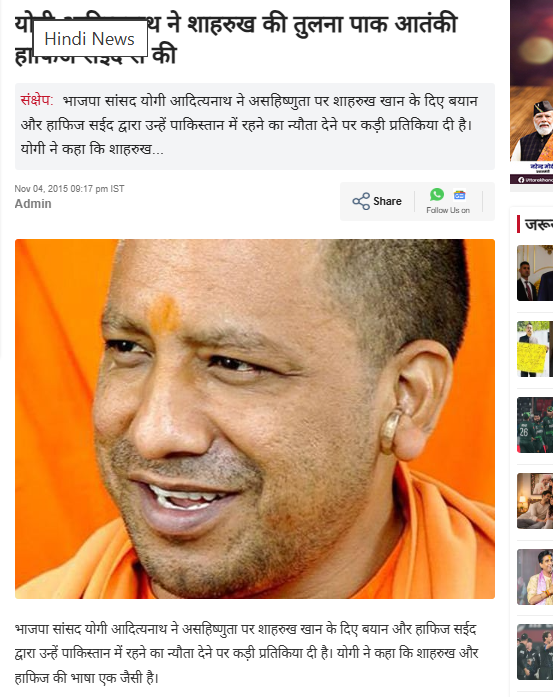
Further research traced the video to Aaj Tak’s website, which reported on November 4, 2015, that then-BJP MP Yogi Adityanath criticized Shah Rukh Khan, comparing his language to that of terrorist Hafiz Saeed, stating that there was no difference in their statements.
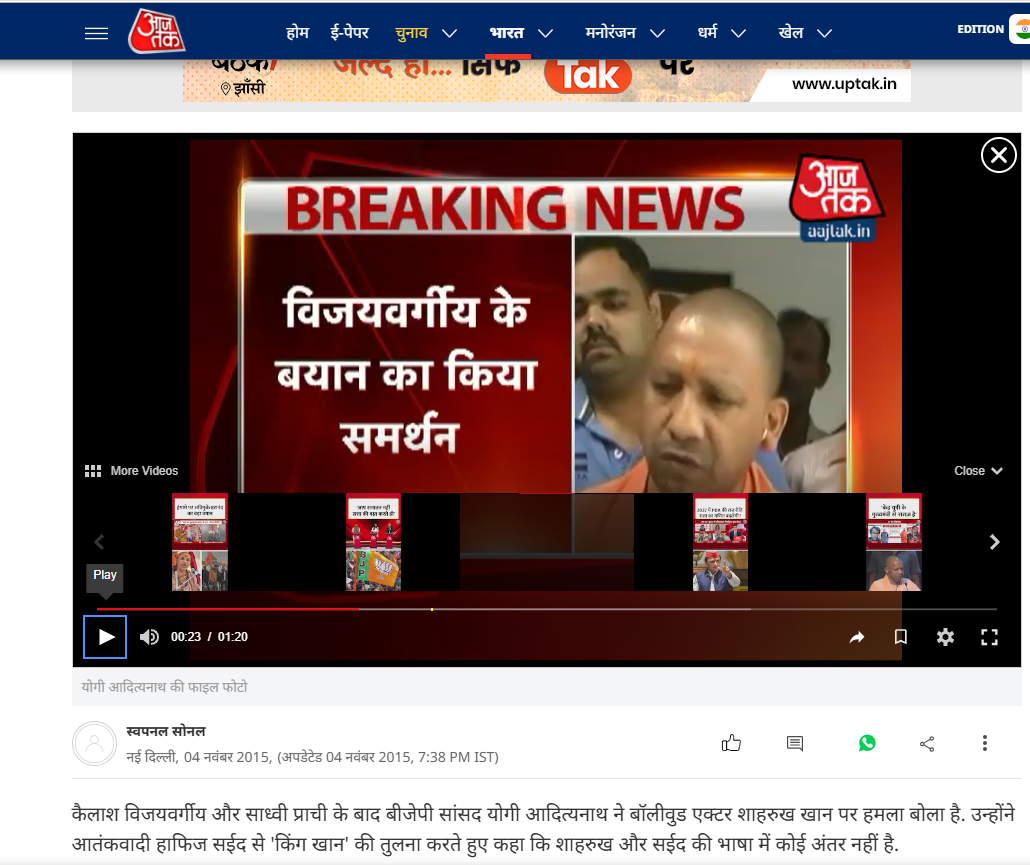
A Live Hindustan report from the same date confirmed that Yogi Adityanath had strongly reacted to Shah Rukh Khan’s comments on rising intolerance in India and Hafiz Saeed’s invitation for him to stay in Pakistan. The reports make it clear that Yogi Adityanath criticized Shah Rukh Khan in 2015 by highlighting the similarity between his statements and those of Hafiz Saeed. At the same time, Shah Rukh Khan had highlighted growing intolerance in the country, citing incidents where filmmakers, scientists, and authors were returning awards, describing it as a sign of “deep intolerance” in India.
Conclusion:
Our research found that the statement attributed to Chief Minister Yogi Adityanath circulating on social media is not recent. The video dates back to 2015, a time when Yogi Adityanath was not yet the Chief Minister of Uttar Pradesh.

Starting on 16th February 2025, Google changed its advertisement platform program policy. It will permit advertisers to employ device fingerprinting techniques for user tracking. Organizations that use their advertising services are now permitted to use fingerprinting techniques for tracking their users' data. Originally announced on 18th December 2024, this rule change has sparked yet another debate regarding privacy and profits.
The Issue
Fingerprinting is a technique that allows for the collection of information about a user’s device and browser details, ultimately enabling the creation of a profile of the user. Not only used for or limited to targeting advertisements, data procured in such a manner can be used by private entities and even government organizations to identify individuals who access their services. If information on customization options, such as language settings and a user’s screen size, is collected, it becomes easier to identify an individual when combined with data points like browser type, time zone, battery status, and even IP address.
What makes this technique contentious at the moment is the lack of awareness regarding the information being collected from the user and the inability to opt out once permissions are granted.
This is unlike Google’s standard system of data collection through permission requests, such as accepting website cookies—small text files sent to the browser when a user visits a particular website. While contextual and first-party cookies limit data collection to enhance user experience, third-party cookies enable the display of irrelevant advertisements while users browse different platforms. Due to this functionality, companies can engage in targeted advertising.
This issue has been addressed in laws like the General Data Protection Regulation (GDPR) of the European Union (EU) and the Digital Personal Data Protection (DPDP) Act, 2023 (India), which mandate strict rules and regulations regarding advertising, data collection, and consent, among other things. One of the major requirements in both laws is obtaining clear, unambiguous consent. This also includes the option to opt out of previously granted permissions for cookies.
However, in the case of fingerprinting, the mechanism of data collection relies on signals that users cannot easily erase. While clearing all data from the browser or refusing cookies might seem like appropriate steps to take, they do not prevent tracking through fingerprinting, as users can still be identified using system details that a website has already collected. This applies to all IoT products as well. People usually do not frequently change the devices they use, and once a system is identified, there are no available options to stop tracking, as fingerprinting relies on device characteristics rather than data-collecting text files that could otherwise be blocked.
Google’s Changing Stance
According to Statista, Google’s revenue is largely made up of the advertisement services it provides (amounting to 264.59 billion U.S. dollars in 2024). Any change in its advertisement program policies draws significant attention due to its economic impact.
In 2019, Google claimed in a blog post that fingerprinting was a technique that “subverts user choice and is wrong.” It is in this context that the recent policy shift comes as a surprise. In response, the ICO (Information Commissioner’s Office), the UK’s data privacy watchdog, has stated that this change is irresponsible. Google, however, is eager to have further discussions with the ICO regarding the policy change.
Conclusion
The debate regarding privacy in targeted advertising has been ongoing for quite some time. Concerns about digital data collection and storage have led to new and evolving laws that mandate strict fines for non-compliance.
Google’s shift in policy raises pressing concerns about user privacy and transparency. Fingerprinting, unlike cookies, offers no opt-out mechanism, leaving users vulnerable to continuous tracking without consent. This move contradicts Google’s previous stance and challenges global regulations like the GDPR and DPDP Act, which emphasize clear user consent.
With regulators like the ICO expressing disapproval, the debate between corporate profits and individual privacy intensifies. As digital footprints become harder to erase, users, lawmakers, and watchdogs must scrutinize such changes to ensure that innovation does not come at the cost of fundamental privacy rights
References
- https://www.techradar.com/pro/security/profit-over-privacy-google-gives-advertisers-more-personal-info-in-major-fingerprinting-u-turn
- https://www.ccn.com/news/technology/googles-new-fingerprinting-policy-sparks-privacy-backlash-as-ads-become-harder-to-avoid/
- https://www.emarketer.com/content/google-pivot-digital-fingerprinting-enable-better-cross-device-measurement
- https://www.lewissilkin.com/insights/2025/01/16/google-adopts-new-stance-on-device-fingerprinting-102ju7b
- https://www.lewissilkin.com/insights/2025/01/16/ico-consults-on-storage-and-access-cookies-guidance-102ju62
- https://www.bbc.com/news/articles/cm21g0052dno
- https://www.techradar.com/features/browser-fingerprinting-explained
- https://fingerprint.com/blog/canvas-fingerprinting/
- https://www.statista.com/statistics/266206/googles-annual-global-revenue/#:~:text=In%20the%20most%20recently%20reported,billion%20U.S.%20dollars%20in%202024

Introduction
Pagers were commonly utilized in the late 1990s and early 2000s, especially in fields that needed fast, reliable communication and swift alerts and information sharing. Pagers typically offer a broader coverage range, particularly in remote areas with limited cellular signals, which enhances their dependability. They are simple electronic devices with minimal features, making them easy to use and less prone to technical issues. The decline in their use has been caused by the rise of mobile phones and their extensive features, offering more advanced communication options like voice calls, text messages, and internet access. Despite this, pagers are still used in some specific industries.
A shocking incident occurred on 17th September 2014, where thousands of pager devices exploded within seconds across Lebanon in a synchronized attack, targeting the US-designated terror group Hezbollah. The explosions killed at least 9 and injured over 2,800 individuals in the country that has been caught up in the Israel-Palestine tensions in its backyard.
The Pager Bombs Incident
On Tuesday, 17th September 2024, hundreds of pagers carried by Hezbollah members in Lebanon exploded in an unprecedented attack, surpassing a series of covert assassinations and cyber-attacks in the region over recent years. The Iran-backed militant group claimed the wireless devices began to explode around 3:30 p.m., local time, in a targeted attack on Hezbollah operatives. The pagers that exploded were new and had been purchased by Hezbollah in recent months. Experts say the explosions underscore Hezbollah's vulnerability as its communication network was compromised to deadly effect. Several areas of the country were affected, particularly Beirut's southern suburbs, a populous area that is a known Hezbollah stronghold. At least 9 people were killed, including a child, and about 2,800 people were wounded, overwhelming Lebanese hospitals.
Second Wave of Attack
As per the most recent reports, the next day, following the pager bombing incident, a second wave of blasts hit Beirut and multiple parts of Lebanon. Certain wireless devices such as walkie-talkies, solar equipment, and car batteries exploded, resulting in at least 9 people killed and 300 injured, according to the Lebanese Health Ministry. The attack is said to have embarrassed Hezbollah, incapacitated many of its members, and raised fears about a greater escalation of hostilities between the Iran-backed Lebanese armed group and Israel.
A New Kind of Threat - ‘Cyber-Physical’ Attacks
The incident raises serious concerns about physical tampering with daily-use electronic devices and the possibility of triggering a new age of warfare. This highlights the serious physical threat posed, wherein even devices such as smartwatches, earbuds, and pacemakers could be vulnerable to physical tampering if an attacker gains physical access to them. We are potentially looking at a new age of ‘cyber-physical’ threats where the boundaries between the digital and the physical are blurring rapidly. It raises questions about unauthorised access and manipulation targeting the physical security of such electronic devices. There is a cause for concern regarding the global supply chain across sectors, if even seemingly-innocuous devices can be weaponised to such devastating effect. Such kinds of attacks are capable of causing significant disruption and casualties, as demonstrated by pager bombings in Lebanon, which resulted in numerous deaths and injuries. It also raises questions on the regulatory mechanism and oversights checks at every stage of the electronic device lifecycle, from component manufacturing to the final assembly and shipment or supply. This is a grave issue because embedding explosives and doing malicious modifications by adversaries can turn such electronic devices into weapons.
CyberPeace Outlook
The pager bombing attack demonstrates a new era of threats in warfare tactics, revealing the advanced coordination and technical capabilities of adversaries where they have weaponised the daily use of electronic devices. They have targeted the hardware security of electronic devices, presenting a serious new threat to hardware security. The threat is grave, and has understandably raised widespread apprehension globally. Such kind of gross weaponisation of daily-use devices, specially in the conflict context, also triggers concerns about the violation of International Humanitarian Law principles. It also raises serious questions on the liabilities of companies, suppliers and manufacturers of such devices, who are subject to regulatory checks and ensuring the authenticity of their products.
The incident highlights the need for a more robust regulatory landscape, with stricter supply chain regulations as we adjust to the realities of a possible new era of weaponisation and conflict expression. CyberPeace recommends the incorporation of stringent tracking and vetting processes in product supply chains, along with the strengthening of international cooperation mechanisms to ensure compliance with protocols regarding the responsible use of technology. These will go a long way towards establishing peace in the global cyberspace and restore trust and safety with regards to everyday technologies.
References:
1. https://indianexpress.com/article/what-is/what-is-a-pager-9573113/
5. https://www.theguardian.com/world/2024/sep/18/hezbollah-pager-explosion-lebanon-israel-gold-apollo
