
#FactCheck - "AI-Generated Image of UK Police Officers Bowing to Muslims Goes Viral”
Executive Summary:
A viral picture on social media showing UK police officers bowing to a group of social media leads to debates and discussions. The investigation by CyberPeace Research team found that the image is AI generated. The viral claim is false and misleading.

Claims:
A viral image on social media depicting that UK police officers bowing to a group of Muslim people on the street.


Fact Check:
The reverse image search was conducted on the viral image. It did not lead to any credible news resource or original posts that acknowledged the authenticity of the image. In the image analysis, we have found the number of anomalies that are usually found in AI generated images such as the uniform and facial expressions of the police officers image. The other anomalies such as the shadows and reflections on the officers' uniforms did not match the lighting of the scene and the facial features of the individuals in the image appeared unnaturally smooth and lacked the detail expected in real photographs.

We then analysed the image using an AI detection tool named True Media. The tools indicated that the image was highly likely to have been generated by AI.

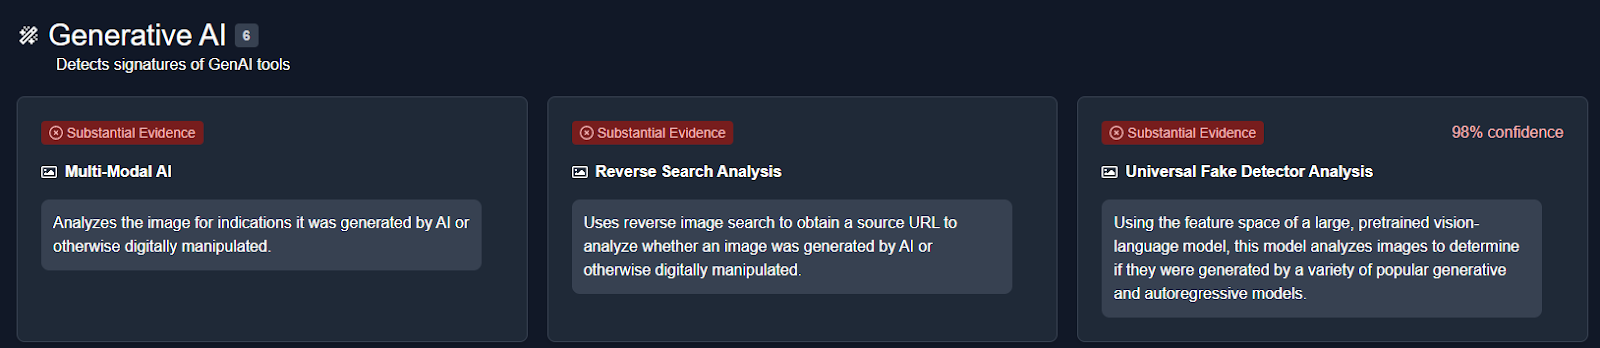

We also checked official UK police channels and news outlets for any records or reports of such an event. No credible sources reported or documented any instance of UK police officers bowing to a group of Muslims, further confirming that the image is not based on a real event.
Conclusion:
The viral image of UK police officers bowing to a group of Muslims is AI-generated. CyberPeace Research Team confirms that the picture was artificially created, and the viral claim is misleading and false.
- Claim: UK police officers were photographed bowing to a group of Muslims.
- Claimed on: X, Website
- Fact Check: Fake & Misleading

Related Blogs

Data localisation refers to restrictions in the data flow by limiting the physical storage and processing of data within a given jurisdiction’s boundaries.
An obvious benefit contributing to the importance of data localisation is the privacy benefits it offers. In addition to this, data localisation also has the potential to safeguard sensitive data and decrease the probability of cyber-attacks. In India, data localisation has become a key issue in the last decade due to the increase in the discourse for data privacy.
The Legal Framework in India
India passed the Digital Personal Data Protection Act of 2023 which directs the data fiduciaries (collectors and processors of digital personal data) to store the data of Indian citizens within India. This push for data localisation aligns with India’s position to enhance privacy, national security and regulatory control. It further requires data fiduciaries to adhere to the principles of data minimisation, purposeful limitation and consent of the data principles. Further, Section 17 of the Act prohibits the transfer of sensitive personal data to foreign jurisdictions unless they meet satisfactory privacy protection standards.
The Reserve Bank of India, via a circular for Payments Data Regulation in 2018, has mandated that all payment data be stored in India, though it can be processed abroad. It requires the telecom sector to ensure local storage and local processing of subscriber information. It further prohibits the transferring of subscribers’ account information overseas.
MeitY’s Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021, emphasise data localisation, specifically when it involves government or critical data. The main idea behind this is that data related to Indian citizens or government activities should remain accessible to Indian law enforcement agencies and is not subject to external jurisdiction.
Common Misinformation about Data Localisation and its Impact
Misconceptions fuel misinformation and influence public perception and policy debates. A common misconception is that all data must be stored in India. It should be noted that non-critical and non-sensitive data are not subject to localisation, and can be cleared for cross-border transfers under specific circumstances.
Another misconception is that data localisation alone ensures complete security. A robust cybersecurity approach, infrastructure and capabilities are what guarantee security and this holds true regardless of the location of where the data is stored.
The notion that small businesses and startups will suffer the most is untrue. While data localisation policies may lead to increased costs, they foster innovation in the domestic infrastructure and services. This potentially fuels development and innovation in these small businesses and startups. Claims that data localisation will stifle global business are unfounded.
Proper regulations for data transfers can help balance data flows, enabling international trade while ensuring data sovereignty.
Real Impact of Data Localisation
Data localisation impacts several domains and has both positive and negative outcomes.
- It can be a driver for investment in local data centres and infrastructure, thereby inducing employment generation and boosting the domestic economy. And in contrast, the compliance costs may rise especially for MNCs that need to maintain multiple data storage systems.
- It can expedite the growth of local technology ecosystems while encouraging innovation in cloud computing and data storage solutions. On the other hand, small businesses might face struggles to afford the required infrastructure updates and upgrades.
- Law enforcement agencies will be able to gain access to data more swiftly while avoiding lengthy processes such as the Mutual Legal Assistance Treaties (MLATs). However, it should be noted that storing data locally does not automatically ensure that they are immune from attacks and breaches.
- A balance between sovereignty and global partnerships is a challenge that emerges with data localisation. International Trade Relationships are vulnerable to data localisations where countries favour a free data flow. This can hamper foreign collaborations with companies that rely on global data systems.
CyberPeace Outlook
It is important to clear misinformation about data localisation, some strategies that can be undertaken are:
- Launching public awareness campaigns to educate the stakeholders about the real requirements and the benefits of data localisation. Misinformation about data restrictions and security guarantees should be tackled fairly quickly.
- A balanced approach that promotes local economic development while at the same time allowing for the necessary cross-border data flows and creating a flexible and friendly business environment is important.
- India should work on international frameworks to streamline the process of data-sharing with other nations. This would protect national interests while making global cooperation easier.
Conclusion
Data localisation in India presents a valuable opportunity to enhance privacy, bolster national security, and stimulate economic growth through local infrastructure investment. Yet, addressing common misconceptions is crucial; the belief that all data must be stored domestically or that localisation alone ensures security is misleading.
It’s vital to pair local data storage with robust cybersecurity measures and foster international cooperation. Supporting small businesses, which may face challenges due to localisation requirements, is equally important. By addressing misinformation, promoting flexible regulations, and working towards global data-sharing frameworks, India can effectively manage the complexities of data localisation, safeguarding national interests while encouraging innovation and economic development.
References
- https://www.thehindu.com/sci-tech/technology/are-data-localisation-requirements-necessary-and-proportionate/article66131957.ece
- https://carnegieendowment.org/research/2021/04/how-would-data-localization-benefit-india?lang=en
- https://www.rbi.org.in/commonperson/English/Scripts/FAQs.aspx?Id=2995
- https://www.meity.gov.in/writereaddata/files/Information%20Technology%20%28Intermediary%20Guidelines%20and%20Digital%20Media%20Ethics%20Code%29%20Rules%2C%202021%20%28updated%2006.04.2023%29-.pdf

Introduction
In India, the rights of children with regard to protection of their personal data are enshrined under the Digital Personal Data Protection Act, 2023 which is the newly enacted digital personal data protection law of India. The DPDP Act requires that for the processing of children's personal data, verifiable consent of parents or legal guardians is a necessary requirement. If the consent of parents or legal guardians is not obtained then it constitutes a violation under the DPDP Act. Under section 2(f) of the DPDP act, a “child” means an individual who has not completed the age of eighteen years.
Section 9 under the DPDP Act, 2023
With reference to the collection of children's data section 9 of the DPDP Act, 2023 provides that for children below 18 years of age, consent from Parents/Legal Guardians is required. The Data Fiduciary shall, before processing any personal data of a child or a person with a disability who has a lawful guardian, obtain verifiable consent from the parent or the lawful guardian. Section 9 aims to create a safer online environment for children by limiting the exploitation of their data for commercial purposes or otherwise. By virtue of this section, the parents and guardians will have more control over their children's data and privacy and they are empowered to make choices as to how they manage their children's online activities and the permissions they grant to various online services.
Section 9 sub-section (3) specifies that a Data Fiduciary shall not undertake tracking or behavioural monitoring of children or targeted advertising directed at children. However, section 9 sub-section (5) further provides room for exemption from this prohibition by empowering the Central Government which may notify exemption to specific data fiduciaries or data processors from the behavioural tracking or target advertising prohibition under the future DPDP Rules which are yet to be announced or released.
Impact on social media platforms
Social media companies are raising concerns about Section 9 of the DPDP Act and upcoming Rules for the DPDP Act. Section 9 prohibits behavioural tracking or targeted advertising directed at children on digital platforms. By prohibiting intermediaries from tracking a ‘child's internet activities’ and ‘targeted advertising’ - this law aims to preserve children's privacy. However, social media corporations contended that this limitation adversely affects the efficacy of safety measures intended to safeguard young users, highlighting the necessity of monitoring specific user signals, including from minors, to guarantee the efficacy of safety measures designed for them.
Social media companies assert that tracking teenagers' behaviour is essential for safeguarding them from predators and harmful interactions. They believe that a complete ban on behavioural tracking is counterproductive to the government's objectives of protecting children. The scope to grant exemption leaves the door open for further advocacy on this issue. Hence it necessitates coordination with the concerned ministry and relevant stakeholders to find a balanced approach that maintains both privacy and safety for young users.
Furthermore, the impact on social media platforms also extends to the user experience and the operational costs required to implement the functioning of the changes created by regulations. This also involves significant changes to their algorithms and data-handling processes. Implementing robust age verification systems to identify young users and protect their data will also be a technically challenging step for the various scales of platforms. Ensuring that children’s data is not used for targeted advertising or behavioural monitoring also requires sophisticated data management systems. The blanket ban on targeted advertising and behavioural tracking may also affect the personalisation of content for young users, which may reduce their engagement with the platform.
For globally operating platforms, aligning their practices with the DPDP Act in India while also complying with data protection laws in other countries (such as GDPR in Europe or COPPA in the US) can be complex and resource-intensive. Platforms might choose to implement uniform global policies for simplicity, which could impact their operations in regions not governed by similar laws. On the same page, competitive dynamics such as market shifts where smaller or niche platforms that cater specifically to children and comply with these regulations may gain a competitive edge. There may be a drive towards developing new, compliant ways of monetizing user interactions that do not rely on behavioural tracking.
CyberPeace Policy Recommendations
A balanced strategy should be taken into account which gives weightage to the contentions of social media companies as well as to the protection of children's personal information. Instead of a blanket ban, platforms can be obliged to follow and encourage openness in advertising practices, ensuring that children are not exposed to any misleading or manipulative marketing techniques. Self-regulation techniques can be implemented to support ethical behaviour, responsibility, and the safety of young users’ online personal information through the platform’s practices. Additionally, verifiable consent should be examined and put forward in a manner which is practical and the platforms have a say in designing the said verification. Ultimately, this should be dealt with in a manner that behavioural tracking and targeted advertising are not affecting the children's well-being, safety and data protection in any way.
Final Words
Under section 9 of the DPDP Act, the prohibition of behavioural tracking and targeted advertising in case of processing children's personal data - will compel social media platforms to overhaul their data collection and advertising practices, ensuring compliance with stricter privacy regulations. The legislative intent behind this provision is to enhance and strengthen the protection of children's digital personal data security and privacy. As children are particularly vulnerable to digital threats due to their still-evolving maturity and cognitive capacities, the protection of their privacy stands as a priority. The innocence of children is a major cause for concern when it comes to digital access because children simply do not possess the discernment and caution required to be able to navigate the Internet safely. Furthermore, a balanced approach needs to be adopted which maintains both ‘privacy’ and ‘safety’ for young users.
References
- https://www.meity.gov.in/writereaddata/files/Digital%20Personal%20Data%20Protection%20Act%202023.pdf
- https://www.firstpost.com/tech/as-govt-of-india-starts-preparing-rules-for-dpdp-act-social-media-platforms-worried-13789134.html#google_vignette
- https://www.business-standard.com/industry/news/social-media-platforms-worry-new-data-law-could-affect-child-safety-ads-124070400673_1.html
Executive Summary
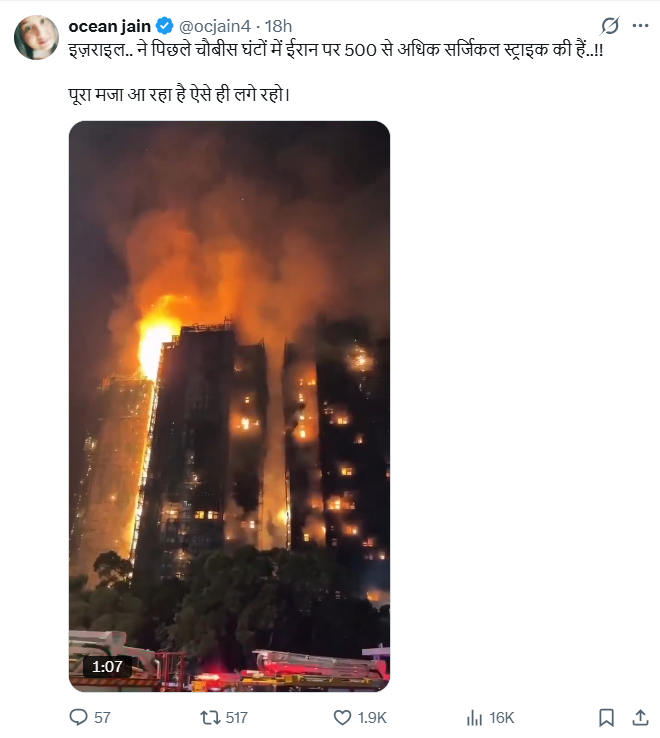
A video is being widely shared on social media with the claim that it shows the aftermath of a recent Israeli attack on Iran. The footage shows multiple residential high-rise buildings engulfed in flames, with thick plumes of smoke rising into the sky. Users sharing the video claim that Israel carried out more than 500 airstrikes on Iran. CyberPeace Research Wingresearch found the claim to be misleading. The viral video is not related to any Israeli attack on Iran. It actually shows a massive fire that broke out in a residential complex in Hong Kong in November 2025.
Claim:
An X user shared the viral video and wrote, “Israel has carried out more than 500 surgical strikes on Iran in the last 24 hours. Enjoying it thoroughly. Keep it up.”
Post link, archive link and screenshot can be seen below:
https://x.com/ocjain4/status/2064715707997413618?s=20
Fact Check:
To verify the authenticity of the viral video, we extracted keyframes and conducted a Google Lens search. During the research, we found the same footage on Reuters’ website, where it had been published on November 26, 2025.
Report link and screenshot can be seen below:
https://www.reuters.com/video/watch/idRW511126112025RP1/
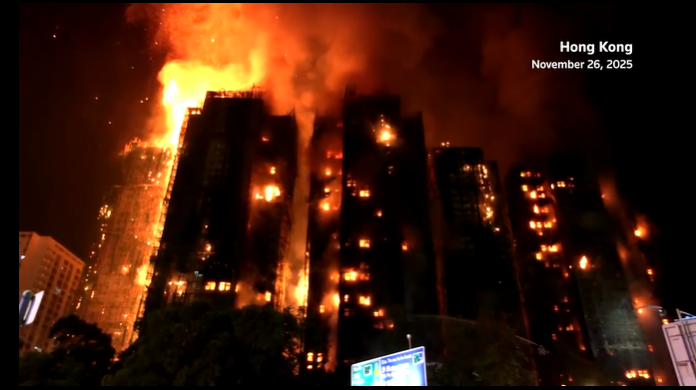
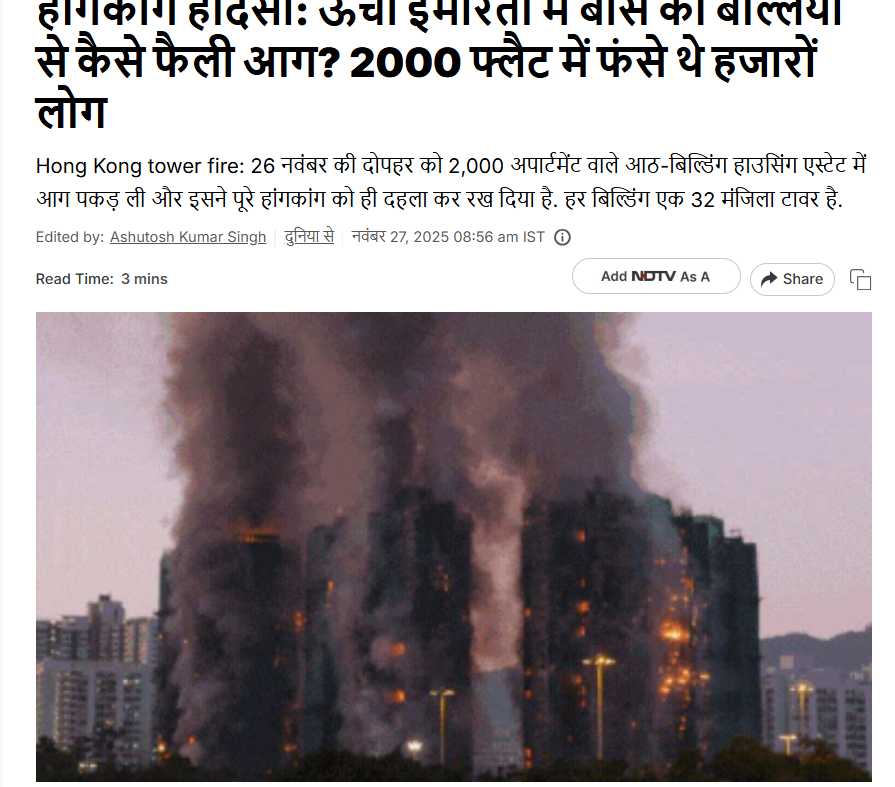
According to Reuters, the video shows a massive fire that engulfed multiple high-rise residential buildings in Hong Kong’s northern Tai Po district. The blaze claimed the lives of at least four people. Thick smoke could be seen billowing from the buildings as firefighters and emergency response teams worked to bring the fire under control.
After establishing the source of the video, we conducted a keyword search on Google and found a report published by NDTV on November 27, 2025, which also covered the incident.
Report link and screenshot can be seen below:
Conclusion:
Our research found that the viral video is not related to any Israeli attack on Iran. The footage actually shows a massive fire that broke out in residential buildings in Hong Kong in November 2025. Chinese President Xi Jinping had expressed condolences to the victims, including a firefighter who lost his life while on duty.

