
What’s Your New Year's Resolution?
2025 is knocking firmly at our door and we have promises to make and resolutions to keep. Time you make your list for the New Year and check it twice.
- Lifestyle targets 🡪 Check
- Family targets 🡪 Check
- Social targets 🡪 Check
Umm, so far so good, but what about your cybersecurity targets for the year? Hey, you look confused and concerned. Wait a minute, you do not have one, do you?
I get it. Though the digital world still puzzles, and sometimes outright scares us, we still are not in the ‘Take-Charge-Of-Your-Digital-Safety Mode. We prefer to depend on whatever software security we are using and keep our fingers crossed that the bad guys (read threat actors) do not find us.
Let me illustrate why cybersecurity should be one of your top priorities. You know that stress is a major threat to our continued good health, right? However, if your devices, social media accounts, office e-mail or network, or God forbid, bank accounts become compromised, would that not cause stress? Think about it and the probable repercussions and you will comprehend why I am harping on prioritising security.
Fret not. We will keep it brief as we well know you have 101 things to do in the next few days leading up to 01/01/2025. Just add cyber health to the list and put in motion the following:
- Install and activate comprehensive security software on ALL internet-enabled devices you have at home. Yes, including your smartphones.
- Set yourself a date to change and create separate unique passwords for all accounts. Or use the password manager that comes with all reputed security software to make life simpler.
- Keep home Wi-Fi turned off at night
- Do not set social media accounts to auto-download photos/documents
- Activate parental controls on all the devices used by your children to monitor and mentor them. But keep them apprised.
- Do not blindly trust anyone or anything online – this includes videos, speeches, emails, voice calls, and video calls. Be aware of fakes.
- Be aware of the latest threats and talk about unsafe cyber practices and behaviour often at home.
Short and sweet, as promised.
We will be back, with more tips, and answers to your queries. Drop us a line anytime, and we will be happy to resolve your doubts.
Ciao!

Related Blogs

Introduction
When Tamil Nadu Police arrested a man from Vellore in May 2026 on suspicion of being the point person helping Indian youth to be smuggled into cyber scam compounds in Cambodia, the papers led with the accused. They shouldn't have led with the accused but with the system. The arrest, one in a long string of them in Tamil Nadu, Madurai, and other states, is not simply another one-off policing victory. Rather, the arrest gives us an insight into a larger, darker world: an international criminal organisation that has successfully combined human trafficking and cybercrime, a new trend in criminality that specialists are calling 'cyber slavery.'
What Is Cyber Slavery?
“Cyber slavery” involves trafficking persons under the pretence of employment, forcing them into committing online fraud to serve criminal enterprises. Victims are not merely victims of the work they are forced to do; they are often turned into culprits as they become complicit in victimising others. Trafficked victims are compelled to participate in frauds targeted at unsuspecting victims all around the globe. These activities, organised into robust criminal schemes, involve victims of sex or labour trafficking who are forced into operating romance scams or the so-called "pig butchering" scams that defraud people of their investment in cryptocurrency, all in heavily secured complexes guarded with threats of violence and torture. The extent of the problem is enormous, with the UN Office of the High Commissioner for Human Rights estimating in a 2023 report that there are over 100,000 victims of cyber scam compounds in Cambodia and another 120,000 in Myanmar. Schemes throughout Southeast Asia were projected to commit as much as $39.9 billion in fraudulent schemes a year.
Why Southeast Asia? The Geography of Organised Crime
In order to answer why Cambodia, Myanmar, Laos, and the surrounding regions have developed into the cyber slavery hub of the world, we can draw together an array of structural reasons:
- Casino clampdown and crime diversification: Cambodia's ban on online gambling in 2019 broke down established casino-related criminal networks. This saw old casinos and Special Economic Zones turn into cyber scam compound operations.
- Corruption and state complicity: A pre-existing environment of corruption and involvement of politically linked figures permitted scamming networks to flourish, and the armed groups in the border areas of Myanmar are reportedly complicit in these operations through supplying land and protection for the networks to operate in.
- Poor governance in the border areas: The lack of state control in the frontier areas of Myanmar provided the criminal networks with a secure sanctuary in which they could operate with impunity and cross borders to escape crackdowns and move their operations.
- Post-pandemic growth: The economic stress associated with the COVID-19 pandemic led to an increase in the supply of vulnerable individuals available to fill the scam networks, as well as unprecedented profit margins on scams.
The Recruitment Pipeline: How Are Indian Youth Trapped?
The typical journey from an Indian town or village to a locked compound in Southeast Asia follows the same narrative:
- The bait: On platforms like Facebook, WhatsApp, and Telegram, gangs lure with posts of lucrative overseas employment for IT work, customer service, data entry, and digital marketing with attractive, albeit feasible, pay packages (Rs. 80,000 to Rs. 1.5 lakh per month) and destinations such as Thailand and Singapore added for a veneer of genuineness.
- The recruiters: Local agents who gain trust, arrange visas and flight tickets, and collect the application fees are key intermediaries. Cases registered in Vellore and Madurai hint at recruitment agents receiving a commission for each person successfully smuggled into a trap, linked to larger travel and immigration networks.
- The lie: Victims are assured that they will be working legitimately in Thailand, but on reaching the border and crossing over, they find themselves pushed into scam compounds in neighbouring countries and have their passports, mobile phones and devices confiscated, thus rendering any escape attempt futile.
- The trap: In the interim, fake interviews, false job promises and convincing flight tickets serve to maintain the facade until the victims are forced to participate in cyber-fraud schemes.
The Architecture of Coercion: Life Inside the Scam Compounds
It is in these compounds that the fates of the victims become known. Survivor accounts, investigations and UN human rights reports provide evidence of these circumstances. These compounds are often surrounded by barbed wire fences, monitored with cameras and heavily guarded. Once a potential victim is captured, they are stripped of their passports and any other electronic devices, preventing them from being able to contact the outside world or to escape. Workers are allocated stringent targets, ranging from the number of potential victims they must solicit for scams and the amount of money they must acquire through such scams. Failure to do so, or perceived disobedience, may lead to beatings, electroshock treatment, starvation and long periods in confinement. These beatings are supplemented with psychological torture, with scammers assuring their victims that they owe money for their journey, stay and training. This method of debt bondage keeps people at the compound even when the opportunity for escape is presented to them. The victims are then forced to take part in more complex online scams, which involve romance scams, fake investment scams, and impersonation scams using scripts and with supervision. In some cases, families will be encouraged to pay for their captive relatives' release by ransom, whereas those who refuse to comply or meet performance requirements may be sold and transferred to another compound as a piece of property within a transnational criminal network.
Cybercrime Is No Longer Just About Hacking
This emergency challenges the existing notion of cybercrime. The scam compound of Southeast Asia is not about a lonely hacker or a standalone breach; it is a form of organised cyber slavery in which trafficked individuals are made to commit financial fraud on an industrial level.
The probe of India's NIA found that recruitment is done in the Indian states of Bihar and Uttar Pradesh. Transport agents in Chennai and Madurai provide logistics, and Dubai and Bangkok act as transit points on the way to Cambodia, Laos, and Vietnam. It makes use of cryptocurrency wallets, shadow banking, and shell companies for the movement of funds across international borders. Companies such as the Huione Group has been accused of facilitating billions of dollars in financial transactions for scam infrastructure before receiving sanctions from the U.S.
To illustrate the threat landscape, the U.S. Treasury imposed sanctions on 19 entities spread across Myanmar and Cambodia and said that cyber scam operations looted $10 billion worth last year. Also, cryptocurrency transactions related to trafficking crimes jumped by 85% last year, which speaks to the expanding nature of the global criminal infrastructure.
India's Exposure: A National Vulnerability
The scale of exposure for India is large and expanding. The most likely victims are educated, and aspirational young men and women from Tier 2 and Tier 3 cities, seeking work abroad, which perfectly aligns with the primary target of such human trafficking networks.
Repeated incidents of people from Tamil Nadu falling victim to these networks have come to light. As far back as 2022, the chief minister wrote to the prime minister that close to 300 Indians, roughly 50 Tamils included, were being held in Myanmar. The Madurai-Cambodia case that came to light in 2026 revealed an entire network spanning Cambodia, Laos, and Vietnam, with authorities believing that thousands of Indians might have been trafficked there over the past three years. Such cases from Kerala, Karnataka, Andhra Pradesh, and some northern Indian states have been reported. Last year, India had to charter Air Force flights to rescue over 549 Indians from cyber scam centres along the Myanmar-Thailand border.
The Indian embassy in Phnom Penh assisted the Indian nationals along with the CBI, MEA, and NIA in the rescue of 67 Indians in September 2024; however, these operations are largely reactive in the face of the vast and evolving transboundary crisis.
Prevention
The best solution is awareness. The following are tangible signs that a job offer might be a lead to trafficking:
Red Flags within the job offer:
- Receiving unsolicited recruitment messages on WhatsApp, Telegram or Instagram from unknown numbers/contacts.
- Offer of unbelievably high salaries in undefined roles like ‘data entry,’ ‘online marketing’ or ‘customer service’ outside India.
- Request for upfront money to cover costs of visas, travel, accommodation, and training.
- Job offers to places in Thailand or Singapore involving complex transit routes through other countries.
- An interview process entirely through messaging apps, where the company has no real office address or registration number.
- Urgency and/or confidentiality required.
Verification:
- Check if the recruiter is registered on MEA's e-Migrate portal-this is a portal where MEA lists authorised overseas recruiters.
- Verify the authenticity of the company through its business registration with official registries in the foreign country.
- Contact the Indian Embassy/Consulate in that foreign country if something doesn't add up about the offer.
- Do not hand over your passport to your employer on arrival; it is standard practice for recruiters working as traffickers to confiscate it.
What to do if trapped:
- Contact the closest Indian embassy or consulate immediately.
- Call the MEA overseas helpline: 1800-11-3090.
- Lodge a report on the National Cybercrime Reporting Portal (cybercrime.gov.in).
Policy Imperatives
On their own, individual consciousness cannot undo such a massive criminal infrastructure. India has to enforce the Emigration Act rigorously, implement mandatory licensing of recruitment agents and create a specialised task force consisting of NIA, CBI, MEA and the states’ cybercrime units. Pre-departure orientations should also become mandatory for migrant workers who go to Southeast Asia. Globally, India needs to work more closely with Cambodia, Myanmar, Thailand and Laos via intel sharing protocols, victim repatriations and action against scam compounds. Financial probes must be on par with enforcement investigations to catch up with the perpetrators’ network, the cryptocurrency and hawala channels that facilitate money laundering and finance trafficking operations, as that would severely hit these networks.
Conclusion
This arrest of the recruiter in Vellore is just a small piece of a larger network. What we see in these instances is the marriage of cybercrime, trafficking, and financial fraud into a larger transnational ecosystem that systematically preys on the economic vulnerability of individuals. These young Indians are not simply falling for scams; they are being systematically targeted, recruited, trafficked, and forced into these criminal operations by a networked structure. The scam compounds in Cambodia and along the border of Myanmar and Thailand are only the end of a process that very likely starts with a convincing job offer on social media. Fighting cyber slavery will not be as simple as more arrests; we need education and international efforts, as well as policy responses that match the scope and scale of the problem.
References
- https://the420.in/78415-2vellore-man-cambodia-cyber-slavery-trafficking-case/
- https://the420.in/madhan-vadivel-cambodia-cyber-slavery-trafficking-racket-investigation/
- https://www.newsonair.gov.in/tamil-nadu-police-arrest-key-recruiter-in-cambodia-cyber-slavery-racket/
- https://kashmirdotcom.in/2026/05/16/cambodia-linked-human-trafficking-cyber-slavery-racket-nia-chargesheets-five-including-absconding-kingpin/
- https://www.aljazeera.com/news/2025/7/16/more-than-1000-arrested-in-cambodian-cyber-scam-raids
- https://www.pbs.org/newshour/world/why-southeast-asias-online-scam-industry-is-so-hard-to-shut-down
- https://www.cfr.org/articles/how-myanmar-became-global-center-cyber-scams
- https://www.amlrightsource.com/resources/scam-states-the-cybercrime-corruption-complex-in-southeast-asia-and-the-collapse-of-anti-money-laundering-enforcement
- https://newlinesinstitute.org/global-security-mil-priorities/cybercrimes-human-trafficking-and-cryptocurrency-in-southeast-asias-special-economic-zones/
- https://www.theweek.in/news/india/2026/03/21/lured-by-jobs-sold-into-slavery-indias-crackdown-on-cyber-trafficking-continues.html

Introduction
A hacking operation has corrupted data on Madhya Pradesh's e-Nagarpalika portal, a vital online platform for paying civic taxes that serves 413 towns and cities in the state. Due to this serious security violation, the portal has been shut down. The incident occurred in December 2023. This affects citizens' access to vital online services like possessions, water, and municipal tax payments, as well as the issuing of obituaries and certain documents offered via online portal. Ransomware which is a type of malware encodes and conceals a victim's files, and data making it inaccessible and unreachable unless the attacker is paid a ransom. When ransomware initially appeared, encryption was the main method of preventing individuals' data from such threats.
The Intrusion and Database Corruption: Exposing the Breach's Scope
The extent of the assault on the e-Nagarpalika portal was revealed by the Principal Secretary of the Urban Administration and Housing Department of Madhya Pradesh, in a startling revelation. Cybercriminals carried out a highly skilled assault that led to the total destruction of the data infrastructure covering all 413 of the towns for which the website was responsible.
This significant breach represents a thorough infiltration into the core of the electronic civic taxation system, not just an arrangement. Because of the attackers' nefarious intent, the data integrity was compromised, raising questions about the safeguarding of private citizen data. The extent of the penetration reaches vital city services, causing a reassessment of the current cybersecurity safeguards in place.
In addition to raising concerns about the privacy of personal information, the hacked information system casts doubt on the availability of crucial municipal services. Among the vital services affected by this cyberattack are marriage licenses, birth and death documents, and the efficient handling of possessions, water, and municipal taxes.
The weaknesses of electronic systems, which are the foundation of contemporary civic services, are highlighted by this incident. Beyond the attack's immediate interruption, citizens now have to deal with concerns about the security of their information and the availability of essential services. This tragedy is a clear reminder of the urgent need for robust safety safeguards as authorities work hard to control the consequences and begin the process of restoration.
Offline Protections in Place
The concerned authority informed the general population that the offsite data, which has been stored up on recordings every three days, is secure despite the online attack. This preventive action emphasises how crucial offline restores are to lessening the effects of these kinds of cyberattacks. The choice to keep the e-Nagarpalika platform offline until a certain time highlights how serious the matter is and how urgently extensive reconstruction must be done to restore the online services offer
Effect on Civic Services
The e-Nagarpalika website is crucial to providing online municipal services, serving as an invaluable resource for citizens to obtain necessary paperwork and carry out diverse transactions. Civic organisations have been told to function offline while the portal remains unavailable until the infrastructure is fully operational. This interruption prompts worries about possible delays and obstacles citizens face when getting basic amenities during this time.
Examination and Quality Control
Information technology specialists are working diligently to look into the computer virus and recover the website, in coordination with the Madhya Pradesh State Electronic Development Corporation Limited, the state's cyber police, and the Indian Computer Emergency Response Team (CERT-In). Reassuringly for impacted citizens, authorities note that there is currently no proof of data leaks arising from the hack.
Conclusion
The computerised attack on the e-Nagarpalika portal in Madhya Pradesh exposes the weakness of computer networks. It has affected the essential services to public services offered via online portal. The hack, which exposed citizen data and interfered with vital services, emphasises how urgently strong safety precautions are needed. The tragedy is a clear reminder of the need to strengthen technology as authorities investigate and attempt to restore the system. One bright spot is that the offline defenses in place highlight the significance of backup plans in reducing the impact of cyberattacks. The ongoing reconstruction activities demonstrate the commitment to protecting public data and maintaining the confidentiality of essential city operations.
References
- https://government.economictimes.indiatimes.com/tag/cyber+attack
- https://www.techtarget.com/searchsecurity/definition/ransomware#:~:text=Ransomware%20is%20a%20type%20of,accessing%20their%20files%20and%20systems.
- https://www.business-standard.com/india-news/mp-s-e-nagarpalika-portal-suffers-cyber-attack-data-corrupted-officials-123122300519_1.html
- https://www.freepressjournal.in/bhopal/mp-govts-e-nagar-palika-portal-hacked-data-of-over-400-cities-leaked
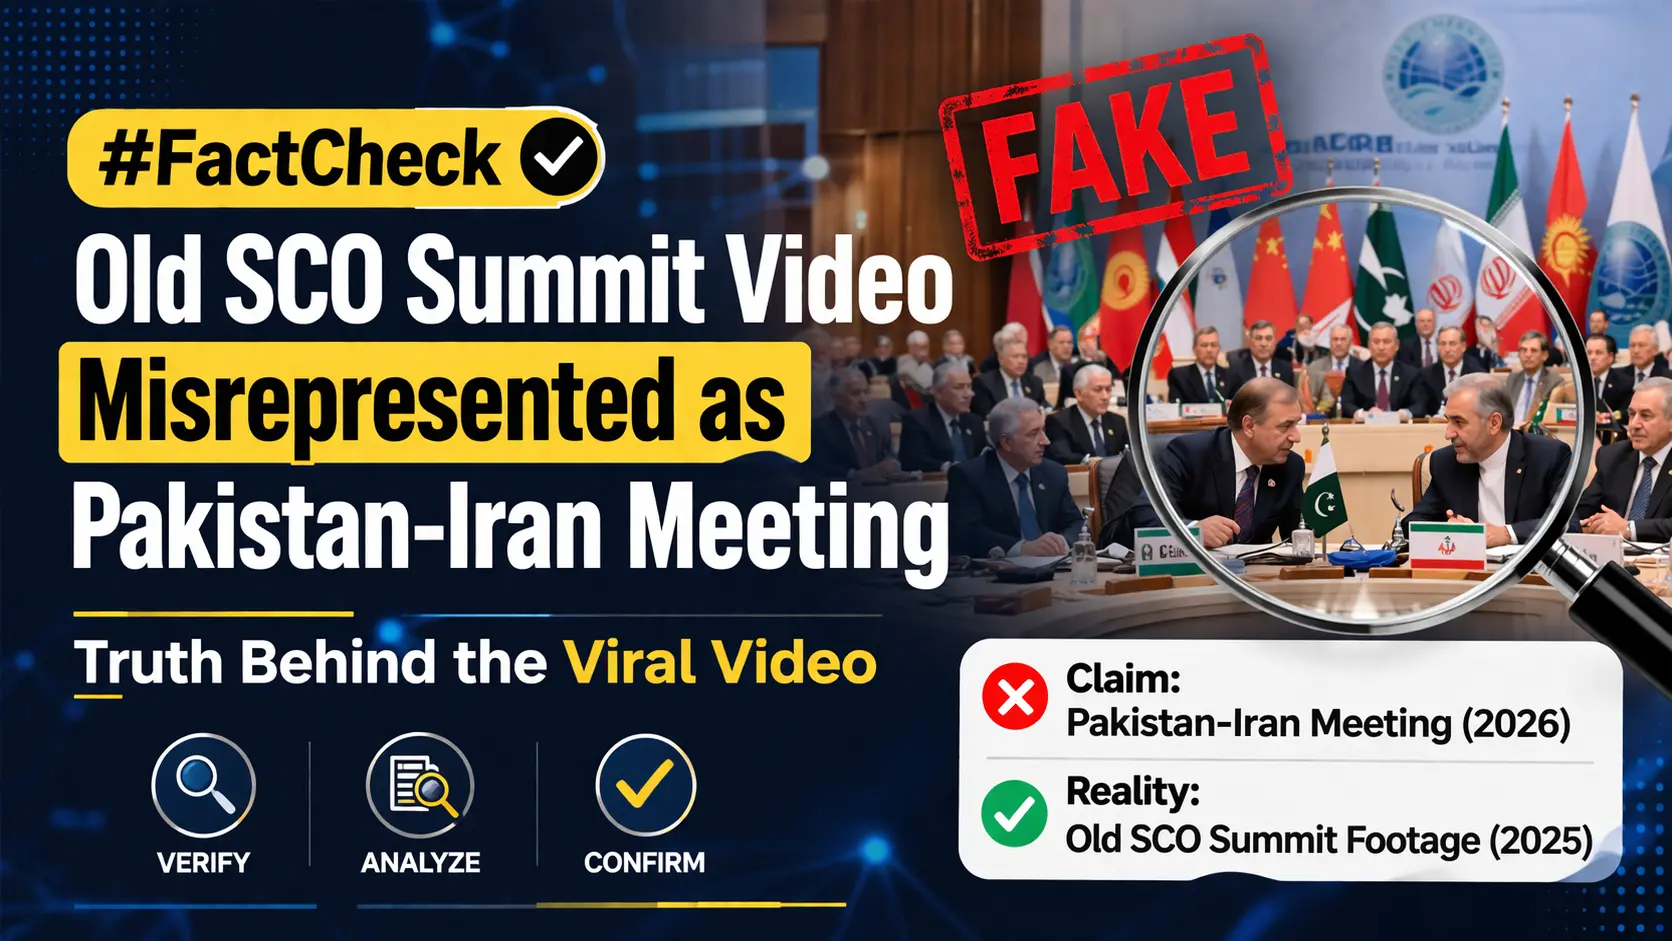
Executive Summary
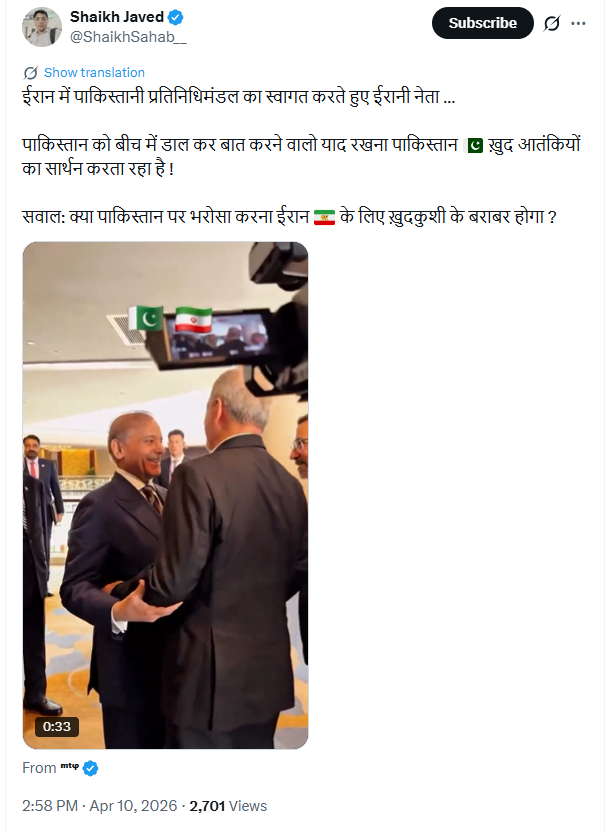
Amid reports of a two-week ceasefire announced on April 8, 2026, between the United States and Iran, and claims that Pakistan is facilitating peace talks between the two nations, a video showing leaders of Pakistan and Iran meeting has gone viral on social media. The video is being shared with the claim that Pakistani leaders received a grand welcome upon arriving in Iran for the April 11, 2026 talks. However, an research by the CyberPeace found the claim to be misleading. The viral video is not recent but dates back to September 2025.
Claim
An X (formerly Twitter) user shared the video on April 10, 2026, claiming that it shows Pakistani leaders being warmly welcomed in Iran.
Post link:
Fact Check
To verify the claim, we extracted keyframes from the viral video and conducted a reverse image search. This led us to the same video posted on a Facebook account named “Bhurgri Siddique” on September 1, 2025.
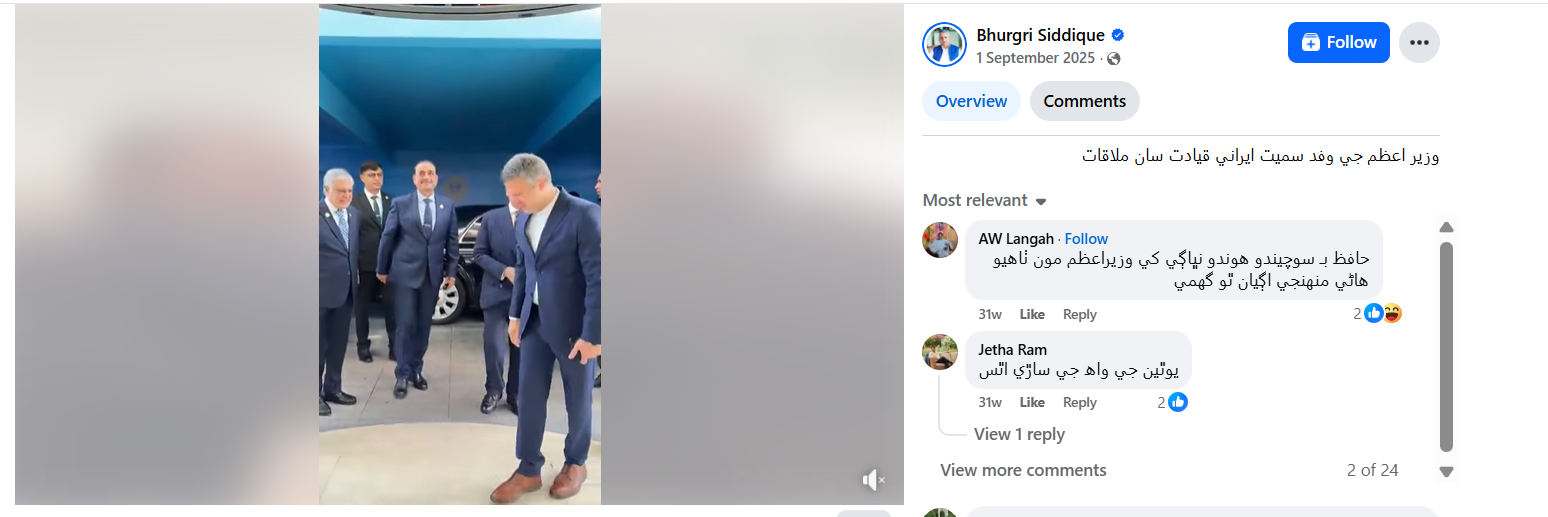
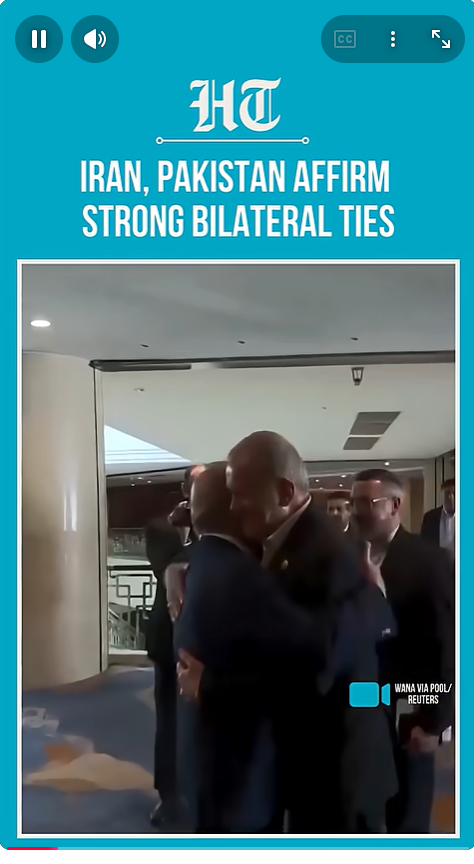
According to the available information, the video shows a meeting between a Pakistani delegation and Iranian leaders. Further keyword searches helped us locate a longer version of the same video on the official YouTube channel “HT Videos,” also uploaded on September 1, 2025. The video was from the Shanghai Cooperation Organisation Summit 2025 held in China, where leaders from various member countries, including Pakistan and Iran, had met.
Conclusion
The viral claim is misleading. The video does not show any recent meeting or welcome ceremony in Iran linked to the ongoing ceasefire talks. Instead, it is an old clip from September 2025, recorded during the SCO Summit in China. There is no evidence to suggest that the footage is related to current developments between the United States, Iran, and Pakistan. The video has been taken out of context and is being reshared with a false narrative to mislead users.
