
Law in 30 Seconds? The Rise of Influencer Hype and Legal Misinformation
Introduction
In today's digital age, we consume a lot of information and content on social media apps, and it has become a daily part of our lives. Additionally, the algorithm of these apps is such that once you like a particular category of content or show interest in it, the algorithm starts showing you a lot of similar content. With this, the hype around becoming a content creator has also increased, and people have started making short reel videos and sharing a lot of information. There are influencers in every field, whether it's lifestyle, fitness, education, entertainment, vlogging, and now even legal advice.
The online content, reels, and viral videos by social media influencers giving legal advice can have far-reaching consequences. ‘LAW’ is a vast subject where even a single punctuation mark holds significant meaning. If it is misinterpreted or only partially explained in social media reels and short videos, it can lead to serious consequences. Laws apply based on the facts and circumstances of each case, and they can differ depending on the nature of the case or offence. This trend of ‘swipe for legal advice’ or ‘law in 30 seconds’, along with the rise of the increasing number of legal influencers, poses a serious problem in the online information landscape. It raises questions about the credibility and accuracy of such legal advice, as misinformation can mislead the masses, fuel legal confusion, and create risks.
Bar Council of India’s stance against legal misinformation on social media platforms
The Bar Council of India (BCI) on Monday (March 17, 2025) expressed concern over the rise of self-styled legal influencers on social media, stating that many without proper credentials spread misinformation on critical legal issues. Additionally, “Incorrect or misleading interpretations of landmark judgments like the Citizenship Amendment Act (CAA), the Right to Privacy ruling in Justice K.S. Puttaswamy (Retd.) v. Union of India, and GST regulations have resulted in widespread confusion, misguided legal decisions, and undue judicial burden,” the body said. The BCI also ordered the mandatory cessation of misleading and unauthorised legal advice dissemination by non-enrolled individuals and called for the establishment of stringent vetting mechanisms for legal content on digital platforms. The BCI emphasised the need for swift removal of misleading legal information.
Conclusion
Legal misinformation on social media is a growing issue that not only disrupts public perception but also influences real-life decisions. The internet is turning complex legal discourse into a chaotic game of whispers, with influencers sometimes misquoting laws and self-proclaimed "legal experts" offering advice that wouldn't survive in a courtroom. The solution is not censorship, but counterbalance. Verified legal voices need to step up, fact-checking must be relentless, and digital literacy must evolve to keep up with the fast-moving world of misinformation. Otherwise, "legal truth" could be determined by whoever has the best engagement rate, rather than by legislation or precedent.
References:

Related Blogs
Executive Summary
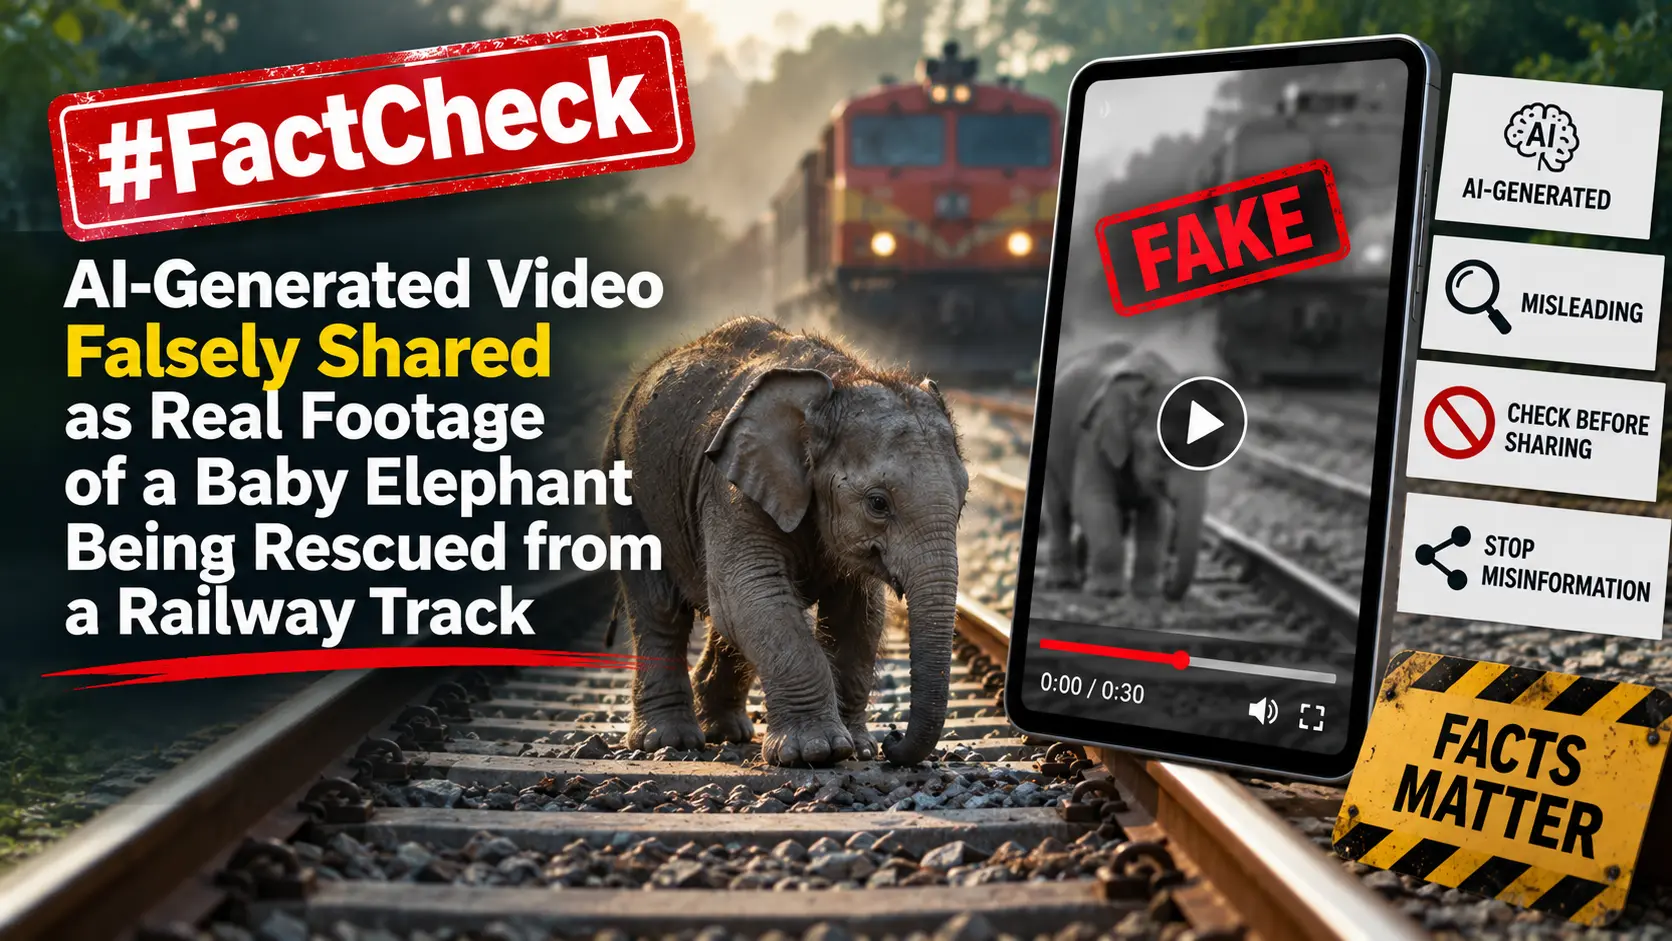
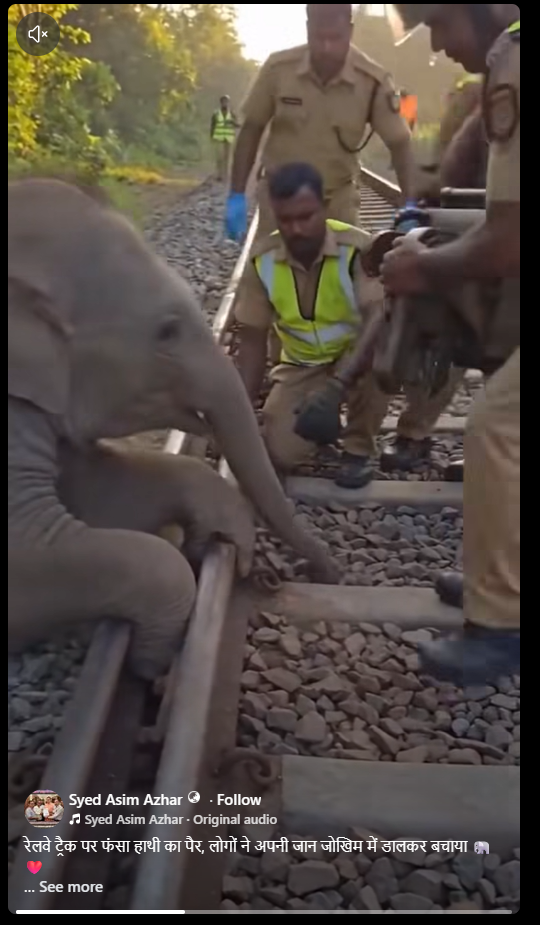
A video is being shared on social media showing a baby elephant apparently trapped in a railway track. In the video, its leg can be seen stuck between the tracks, while a train appears to be approaching. The video further shows rescuers using a hydraulic machine to remove part of the railway track and safely free the baby elephant. CyberPeace Research found that the viral claim is false. Our research found that the video is AI-generated and is being shared on social media with a false and misleading claim.
Claim:
A user on Facebook shared the video claiming that an elephant’s leg got stuck in a railway track, following which people risked their lives to safely rescue the animal. The post link, archive link and screenshot are provided below.
https://www.facebook.com/reel/992948767150505
Fact Check
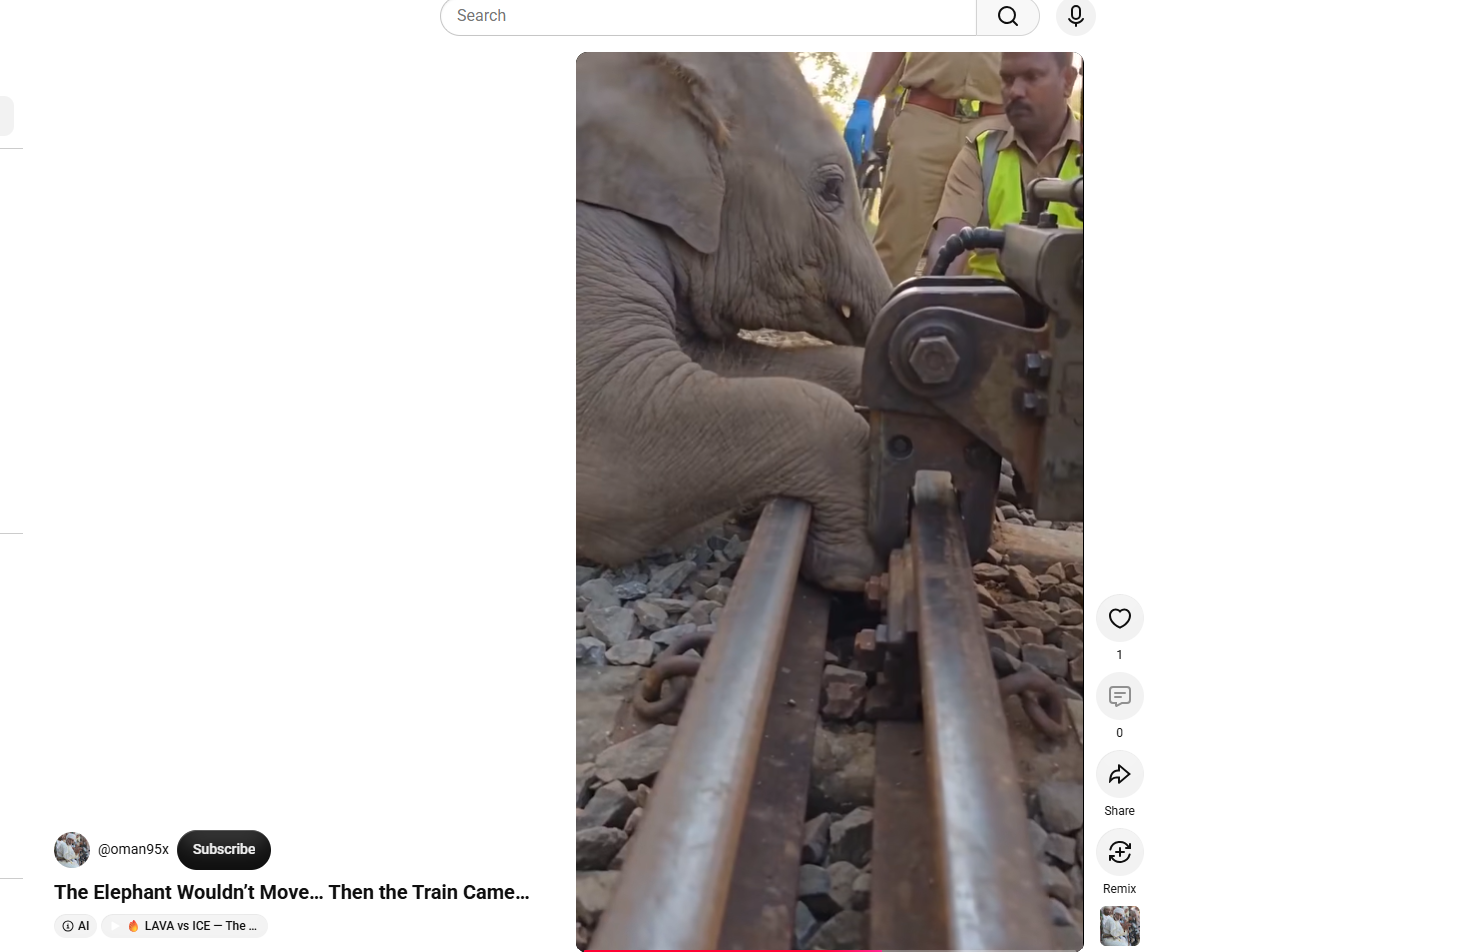
During our research, we conducted a reverse image search of different keyframes from the viral video. However, we did not find any credible media report or other authentic source related to the incident. However, during our research, we found some social media posts featuring the same video. These posts have labelled the video as AI-generated content.
https://www.youtube.com/shorts/TCQ2n6LDr_Q
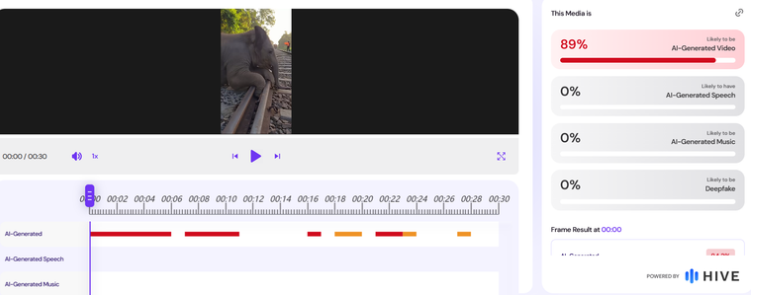
We then scanned the viral video using the Hive Detect tool. According to the tool’s analysis, the video was identified as potentially AI-generated with an 89% score.
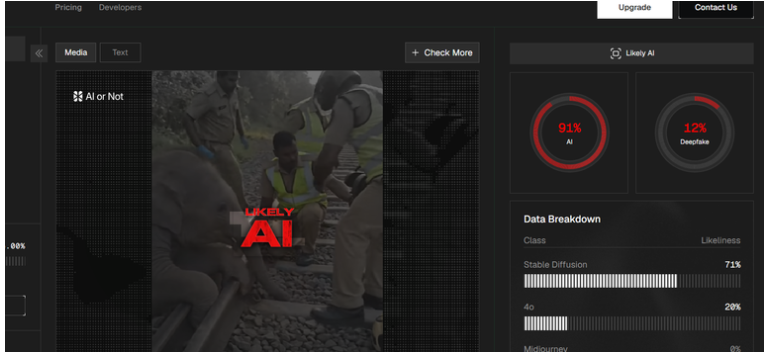
At the end of our research, we also examined the video using the AIorNot tool. According to its analysis, the visuals in the video were identified as AI-generated with a 91% probability.
Conclusion
Our research found that the video being shared on social media does not depict a real incident. During our research into the source and context of the video, we found no credible information supporting the claim. Furthermore, an analysis of the video using AI detection tools also confirmed that it is AI-generated.
Introduction
Did you know that millions of workers today earn their livelihood through digital platforms such as Uber, Lyft, Deliveroo, Amazon Flex, Swiggy, and Zomato? The gig economy refers to a labour market in which individuals earn income through short term, temporary, task based, or freelance work arrangements rather than traditional long term employment. Most gig work is facilitated through digital platforms such as Uber, Lyft, Deliveroo, Amazon Flex, Swiggy, and Upwork, which connect workers directly with customers seeking specific services. While the gig economy has created unprecedented opportunities for flexible work, it has also exposed workers to challenges such as insecure employment, lack of social security, unfair pay, and algorithmic control. To address these concerns, the International Labour Organization adopted Convention No. 193, the world's first binding international treaty dedicated to platform workers. The Convention marks a significant step towards ensuring decent work in the digital age and is expected to guide nations in building stronger legal and social protection frameworks for the rapidly expanding gig economy.
First Gig Economy Treaty at Glance
On June 12, 2026, the course of global labor governance took a decisive turn when, at its 114th International Labour Conference in Geneva, the ILO finally ratified the Decent Work in the Platform Economy Convention (ILO Convention No. 193) with a vote of 406-8-36. This first-ever binding instrument setting labor standards for digital platform/gig workers represents the product of a lengthy multi-year debate leading to an international understanding that labor law itself had to be redefined to apply to the digital age. The Convention sought to fill a regulatory gap in which "corporation power, algorithmic governance, work informality, and workers’ rightlessness defined the space."
The Genesis: How the Convention Came to Be
The negotiations of ILO Convention No. 193 were long, complex, and controversial. The systematic ILO attention on the gig economy was started during the beginning of the 2010s as on-demand app-based models provided by Uber, Lyft, Deliveroo, Amazon Flex, etc., began to transform the labor market fundamentally. The problem concerned is mass misclassification of workers.
Labeling platform workers as "independent contractors," as opposed to "employees," allows digital platforms to escape many standard labor law obligations such as minimum wage standards, social security benefits, health and safety standards, and the right to organize and bargain collectively.
Calls for international action escalated with the growth of the gig economy. 435 million people in the world were active in online gig work as of 2023, based on the World Bank Report. The platform work was added to the agenda of the ILO Governing Body in 2023. In 2024, a questionnaire was sent to member States and social partners and compiled into Report V(2): Realizing decent work in the platform economy (February 2025).
A decisive turning point occurred at the 113th International Labour Conference in June 2025 when, despite objections from employer representatives and governments like the United States, India, and Switzerland, delegates agreed to adopt both a binding Convention and a Recommendation on the issue.
A Standard-Setting Committee then produced a draft instrument throughout 2025 and early 2026. The committee's text was adopted by the committee on June 11, 2026, and by the conference plenary the following day. Civil society groups, including Privacy International and Human Rights Watch, played a role in the process through their recommendations regarding algorithmic governance, data privacy, and inclusive coverage.
Scope and Definitional Framework
The most important and contentious aspect of the Convention is its scope. The text defines "digital labour platforms" as being covered, as well as "all digital platform workers… whether in the formal or informal economy. "It is designed this way precisely because previous attempts at regulating platforms, such as the 2024 EU Platform Work Directive, which was weakened considerably by the Council's final approval, were narrow and open to carve-outs. "Digital platform worker," according to Convention No. 193, is defined as "a person who is in employment or engaged in work for the provision of a service organised and/or mediated by a digital labour platform." It makes no distinction regarding employee status, thereby evading the definitional trap that allowed platforms to deny responsibility by defining workers as self-employed. The platforms covered in the Convention include location-based (food delivery, ride-hailing, domestic care, and construction services) and online/cloud-based platforms (data annotation, content moderation, creative freelancing, and software development).
Key Substantive Provisions
- Fundamental Principles and Rights at Work :Convention 193 requires each state that ratifies it to make arrangements to "respect, promote, and realise" these fundamental principles and rights at work, which under the 1998 ILO Declaration were identified as freedom of association and the effective recognition of the right to collective bargaining; the elimination of forced or compulsory labour; the abolition of child labour and the elimination of discrimination in employment and occupation. The question of collective bargaining rights is especially important since digital platforms have not in the past been willing to accept unions and bargaining processes, claiming that since those who work on the platform are classified as independent contractors, they do not have the right to bargain collectively.
- Fair Pay and Parity of Treatment :The Convention enshrines equal pay and treatment for gig workers: "not less favorable conditions than those offered to workers of the same employment status classification." This has the aim of remedying the two-tier system maintained by a number of digital platforms, where workers performing the equivalent job role of employees are provided with considerably lower remuneration, lacking the benefits, stability, and protection afforded to employees under statutory labor law.
- Transparency and Algorithmic Accountability:One of the most innovative features of Convention 193 is its attempt to tackle algorithmic management. Digital platforms must supply information about the terms of the working relationship in a manner that is "timely, verifiable, and easily accessible and comprehensible" and, "in all cases prior to any significant changes," must disclose how automated systems allocate work, set pay, and determine termination decisions. Civil society organisations, such as Privacy International and Human Rights Watch, sought to make algorithmic control, including human oversight over automated decisions to impose disciplinary sanctions, legally binding. While the final provision fell short of doing so, it represents a new standard for algorithmic transparency in international labour law.
- Occupational Safety and Health :Each member state will be required to take steps to prevent occupational accidents, diseases, and injuries "affecting platform workers." For location-based gig workers, such as delivery and ride-hailing drivers who are repeatedly placed in hazardous and unstable work environments, this provision is vital in addressing what is frequently referred to as a 'silent crisis' within the platform economy, as workers are often ineligible for statutory workplace injury coverage and compensation schemes.
- Social Security Access:Possibly the most significant structural reform the Convention seeks to bring about, gig workers will have a right to access social security (including medical coverage, sick pay, and retirement and maternity/parental/sick benefits), which they have been able to bypass on the grounds of independent contractor status. For decades, digital platforms have lowered labor costs by externalizing the costs of social insurance onto gig workers themselves or public welfare systems. Convention 193 attempts to render that strategy illegal under international law.
- Protection for migrant and refugee workers :There are provisions protecting migrant and refugee platform workers and ensuring rights and protection throughout the life cycle of work, covering recruitment to employment and providing protection against discrimination. Migrant workers are over-represented among those employed in low-paid and informal gig work, where they face the highest risks of exploitation and deteriorating work conditions.
- Dispute resolution: Convention 193 establishes for platform workers the right to effective and impartial complaint and dispute resolution procedures as well as appropriate remedies, meaning when a country ratifies and domesticates the convention, workers will be empowered to pursue direct claims against digital platforms, overcoming the traditional obstacles placed in the way of such action.
Enforcement Architecture and Its Limitations
Despite the convention's potential, it is subject to key difficulties in implementation. The ILO does not have the enforcement power of the World Trade Organization, and simply ratifying a Convention does not automatically give domestic law effects. Countries must integrate the Convention into their national legislation, and ratifying members are not bound to implement it until 12 months after the Convention is ratified, which has also required two ratifications for entry into force. The Convention has optional provisions excluding the scope, where the argument is for the need of flexibility in the varied labour markets. While the International Trade Union Confederation, in reaction to the exclusions, has argued that large numbers of workers could be out of its protection, the countries that resort to the exceptions have to give a justification for this practice. The enforcement of the Convention is largely a matter of political will. Countries that, like the United States, voted against the Convention, will certainly choose not to ratify and implement it in their own legal system, leaving the gig workers out of its scope.
Geopolitical and Comparative Context
Convention No. 193 did not arise in a vacuum. There has been a trend of national governments regulating platform work in various ways. Spain's Riders' Law (2021) provided for a legal presumption of employment for delivery riders, while the UK Supreme Court ruled that Uber drivers are workers in 2021, entitling them to minimum wage and holidays. The French Constitutional Council (2020) found platform worker charter clauses consistent with rights. Some Indian states have promoted registration for gig workers for social security purposes (though national legislation is still needed). Convention No. 193 standardises these varied efforts through international normative agreement and particularly helps lower-income states lacking capacity or power against global platforms.
Conclusion
While ILO Convention No. 193 represents a momentous milestone for platform workers, the true impact of the Convention rests on ratification, domestic legislation, and judicial enforcement, alongside consistent vigilance on the part of the trade unions and civil society. Its most significant accomplishment to date is the establishment of a new international norm: for the first time, it establishes under international law that the labor rights of platform and gig workers are state responsibilities, not discretionary private undertakings by companies, a fact made urgently necessary by the growing strength of platform power.
References
- https://www.ilo.org/resource/conference-paper/ilc/113/draft-resolution-and-proposed-conclusions-standard-setting-committee-decent
- https://www.aljazeera.com/news/2026/6/12/un-adopts-treaty-setting-standards-for-gig-economy-workers
- https://www.ilo.org/node/697106
- https://www.europeanpapers.eu/e-journal/decent-work-gig-economy-appraisal-eu-ilo-regulation-digital-labour-platforms
- https://economictimes.indiatimes.com/news/international/world-news/worlds-fi
- https://www.taipeitimes.com/News/world/archives/2026/06/14/2003859085
Introduction
Picture a pickup truck moving at around 30 kilometres an hour down a straight country road outside Canberra. A journalist is driving it. Somewhere nearby, a researcher sits with a laptop, and without touching the vehicle, he switches the headlights off while it is still moving, in the dark, turns them back on, activates the wipers at full speed, sprays the windscreen washer, and plays sound through the cabin speakers. That scene, broadcast in September 2026 as part of an ABC Four Corners investigation into connected car security, is the starting point for a conversation that extends well beyond the one vehicle involved. (It was a commissioned cybersecurity demonstration, authorised and arranged by ABC's Four Corners as part of their journalistic investigation titled "Asleep at the Wheel.").
What the test actually found
The vehicle at the centre of the investigation was a BYD Shark 6, a plug-in hybrid pickup, which ABC's Four Corners programme provided to automotive cybersecurity researcher Dan Hreszczuk, co-founder of Canberra based Fortify Labs, for a two week authorised assessment. Hreszczuk later described the access point he found in notably simple terms: it did not require a password at all.
Over the course of the test, Hreszczuk demonstrated remote interaction with the vehicle's headlights, windscreen wipers, door locks, cabin speakers and infotainment display. He also tracked the vehicle's real time location and accessed its cabin microphone, which raised concerns beyond vehicle control and into personal surveillance, since a compromised in car microphone can expose private conversations rather than just dashboard functions. It is worth being precise about what the test did not reach. Hreszczuk said he could not access the brakes or the vehicle's cameras, describing those systems as well protected, and the demonstration did not amount to complete remote control of the vehicle.
Following the broadcast, BYD ran its own internal investigation and confirmed a software defect in the Shark 6's infotainment system. The company's engineers reproduced the access path and traced it to Android Debug Bridge, a standard Android development tool that is meant to be disabled in production vehicles but had been left reachable through the defect, alongside a separate route through the vehicle's CAN bus network. BYD has said it will issue an over the air software update to close the gap. Fortify Labs, for its part, stated its objective had been to simulate the kind of remote access a vehicle manufacturer itself typically holds over a connected car, and to demonstrate how that same level of access could be misused if it fell into the wrong hands.
This context matters because it distinguishes a controlled, authorised research exercise, conducted over two weeks with extended physical access to a single vehicle, from an active criminal compromise. No malware was involved, and no evidence has emerged of this technique being used against vehicles outside the test. The finding is nonetheless significant precisely because it shows what becomes possible once a single weak point in a vehicle's software stack is identified and deliberately explored.
The questions this raises, beyond one vehicle
The useful questions are structural ones. How is authentication actually enforced across every vehicle facing service, not just the ones a manufacturer assumes a researcher might look at? Are a vehicle's internal networks and external facing services properly segmented, so that compromising an infotainment system does not create an unobstructed path toward a vehicle's core control units? Are commands subject to strong authorisation and validation at every layer, rather than relying on obscurity or an assumption that a particular access route would be too obscure to find? Is the principle of least privilege consistently applied, so that a development tool left active in a production vehicle, as appears to have happened here, does not carry the same level of access a factory engineer would have? How are unusual remote behaviours actually detected and investigated in real time, rather than discovered after the fact through an external test? And how are vulnerabilities tracked and patched across a vehicle's entire operational lifecycle, given that a car, unlike a phone, is expected to remain in active use for well over a decade after it leaves the factory floor.
A rulebook already exists. The gap is enforcement, not ignorance
None of this had to be worked out from scratch after the Four Corners broadcast. The industry has had a binding answer to most of these questions sitting on the books since 2021, when the World Forum for Harmonization of Vehicle Regulations adopted UN Regulation No. 155, known in the industry simply as R155. It requires any manufacturer seeking vehicle type approval to run a certified Cybersecurity Management System covering the car's entire life, from the drawing board through production and all the way to the vehicle still being driven a decade later, and to pass a dedicated cybersecurity assessment before that vehicle type can legally go on sale. Since July 2024 the rule has applied not just to new vehicle designs but to every new vehicle rolling off the line, across more than sixty countries that are party to the underlying 1958 UNECE agreement, a list that includes the European Union, Japan, South Korea, and Australia itself.
That last detail is where the picture gets genuinely interesting, and where a simple story stops being quite so simple. Australia sits among the countries that have signed on to the UNECE framework R155 belongs to, yet coverage of the Four Corners investigation reported something that sounds contradictory at first glance: that Australia has no minimum cybersecurity standard actually governing cars sold in the country. Both things can be true at once. Being a party to the 1958 Agreement establishes that a country participates in the broader regulatory architecture; it does not automatically mean every regulation born out of that architecture has been separately adopted into domestic law and is being actively enforced at the point of sale. R155's own companion standard, ISO/SAE 21434, is the detailed engineering playbook manufacturers actually use to meet the regulation's requirements, walking through how to assess threats, design around them, and keep monitoring for new ones long after a vehicle has left the factory. A framework that comprehensive existing on paper is only as useful as a given market's willingness to actually require manufacturers to follow it before a car reaches a driveway, and that gap between a regulation existing globally and a regulation being enforced locally is arguably the more unsettling finding buried inside this story than the hack itself.
The broader lesson
The real takeaway from this test has very little to do with the particular badge on the vehicle involved. It is a demonstration of what happens when any one interface in a complex, connected system is left weaker than the rest of the architecture around it. As vehicles continue absorbing more software, more connectivity and more remote functionality, security boundaries cannot be treated as a feature added once at launch. They need to be designed deliberately, enforced consistently, and monitored continuously across the entire lifecycle of the vehicle and the ecosystem of backend services it depends on, because the cost of getting that wrong is no longer confined to a screen or a server. It now extends to the physical vehicle itself, and the people inside it.
References
- https://www.pakwheels.com/blog/byd-shark-6-hacked-during-cybersecurity-test-in-australia/
- https://securityaffairs.com/199460/hacking/a-byd-shark-6-hack-shows-the-risks-of-connected-cars.html
- https://autotalk.co.nz/byd-confirms-shark-6-software-defect-after-four-corners-hack-ota-fix-coming/
- https://www.carexpert.com.au/car-news/byds-own-shark-6-hacking-investigation-reveals-software-defect
- https://yourlifechoices.com.au/technology/the-connected-car-warning-behind-byds-shark-6-software-fix
- https://arnav.au/2026/09/22/byd-got-hacked-what-really-happened/
- https://pakobserver.net/byd-shark-6-hacked-in-security-test-as-researcher-gains-access-to-car-systems/
- https://www.femalefirst.co.uk/motoring/byd-issue-security-update-shark-6-after-hacking-concerns-1451532.html
- https://finitestate.io/blog/buckle-up-for-security-a-look-at-the-un-r155-regulation-for-connected-vehicles
- https://www.arteris.com/learn/un-r155-2/
