
Financial Risk Indicator Launched by DoT to Strengthen Cybersecurity
Introduction
On May 21st, 2025, the Department of Telecommunications (DoT) launched the Financial Risk Indicator (FRI) feature, marking an important step towards safeguarding mobile phone users from the risks of financial fraud. This was developed as a part of the Digital Intelligence Platform (DIP), which facilitates coordination between stakeholders to curb the misuse of telecom services for conducting cyber crimes.
What is the Financial Risk Indicator (FRI)?
The FRI is a risk-based metric feature that categorises phone numbers into risk, medium risk, and high risk based on their association with financial fraud in the past. The data pool enabling this intelligence sharing includes the Digital Intelligence Unit (DIU) of the DoT, which engages and sends a list of Mobile Numbers that were disconnected (Mobile Number Revocation List - MNRL) to the following stakeholders, creating a network of checks and balances. They are:
- Intelligence from Non-Banking Finance Companies, and UPI (Unified Payment Interface) gateways.
- The Chakshu facility- a feature on the Sanchar Saathi portal that enables users to report suspected fraudulent communication (Calls, SMS, WhatsApp messages), which has also been roped in.
- Complaints from the National Cybercrime Reporting Portal (NCRP) through the I4C (Indian Cyber Coordination Center).
Some other initiatives taken up concerning securing against digital financial fraud are the Citizen Financial Cyber Fraud Reporting and Management System, the International Incoming Spoofed Calls Prevention System, among others.
A United Stance
The ease of payment and increasing digitisation might have enabled the increasing usage of UPI platforms. However, post-adoption, the responsibility of securing the digital payments infrastructure becomes essential. As per a report by CNBC TV18, UPI fraud cases surged by 85% in FY24. The number of incidents have increased from 7.25 lakh in FY23 to 13.42 lakh in FY24. These cases involved a total value of ₹1,087 crore, compared to ₹573 crore in the previous year, and the number continues to increase.
Nevertheless, UPI platforms are taking their own initiative to combat such crimes. PhonePe, one of the most used digital payment interface as of January 2025 (Statista) has already incorporated the FRI into its PhonePe Protect feature; this blocks transactions with high-risk numbers and issues a warning prior to engaging with numbers that are categorised to be of medium risk.
CyberPeace Insights
The launch of a feature addressing the growing threat of financial fraud is crucial for creating a network of stakeholders to coordinate with law enforcement to better track and prevent crimes. Publicity of these measures will raise public awareness and keep end-users informed. A secure infrastructure for digital payments is necessary in this age, with a robust base mechanism that can adapt to both current and future threats.
References
- https://www.thehawk.in/news/economy-and-business/centre-launches-financial-fraud-risk-indicator-to-safeguard-mobile-users
- https://telanganatoday.com/government-launches-financial-fraud-risk-indicator-to-safeguard-mobile-users
- https://www.pib.gov.in/PressReleasePage.aspx?PRID=2130249#:~:text=What%20is%20the%20%E2%80%9CFinancial%20Fraud,High%20risk%20of%20financial%20fraud
- https://www.business-standard.com/industry/news/dot-launches-financial-fraud-risk-indicator-to-aid-cybercrime-detection-125052101912_1.html
- https://www.cnbctv18.com/business/finance/upi-fraud-cases-rise-85-pc-in-fy24-increase-parliament-reply-data-19514295.htm
- https://www.statista.com/statistics/1034443/india-upi-usage-by-platform/#:~:text=In%20January%202025%2C%20PhonePe%20held%20the%20highest,key%20drivers%20of%20UPI%20adoption%20in%20India
- https://telecom.economictimes.indiatimes.com/amp/news/policy/centre-notifies-draft-rules-for-delicensing-lower-6-ghz-band/121260887?nt

Related Blogs
Introduction
It might seem too good to be true: free movies, live TV and sports without any subscription plan are deals that no one in India could actually refuse, and that’s precisely the explanation as to why applications such as Pikashow have gained tremendous traction in India and all over the world as well. However, cybersecurity authorities have a strong cause of concern: the threat that this type of application poses towards lakhs of Indians with malicious software, stealing information and even money. Pikashow may be a perfect case study to establish this problem, but in fact, it all ties down to how downloading anything without the recognised applications has certain risks attached to it.
The Pikashow Warning
With no monthly subscription fees, Pikashow is a popular free app for streaming movies, web series, live TV channels and sports programmes. Since its development, Pikashow has had a reputation for never being found on the Google Play Store or Apple’s App Store, which necessitates a process of side-loading. A side load, in this case, entails downloading the Pikashow APK file from an unofficial third-party source and manually installing the app, circumventing the security measures of official download channels.
The latter is significant because security experts who have analysed Pikashow argue that it acts as an informal content aggregator; movies and TV series are illegally scooped up from online streaming services, then shared via various third-party links and streamed without a content licence or any agreement with legitimate providers.
Without going through the rigorous checks conducted by Google or Apple, security researchers discovered that even while the app appeared to be working fine with its promised streams, hidden malware within the installer can run silently, leading to potentially significant security risks such as data theft of user logins, one-time passwords, and private files, including banking credentials. This has been cited to be so problematic for India that law enforcement agencies like the Indian Cyber Crime Coordination Centre under the Ministry of Home Affairs and the Cyber Dost platform are expected to have issued public advisories linking Pikashow to a proliferation of cases of cybercrime. Users should take into account the legal implications alongside security concerns, as using piracy apps may not only lead to device-compromising issues but can also be against the Copyright Act of India as well, thus increasing the risk of legal prosecution.
Why This Isn't Just a "Pikashow Problem"
This should not be viewed as a single warning concerning one app. Pikashow is merely an illustration of one app from millions that exists outside official app stores and is built with the same mechanics that make Pikashow dangerous and applicable to virtually any app, game, or "modded" file which is downloaded from a random website, third-party app store, or Telegram channel.
Some issues that persist are-
- Official app stores are like a filter that is not perfect, but it is still critical to the security on a user's device. Both Google and Apple's App stores run automatic and manual malware scanners, screen permissions for legitimate use, and have the ability to remove malicious developers as necessary. Empirical research has estimated just how important this is: more than fifty-times more malware exists on sideloaded, "unofficial" apps versus official. Mobile security firm Zimperium claims nearly 40% of all devices tested with malware were infected due to downloading an app from outside the official app stores; furthermore, nearly 80% of malicious, sideloaded apps contained riskware or trojans.
- Informational channels can also be used to gain the trust of users by mimicking familiar brands One frequently mentioned scheme is one where malicious actors repackage popular apps with a malignant intent to syphon the app, disguised as a free, trustworthy app. Often when these apps are available, they work exactly the same as the legitimate app, as a matter of fact, but quietly in the background steal passwords or log keystrokes; this was discovered to be occurring with a financial trojan called TeaBot, where bank details and login info were intercepted through the device's Accessibility Service.
- There is generally no recourse or legal liability that applies once something has gone wrong. While official app stores are official developers that can be identified to submit complaints against them, if a third-party download leads to damages, that developer generally cannot be located to establish liability or legal standing.
- Excessive app permissions will often go undetected This occurs for the similar reasons that a malicious actor can include such a clause as explained above. There's really nothing to stop the developer from asking to utilise one's SMS, call log, camera, microphone, storage or location when there's not one reason for one application to need access to everything on the device.
- Expired software has the same or more risk It's actually very common to see apps that receive security updates out in the wild that either don't have the appropriate update sent over to third-party app stores or third-party stores don't have the capacity to update the affected applications. That's why most official third-party app downloads should be of fairly new versions; for example, outdated versions of a banking app, which is being patched as well as receiving other updates from Google or Apple still, will continue to persist on third-party download sites for some time after patching, which could then be malicious.
- Even legitimate, globally recognised apps can and have been compromised The same vulnerability was noted for TikTok in 2023, which, when found on unofficial APK download sites, contained hidden data-tracking malware yet looked identical to the official app version.
How to Protect Yourself
The reassuring thing is that the vast majority of this risk can be eliminated through simple, repeatable habits. Use trusted sources like Google Play and Apple's App Store, which are not faultless, of course, but they remove many infected apps from circulation following review.
- Be sceptical of "free" premium-paid apps.
- If something in a file from a site you don't recognise offers content or features that are normally behind a paywall and they want nothing to do with it, that is a bad sign, not a good deal. Review app permissions when you go to install anything. A flashlight doesn't need access to your SMS messages or contacts, as one recently downloaded on a colleague's Android allegedly attempted to acquire them from the Google Play store. After sideloading any app that you do not fully trust, it's always a wise idea to uninstall it and scan the handset to ensure malicious files aren't still lingering around.
- Choose legitimate services to avoid malware.
- In entertainment terms this will apply most clearly to piracy but applies similarly elsewhere in many senses. Trusted sources that are licensed include YouTube, JioCinema, Hotstar, Netflix, Amazon Prime Video, and MX Player, among others, which will offer content similar to illegally acquired or pirated versions without the security, as well as the legal risks. If you have recently used the file installation route to any degree of caution on a sensitive device, then also monitor banking and payment apps.
- That is not least because the most reported consequence of infection from an illicit or unknown source is the theft of financial account login details.
Conclusion
Free entertainment can look tempting, but as cybersecurity experts keep pointing out, "free" often just means the cost has been shifted from your wallet to your data, your device, and potentially your bank account. The safest rule of thumb remains simple: if an app isn't on an official store, ask why and think twice before installing it.
Sources
- Pikashow app risky, may expose users to malware and data theft: Experts — Times of India
- Free OTT Hack or Cyber Trap? Pikashow Flagged for Serious Security Risks — The420.in
- Pikashow Warning: Free Movies Could Empty Your Bank Account, Government Issues Strong Alert — The420.in
- Is Pikashow Safe or Risky to Use in 2025? Expert's Advice — AiPlex AntiPiracy
- Why Pikashow May Not Be Safe for Your Device — AiPlex AntiPiracy
- Concerns Rise Over the Safety of Popular Streaming App Pikashow — openPR
- Beyond the App Store: The Hidden Risks of Sideloading Apps — Zimperium
- App Sideloading: Risks, Rules, and How IT Admins Respond — Trio
- What Are the Risks of Sideloading Apps on Your Smartphone? — Bitdefender
- Sideloading Risk: Alternative App Stores and Brand Protection — Allure Security
- Building a Trusted Ecosystem for Millions of Apps: A Threat Analysis of Sideloading — Apple
For years, Malaysia governed artificial intelligence the way most countries did before they had to, with guidelines nobody could be fined for ignoring. The National Guidelines on AI Governance and Ethics, published by Malaysia's Ministry of Science, Technology and Innovation back in September 2024, told developers and deployers what "responsible AI" should look like. It just never made anyone legally responsible for anything.
Malaysia is now attempting to change that. On 10 July 2026, the National AI Office (NAIO), operating under the Ministry of Digital, released a Public Consultation Paper for what would become Malaysia's first horizontal AI statute: a single law covering AI across every sector, rather than a patchwork of guidelines, data protection rules, and whatever a particular regulator happens to think about algorithms this year. Written submissions closed on 31 July 2026, and the government has said it wants the Bill tabled and completed before the year is out. That is an aggressive timeline for a law this broad, and it tells you something about how urgently Putrajaya wants this on the books.
Why "horizontal" matters here
Most of the world's AI rules so far have been vertical. A banking regulator handles AI in banking, a health authority handles AI in diagnostics, and everything in between is grey space. Malaysia's own consultation paper is refreshingly candid about the problem this creates: it warns of "differing standards and approaches" building up across sectors, and notes that existing tools only really respond after something has already gone wrong.
The Bill tries to fix that by sitting above the sector specific rules rather than replacing them. It rests on three pillars.
- First, a Central AI Authority, which would still lean on existing regulators (think Bank Negara Malaysia for financial services or the Securities Commission for capital markets) through what the paper calls "Sectoral Leads."
- Second, a set of baseline principles written into law rather than left as suggestions: human dignity, transparency and explainability, accountability, safety and security, and data governance.
- Third, a structure that scales obligations to how dangerous a given AI system actually is, instead of regulating a spam filter and a hospital triage algorithm with the same rulebook.
The mechanics: three tiers, two roles, one authority
The risk framework itself splits into three tiers: Tier 1 for unacceptable risk, Tier 2 for high risk, and Tier 3 for low risk, with obligations scaling up as the potential for harm does. Obligations fall on two kinds of actors: Developers, who materially shape what a system can do, and Deployers, who actually run it in the real world. A single company can be both. This split deliberately echoes the controller and processor distinction from Malaysia's Personal Data Protection Act, though not perfectly, a point several legal commentators have already flagged as a source of future confusion, since a Deployer processing personal data will usually be a controller under the PDPA, while a Developer offering a hosted model might only be a processor.
The Central AI Authority itself is proposed to run three functions: an AI Safety function that maintains the risk framework and oversees testing and incident reporting; an Investigation and Enforcement function with power to demand fact finding and issue directions after incidents; and an AI Enablement function that produces guidance, templates, training, and runs the AI Sandbox, a controlled testing environment meant to let companies experiment before the full weight of compliance lands on them. For smaller businesses without in house compliance teams, that enablement mandate may end up mattering more day to day than the enforcement powers do.
Two more features round out the design. An incident reporting mechanism would require Developers and Deployers to flag not just failures but near misses and unexpected effects, with the public also able to lodge complaints directly. And the Bill's territorial reach is broad by design: it would apply to any AI system designed, developed, or used in Malaysia, regardless of where the underlying infrastructure sits, carving out exemptions only for personal use and national security matters.
How this stacks up against the EU AI Act
Malaysia's drafters have clearly been reading Brussels' homework, and it shows in the structure: a tiered risk model, a central authority, mandatory obligations tied to risk level. But the resemblance is more skeletal than skin deep once you look at the details.
The EU AI Act is a fully codified regulation running to hundreds of pages, with named prohibited practices spelled out in an annex, specific high risk categories listed by sector, and detailed conformity assessment procedures before a system ever reaches the market. Malaysia's Bill, at consultation stage, is still working from principles and a harm list rather than an exhaustive catalogue of prohibited or high risk use cases, closer in spirit to a framework law that leaves the granular detail to subsidiary guidelines and Sectoral Leads. That's partly a function of timeline: the EU spent roughly three years negotiating its Act before adoption, while Malaysia is trying to move from consultation paper to finished statute inside a single year.
Enforcement philosophy differs too. Brussels built the AI Act around compliance that happens before deployment: conformity assessments, technical documentation, and sign off procedures similar to product safety certification, particularly for high risk systems. Malaysia's design leans more on an enablement first posture, with sandboxes, guidance, and incident reporting sitting alongside enforcement powers rather than in front of them, at least as currently framed. Whether that survives contact with the final legislative text is an open question. The consultation drew real pushback from law firms wanting harsher penalty ranges and clearer thresholds, so the version tabled in Parliament may look tougher than the one made public in July.
There's also a jurisdictional difference worth flagging. The EU AI Act has genuine extraterritorial teeth backed by the largest single market in the developed world, which is why companies far outside Europe still comply with it. Malaysia's Bill claims similarly broad reach on paper, covering any system used in Malaysia regardless of where it's hosted, but the practical leverage to enforce that against a foreign Developer is a different question entirely, and one the Edwin Lee and Partners (Law firm based in malaysia) submission specifically raised as a gap needing an international cooperation mechanism.
India and AI Regulation
India has spent the past year deliberately walking in the evolving direction. Through MeitY's India AI Governance Guidelines, released in November 2025 ahead of the India AI Impact Summit, explicitly reject a standalone AI statute in favour of what officials have repeatedly called a "light touch" model: seven guiding principles, trust, people first, innovation, fairness, accountability, transparency, and safety, layered on top of existing law rather than a new one. The Digital Personal Data Protection Act, 2023 and the IT Act, 2000 with amendment rules, do most of the actual legal work, with sector regulators like the RBI and SEBI handling the specifics for their own industries.
The contrast with Malaysia is almost a case study in two governance philosophies. Where Malaysia is building a central authority with enforcement teeth from day one, India has so far preferred advisory bodies, an AI Governance Group and a proposed AI Safety Institute, that shape norms without imposing binding cross sectoral obligations.
Where Malaysia's Bill would be justiciable law with penalties attached, India's framework is closer to a philosophy statement with sandboxes and a national incident database bolted on. That is not a weaker approach so much as a different, and arguably shrewd, bet. India is the world's largest testing ground for AI adoption at scale, from welfare delivery to vernacular language tools, and a heavy compliance regime risks slowing exactly the kind of grassroots experimentation the government is trying to encourage. Betting on existing law and institutional judgment, at least for now, keeps that door open, and it has let India move fast without waiting for a perfect law first.
That said, India's position has been visibly shifting. In July 2026, MeitY Secretary S. Krishnan signalled the government is now exploring dedicated AI legislation after all, a notable departure from the "no early regulation" stance the ministry had held in 2023, and this is likely accelerated by growing concern over deepfakes and synthetic media, which already prompted binding traceability and labelling obligations under amended intermediary rules earlier this year.
The stakes for the next few months
None of this is finished. Malaysia's Bill is still a consultation paper, not enacted law, and the gap between what NAIO proposed in July and what Parliament eventually passes could be significant. Several submissions are already pushing for a wider harm list, sharper enforcement thresholds, and clearer rules for foreign Developers who never set foot in Kuala Lumpur. But the direction is set. Malaysia has decided AI governance can no longer run on goodwill and voluntary guidelines, and it now attempts to write enforceable AI law on a real deadline rather than settling for guidelines. However, the final Bill lives up to that ambition, or gets watered down in the process, is something only the next few months will show.
References
- Ministry of Digital. "Kementerian Digital Mulakan Libat Urus Cadangan Rang Undang Undang Tadbir Urus Kecerdasan Buatan (AI)." 10 July 2026. https://www.digital.gov.my/en-GB/siaran/Kementerian-Digital-Mulakan-Libat-Urus-Cadangan-Rang-Undang-Undang-Tadbir-Urus-Kecerdasan-Buatan-(AI)
- Digital Watch Observatory. "Malaysia launches consultations on AI Governance Bill." July 2026. https://dig.watch/updates/malaysia-ai-governance-bill-consultation
- Baker McKenzie, Wong and Partners. "Malaysia: Public Consultation on the AI Governance Bill." July 2026. https://www.bakermckenzie.com/en/insight/publications/2026/07/malaysia-public-consultation-on-the-ai-governance-bill
- Digital Policy Alert. "Testing requirements in AI Governance Bill" and related entries on the National AI Office consultation. https://digitalpolicyalert.org
- Rahmat Lim and Partners. "National AI Office issues public consultation paper on proposed Artificial Intelligence (AI) Governance Bill." https://www.rahmatlim.com/perspectives/articles/33264/mykh-national-ai-office-issues-public-consultation-paper-on-proposed-artificial-intelligence-ai-governance-bill
- Edwin Lee and Partners. "Malaysia's AI Governance Bill: Our Submission to the Consultation." https://lpplaw.my/ai-governance-malaysia/
- Kiizen. "Overview of the Proposed Malaysia's AI Governance Bill." https://www.kiizen.com.my/proposed-malaysias-ai-governance-bill/
- Zicelegal. "Consultation Alert: Public Consultation on Malaysia's AI Governance Bill." https://www.ziclegal.com/resources/consultation-alert-public-consultation-on-malaysias-ai-governance-bill
- Welcome.AI. "Malaysia's AI Governance Bill Expands Regulation and Accountability for Businesses." July 2026. https://www.welcome.ai/content/malaysias-ai-governance-bill-expands-regulation-and-accountability-for-businesses
- Regulations.ai. "Malaysia AI Regulation Overview." https://regulations.ai/regulations/RAI-MY-NA-SUMMARY-2026
- w.media. "Malaysia to enact AI law." https://w.media/malaysia-to-enact-ai-law/
- VisionIAS. "India's New AI Governance Guidelines Push Hands Off Approach." November 2025. https://visionias.in/blog/current-affairs/indias-new-ai-governance-guidelines-push-hands-off-approach
- EY India. "AI governance guidelines: A bet on innovation." https://www.ey.com/en_in/insights/ai/ai-governance-guidelines-a-bet-on-innovation
- TechnoSports. "Airegulation: Indian Government Finalizes AI Regulation." May 2026. https://technosports.co.in/airegulation-india-framework/
- The AI Track. "India AI Governance Guidelines Released for 2025 to 26." https://theaitrack.com/india-ai-governance-guidelines-2025/
- Lexology, contributed by a law firm. "India's AI Governance Model: MeitY's AI Guidelines and The Evolving Copyright Landscape." March 2026. https://www.lexology.com/library/detail.aspx?g=ffc0c58c-3727-4472-9914-5fa6a33ffffd
- Srishti IAS. "India's First AI Governance Framework 2026: Principles, Oversight, and Inclusive Growth Strategy." February 2026. https://srishtiias.com/india-first-ai-governance-framework-ahead-of-impact-summit-2026/
- Whalesbook. "India Plans Dedicated AI Law, Shifting From Light Touch Approach." July 2026. https://www.whalesbook.com/news/English/other/India-Plans-Dedicated-AI-Law-Shifting-From-Light-Touch-Approach/6a4811c9c7db2a6cf1650f24
- Saikrishna and Associates. "Decoding the India AI Governance Guidelines." November 2025. https://www.saikrishnaassociates.com/decoding-the-india-ai-governance-guidelines/
- News on Air. "MeitY Unveils India AI Governance Guidelines to Promote Safe and Responsible AI Adoption." 5 November 2025. https://www.newsonair.gov.in/meity-unveils-india-ai-governance-guidelines-to-promote-safe-and-responsible-ai-adoption
Contributors
- Maj. Vineet Kumar, Founder & Global President, CyberPeace
- Mr. Neeraj Soni, Senior Research Analyst, Policy & Advocacy, CyberPeace
Executive Summary
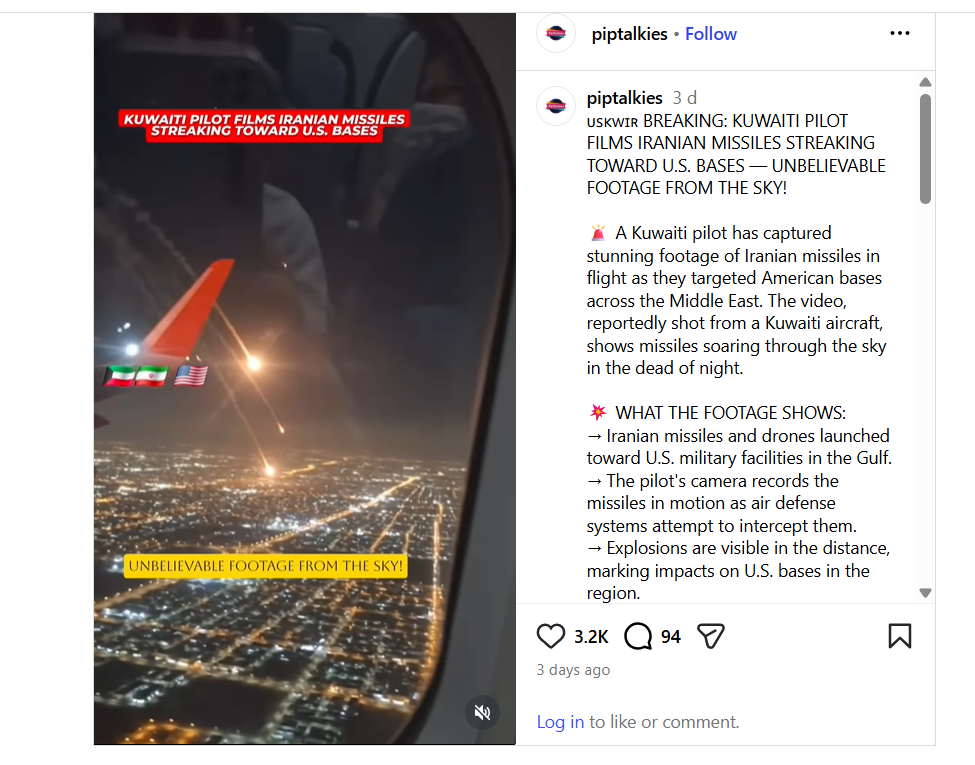
A video is being widely shared on social media showing what appears to be a missile attack over a densely populated city at night. The footage, seemingly recorded from inside a passenger aircraft, shows multiple explosions and missiles lighting up the sky.The video is being circulated with the claim that a Kuwaiti pilot filmed Iranian missiles being launched towards a US military base in the Middle East from the cockpit of an aircraft.
CyberPeace Research Wing’s research found the viral claim to be false. Our research confirmed that while Iran has launched attacks on US military installations in the Middle East, the viral footage is not related to those incidents. The video was found to be AI-generated and is being shared with a false and misleading narrative.
Claim
An Instagram user shared the viral video on July 11, 2026, claiming that it was recorded by a Kuwaiti pilot from an aircraft and shows Iranian missiles targeting a US military base in the Middle East.
Post Link: https://www.instagram.com/reel/DanymEDIdp2/?utm_source=ig_web_button_share_sheet
Fact Check
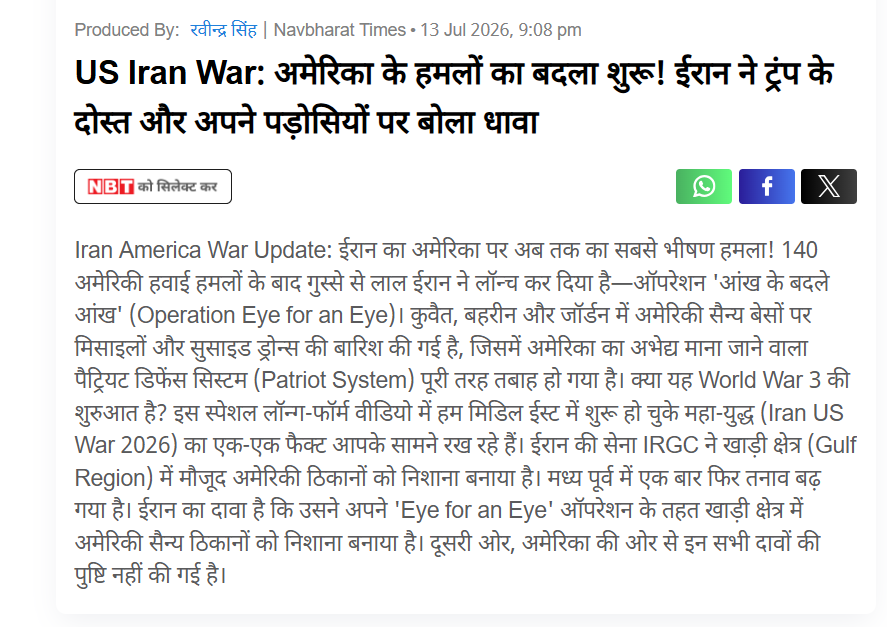
To verify the claim, we conducted a keyword-based search on Google. During the research, we did not find any credible news report or authentic source linking the viral video to the alleged Iranian missile attack. We did find a Navbharat Times report covering Iran's strikes on US military bases in the Middle East. However, the report did not contain the viral footage or any reference suggesting that such a video had been recorded by a Kuwaiti pilot. https://navbharattimes.indiatimes.com/video/news/america-iran-war-retaliation-for-us-attacks-begins-iran-strikes-at-trumps-allies-and-its-neighbour/videoshow/132370583.cms
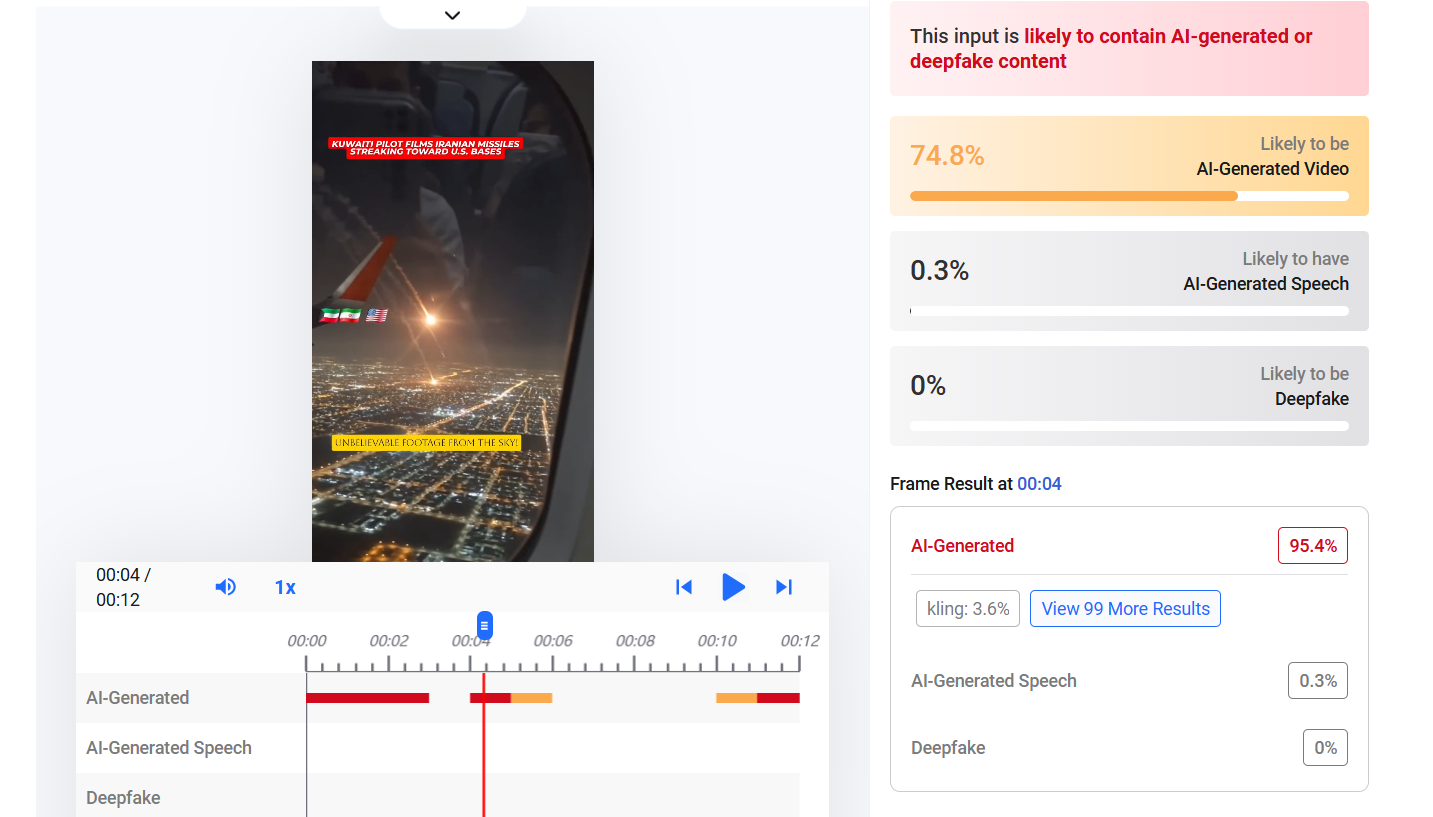
In the next stage of the research, we analysed the viral video using the AI detection tool Hive Moderation. The tool indicated that the video had a 74.8% probability of being AI-generated.
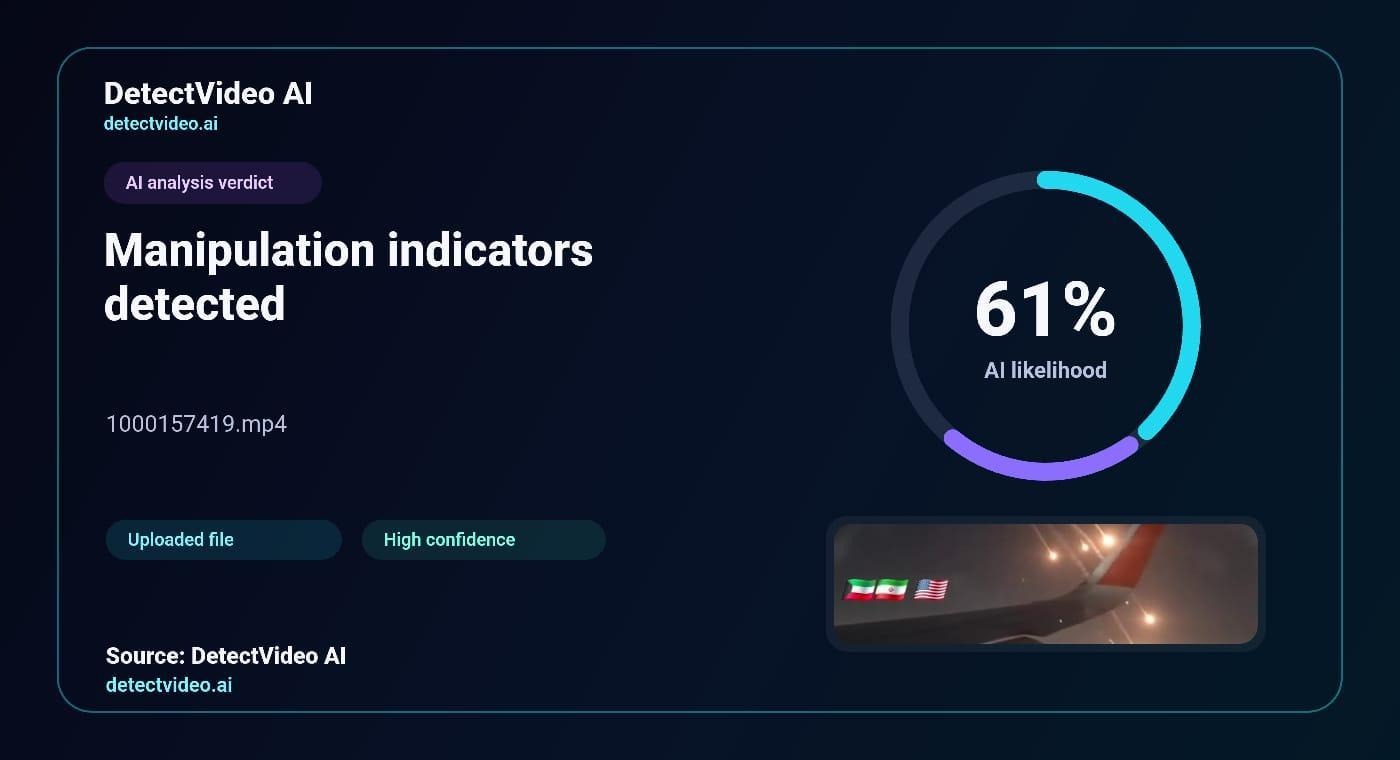
For additional verification, we also analysed the footage using another AI detection tool, DetectVideo AI. Its analysis showed a 61% probability that the video was AI-generated.
Conclusion
Our research found that the viral claim is false. Although Iran has carried out missile strikes on US military facilities in the Middle East, the viral video is not authentic and has no connection to those attacks. The footage was found to be AI-generated and is being circulated on social media with a misleading claim that it was recorded by a Kuwaiti pilot from an aircraft.
