
#FactCheck: An image shows Sunita Williams with Trump and Elon Musk post her space return.
Executive Summary:
Our research has determined that a widely circulated social media image purportedly showing astronaut Sunita Williams with U.S. President Donald Trump and entrepreneur Elon Musk following her return from space is AI-generated. There is no verifiable evidence to suggest that such a meeting took place or was officially announced. The image exhibits clear indicators of AI generation, including inconsistencies in facial features and unnatural detailing.
Claim:
It was claimed on social media that after returning to Earth from space, astronaut Sunita Williams met with U.S. President Donald Trump and Elon Musk, as shown in a circulated picture.

Fact Check:
Following a comprehensive analysis using Hive Moderation, the image has been verified as fake and AI-generated. Distinct signs of AI manipulation include unnatural skin texture, inconsistent lighting, and distorted facial features. Furthermore, no credible news sources or official reports substantiate or confirm such a meeting. The image is likely a digitally altered post designed to mislead viewers.

While reviewing the accounts that shared the image, we found that former Indian cricketer Manoj Tiwary had also posted the same image and a video of a space capsule returning, congratulating Sunita Williams on her homecoming. Notably, the image featured a Grok watermark in the bottom right corner, confirming that it was AI-generated.

Additionally, we discovered a post from Grok on X (formerly known as Twitter) featuring the watermark, stating that the image was likely AI-generated.
Conclusion:
As per our research on the viral image of Sunita Williams with Donald Trump and Elon Musk is AI-generated. Indicators such as unnatural facial features, lighting inconsistencies, and a Grok watermark suggest digital manipulation. No credible sources validate the meeting, and a post from Grok on X further supports this finding. This case underscores the need for careful verification before sharing online content to prevent the spread of misinformation.
- Claim: Sunita Williams met Donald Trump and Elon Musk after her space mission.
- Claimed On: Social Media
- Fact Check: False and Misleading

Related Blogs
Executive Summary
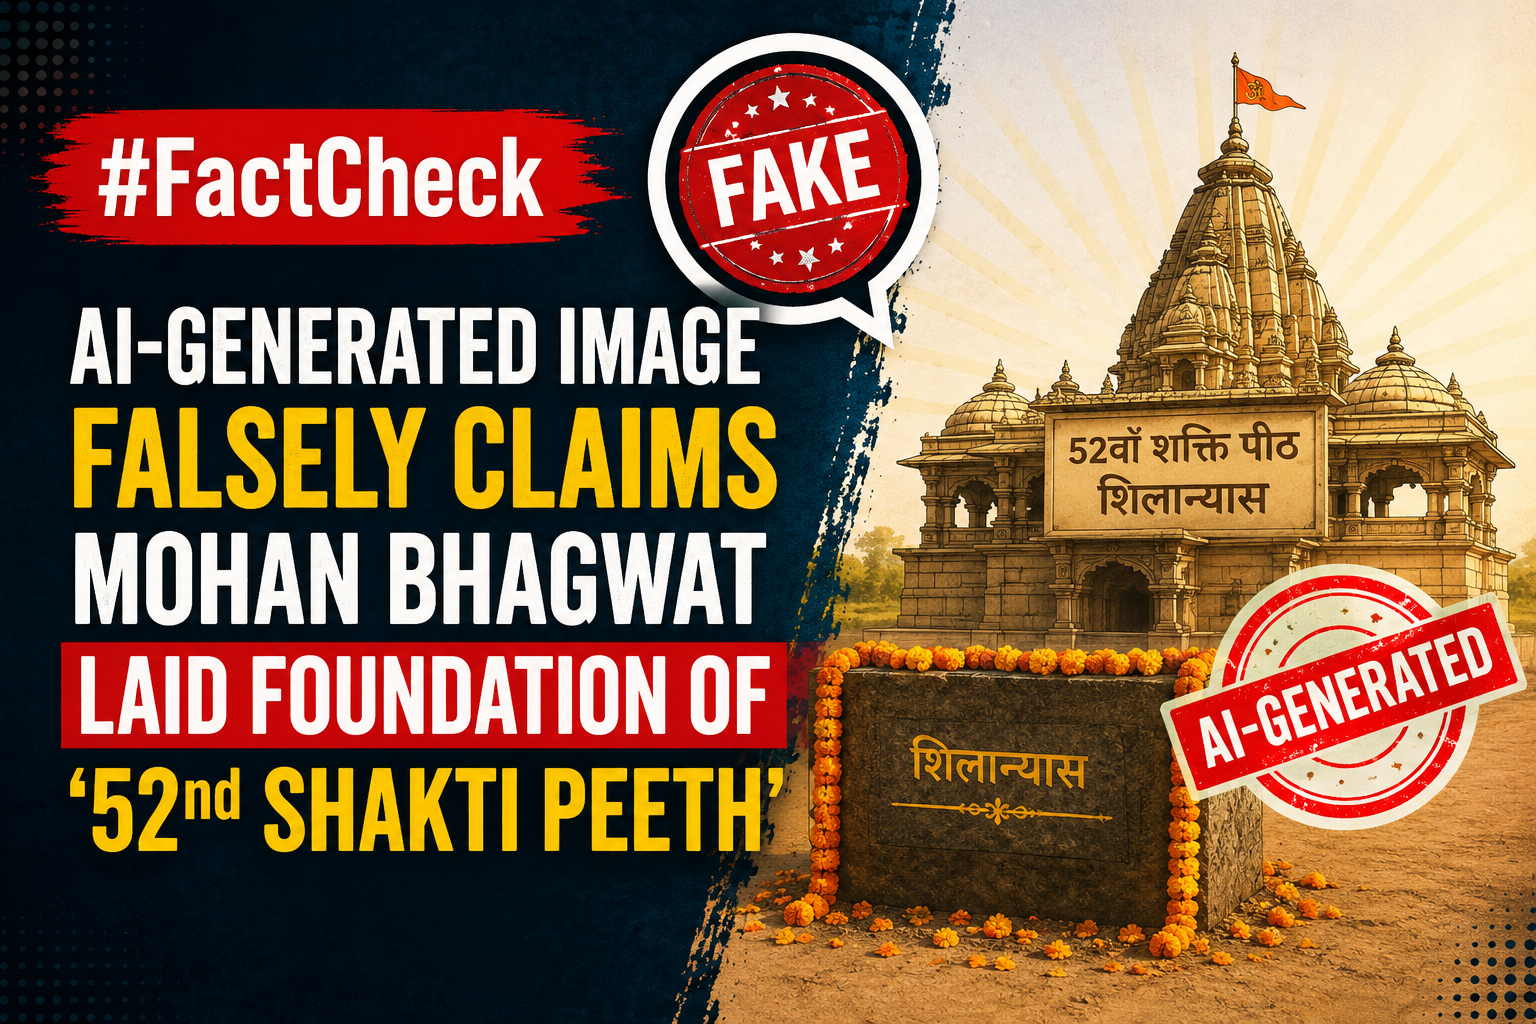
A picture of Mohan Bhagwat is going viral on social media, showing him allegedly laying the foundation stone of a so-called “52nd Shakti Peeth” named Bharatdurga. Users are claiming that the RSS chief insulted Sanatan Dharma by creating a new Shakti Peeth in Nagpur. Research by CyberPeace Research Wing found that the claim is false. The viral image is AI-generated, and Mohan Bhagwat did not inaugurate any “52nd Shakti Peeth.” In reality, he laid the foundation stone of the Bharatdurga Temple.
Claim
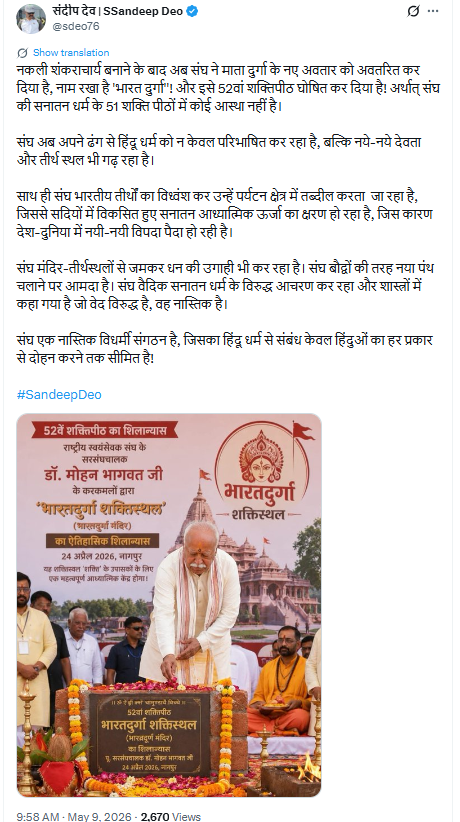
An X user named Sandeep Dev shared the viral image and alleged that after creating “fake Shankaracharyas,” the RSS had now introduced a new form of Goddess Durga called “Bharat Durga” and declared it the 52nd Shakti Peeth. The post further claimed that the RSS was redefining Hinduism and creating new religious sites.
Fact Check
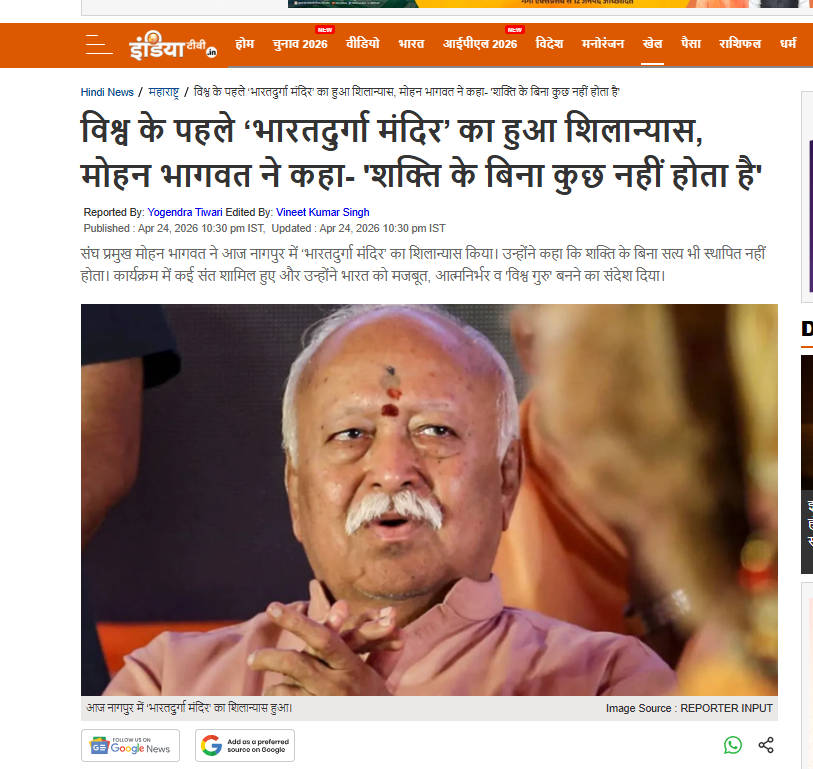
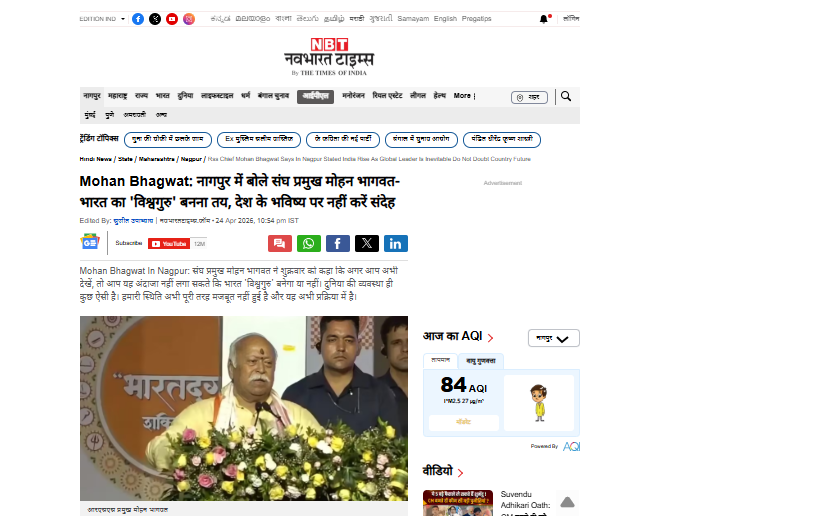
To verify the claim, we searched relevant keywords and found reports published on April 24, 2026, by India TV and Navbharat Times. According to these reports, Mohan Bhagwat laid the foundation stone of the world’s first Bharatdurga Temple in Nagpur during a ceremony organized at the Jamtha campus of Dr. Abaji Thatte Seva and Research Institute. Several prominent saints and religious leaders attended the event. Importantly, none of the reports described the temple as the “52nd Shakti Peeth.”
Further research led us to the full video of the foundation ceremony uploaded on the YouTube channel of Devendra Fadnavis. The stage backdrop and video thumbnail clearly mention “Bharatdurga Temple Foundation Ceremony.” However, the viral image frame was not visible anywhere in the authentic footage.

We also analyzed the viral image using AI detection tools, which indicated that the image was AI-generated.
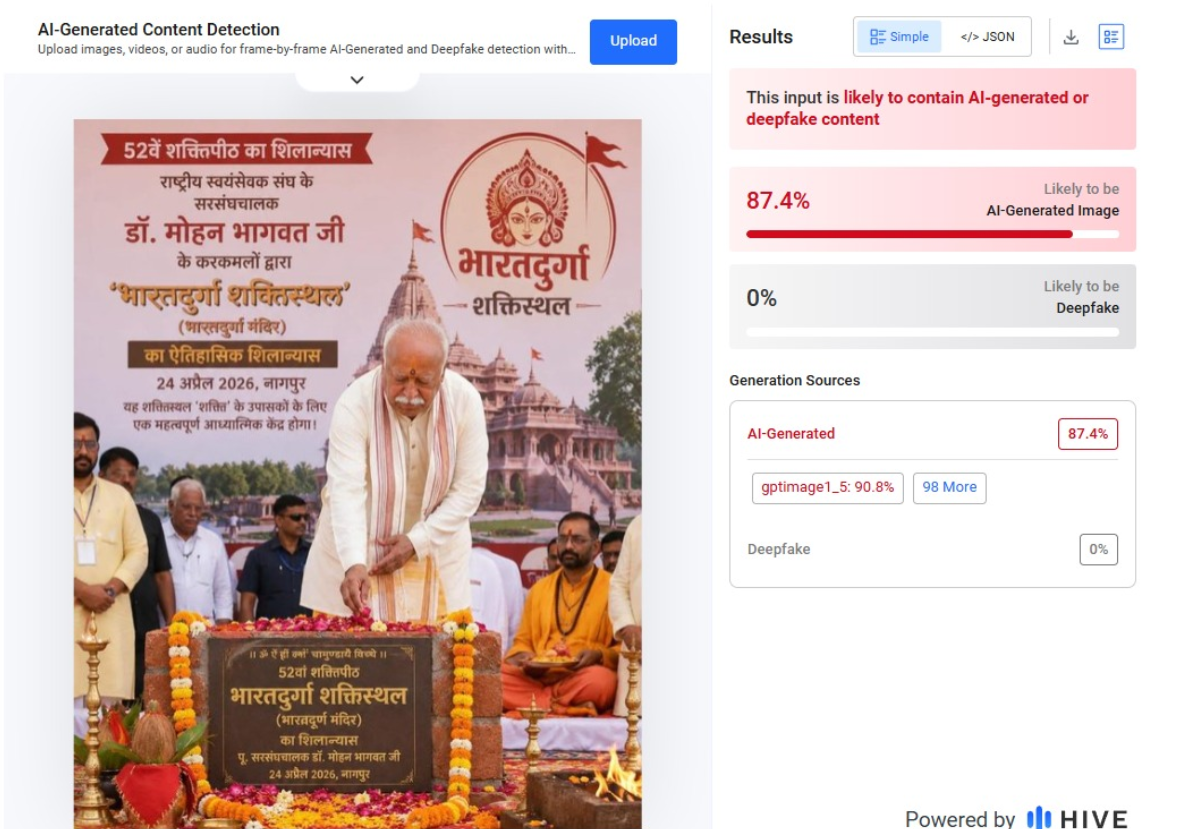
Conclusion
Our research confirms that the claim about Mohan Bhagwat laying the foundation of a “52nd Shakti Peeth” is false. The viral image is AI-generated. In reality, he participated in the foundation ceremony of the Bharatdurga Temple in Nagpur.

Introduction
To every Indian’s pride, the maritime sector has seen tremendous growth under various government initiatives. Still, each step towards growth should be given due regard to security measures. Sadly, cybersecurity is still treated as a secondary requirement in various critical sectors, let alone to protect the maritime sector and its assets. Maritime cybersecurity includes the protection of digital assets and networks that are vulnerable to online threats. Without an adequate cybersecurity framework in place, the assets remain at risk from cyber threats, such as malware and scams, to more sophisticated attacks targeting critical shore-based infrastructure. Amid rising global cyber threats, the maritime sector is emerging as a potential target, underscoring the need for proactive security measures to safeguard maritime operations. In this evolving threat landscape, assuming that India's maritime domain remains unaffected would be unrealistic.
Overview of India’s Maritime Sector
India’s potential in terms of its resources and its ever-so-great oceans. India is well endowed with its dynamic 7,500 km coastline, which anchors 12 major ports and over 200 minor ones. India is strategically positioned along the world’s busiest shipping routes, and it has the potential to rise to global prominence as a key trading hub. As of 2023, India’s share in global growth stands at a staggering 16%, and India is reportedly running its course to become the third-largest economy, which is no small feat for a country of 1.4 billion people. This growth can be attributed to various global initiatives undertaken by the government, such as “Sagarmanthan: The Great Oceans Dialogue,” laying the foundation of an insightful dialogue between the visionaries to design a landscape for the growth of the marine sector. The rationale behind solidifying a security mechanism in the maritime industry lies in the fact that 95% of the country’s trade by volume and 70% by value is handled by this sector.
Current Cybersecurity Landscape in the Maritime Sector
All across the globe, various countries are recognising the importance of their seas and shores, and it is promising that India is not far behind its western counterparts. India has a glorious history of seas that once whispered tales of Trade, Power, and Civilizational glory, and it shall continue to tread its path of glory by solidifying and securing its maritime digital infrastructure. The path brings together an integration of the maritime sector and advanced technologies, bringing India to a crucial juncture – one where proactive measures can help bridge the gap with global best practices. In this context, to bring together an infallible framework, it becomes pertinent to incorporate IMO’s Guidelines on maritime cyber risk management, which establish principles to assess potential threats and vulnerabilities and advocate for enhanced cyber discipline. In addition, the guidelines that are designed to encourage safety and security management practices in the cyber domain warn the authorities against procedural lapses that lead to the exploitation of vulnerabilities in either information technology or operational technology systems.
Anchoring Security: Global Best Practices & Possible Frameworks
The Asia-Pacific region has not fallen behind the US and the European Union in realising the need to have a dedicated framework, with the growing prominence of the maritime sector and countries like Singapore, China, and Japan leading the way with their robust frameworks. They have in place various requirements that govern their maritime operations and keep in check various vulnerabilities, such as Cybersecurity Awareness Training, Cyber Incident Reporting, Data Localisation, establishing secure communications, Incident management, penalties, etc.
Every country striving towards growth and expanding its international trade and commerce must ensure that it is secure from all ends to boost international cooperation and trust. On that note, the maritime sector has to be fortified by placing the best possible practices or a framework that is inclined towards its commitment to growth. The following four measures are indispensable to this framework, and in the maritime industry, they must be adapted to the unique blend of Information Technology (IT) and Operational Technology (OT) used in ships, ports, and logistics. The following mechanisms are not exhaustive in nature but form a fundamental part of the framework:
- Risk Assessment: Identifying, analysing, and ensuring that all systems that are susceptible to cyber threats are prioritized and vulnerability scans are conducted of vessel control systems and shore-based systems. The critical assets that have a larger impact on the whole system should be kept formidable in comparison to other systems that may not require the same attention.
- Access Control: Restrictions with regard to authorisation, wherein access must be restricted to verified personnel to reduce internal threats and external breaches.
- Incident Response Planning: The nature of cyber risks is inherently dynamic in nature; there are no calls for cyber attacks or warfare techniques. Such attacks are often committed in the shadows, so as to require an action plan to respond to and to recover from cyber incidents effectively.
- Continuous Staff Training: Regularly educating all levels of maritime personnel about cyber hygiene, threat trends, and secure practices.
CyberPeace Suggests: Legislative & Executive Imperatives
It can be said with reasonable foresight that the Indian maritime sector is in need of a national maritime cybersecurity framework that operates in cooperation with the international framework. The national imperatives will include robust cyber hygiene requirements, real-time threat intelligence mechanisms, incident response obligations, and penalties for non-compliance. The government must strive to support Indian shipbuilders through grants or incentives to adopt cyber-resilient ship design frameworks.
The legislative quest should be to incorporate the National Maritime Cybersecurity Framework with the well-established CERT-In guidelines and data protection principles. The one indispensable requirement set under the framework should be to mandate Cybersecurity Awareness Training to help deploy trained personnel equipped to tackle cyber threats. The rationale behind such a requirement is that there can be no “one-size-fits-all” approach to managing cybersecurity risk, which is dynamic and evolving in nature, and the trained personnel will play a key role in helping establish a customised framework.
References
- https://pib.gov.in/PressNoteDetails.aspx?NoteId=153432®=3&lang=1
- https://bisresearch.com/industry-report/global-maritime-cybersecurity-market.html#:~:text=Maritime%20cybersecurity%20involves%20safeguarding%20digital,and%20protection%20against%20potential%20risks.
- https://www.shipuniverse.com/2025-maritime-cybersecurity-regulations-a-simplified-breakdown/#:~:text=Japan%3A,for%20incident%20response%20and%20recovery.
- https://wwwcdn.imo.org/localresources/en/OurWork/Security/Documents/MSC-FAL.1-Circ.3-Rev.2%20-%20Guidelines%20On%20Maritime%20Cyber%20Risk%20Management%20(Secretariat)%20(1).pdf

Introduction
Indian Cybercrime Coordination Centre (I4C) was established by the Ministry of Home Affairs (MHA) to provide a framework and eco-system for law enforcement agencies (LEAs) to deal with cybercrime in a coordinated and comprehensive manner. The Indian Ministry of Home Affairs approved a scheme for the establishment of the Indian Cyber Crime Coordination Centre (I4C) in October2018, which was inaugurated by Home Minister Amit Shah in January 2020. I4C is envisaged to act as the nodal point to curb Cybercrime in the country. Recently, on 13th March2024, the Centre designated the Indian Cyber Crime Coordination Centre (I4C) as an agency of the Ministry of Home Affairs (MHA) to perform the functions under the Information Technology Act, 2000, to inform about unlawful cyber activities.
The gazetted notification dated 13th March 2024 read as follows:
“In exercise of the powers conferred by clause (b) of sub-section (3) of section 79 of the Information Technology Act 2000, Central Government being the appropriate government hereby designate the Indian Cybercrime Coordination Centre (I4C), to be the agency of the Ministry of Home Affairs to perform the functions under clause (b) of sub-section (3) of section79 of Information Technology Act, 2000 and to notify the instances of information, data or communication link residing in or connected to a computer resource controlled by the intermediary being used to commit the unlawful act.”
Impact
Now, the Indian Cyber Crime Coordination Centre (I4C) is empowered to issue direct takedown orders under 79(b)(3) of the IT Act, 2000. Any information, data or communication link residing in or connected to a computer resource controlled by any intermediary being used to commit unlawful acts can be notified by the I4C to the intermediary. If an intermediary fails to expeditiously remove or disable access to a material after being notified, it will no longer be eligible for protection under Section 79 of the IT Act, 2000.
Safe Harbour Provision
Section79 of the IT Act also serves as a safe harbour provision for the Intermediaries. The safe harbour provision under Section 79 of the IT Act states that "an intermediary shall not be liable for any third-party information, data, or communication link made available or hosted by him". However, it is notable that this legal immunity cannot be granted if the intermediary "fails to expeditiously" take down a post or remove a particular content after the government or its agencies flag that the information is being used to commit something unlawful. Furthermore, Intermediaries are also obliged to perform due diligence on their platforms and comply with the rules & regulations and maintain and promote a safe digital environment on the respective platforms.
Under the Information Technology (Intermediary Guidelines and Digital Media Ethics Code) Rules, 2021, The government has also mandated that a ‘significant social media intermediary’ must appoint a Chief Compliance Officer (CCO), Resident Grievance Officer (RGO), and Nodal Contact Person and publish periodic compliance report every month mentioning the details of complaints received and action taken thereon.
I4C's Role in Safeguarding Cyberspace
The Indian Cyber Crime Coordination Centre (I4C) is actively working towards initiatives to combat the emerging threats in cyberspace. I4C is one of the crucial extensions of the Ministry of Home Affairs, Government of India, working extensively to combat cyber crimes and ensure the overall safety of netizens. The ‘National Cyber Crime Reporting Portal’ equipped with a 24x7 helpline number 1930, is one of the key component of the I4C.
Components Of The I4C
- National Cyber Crime Threat Analytics Unit
- National Cyber Crime Reporting Portal
- National Cyber Crime Training Centre
- Cyber Crime Ecosystem Management Unit
- National Cyber Crime Research and Innovation Centre
- National Cyber Crime Forensic Laboratory Ecosystem
- Platform for Joint Cyber Crime Investigation Team.
Conclusion
I4C, through its initiatives and collaborative efforts, plays a pivotal role in safeguarding cyberspace and ensuring the safety of netizens. I4C reinforces India's commitment to combatting cybercrime and promoting a secure digital environment. The recent development by designating the I4C as an agency to notify the instances of unlawful activities in cyberspace serves as a significant step to counter cybercrime and promote an ethical and safe digital environment for netizens.
References
- https://www.deccanherald.com/india/centre-designates-i4c-as-agency-of-mha-to-notify-unlawful-activities-in-cyber-world-2936976
- https://www.business-standard.com/india-news/home-ministry-authorises-i4c-to-issue-takedown-notices-under-it-act-124031500844_1.html
- https://www.hindustantimes.com/india-news/it-ministry-empowers-i4c-to-notify-instances-of-cybercrime-101710443217873.html
- https://i4c.mha.gov.in/about.aspx#:~:text=Objectives%20of%20I4C,identifying%20Cybercrime%20trends%20and%20patterns
