
Deepfake Alert: Sachin Tendulkar's Warning Against Technology Misuse
Introduction
Deepfake have become a source of worry in an age of advanced technology, particularly when they include the manipulation of public personalities for deceitful reasons. A deepfake video of cricket star Sachin Tendulkar advertising a gaming app recently went popular on social media, causing the sports figure to deliver a warning against the widespread misuse of technology.
Scenario of Deepfake
Sachin Tendulkar appeared in the deepfake video supporting a game app called Skyward Aviator Quest. The app's startling quality has caused some viewers to assume that the cricket legend is truly supporting it. Tendulkar, on the other hand, has resorted to social media to emphasise that these videos are phony, highlighting the troubling trend of technology being abused for deceitful ends.
Tendulkar's Reaction
Sachin Tendulkar expressed his worry about the exploitation of technology and advised people to report such videos, advertising, and applications that spread disinformation. This event emphasises the importance of raising knowledge and vigilance about the legitimacy of material circulated on social media platforms.
The Warning Signs
The deepfake video raises questions not just for its lifelike representation of Tendulkar, but also for the material it advocates. Endorsing gaming software that purports to help individuals make money is a significant red flag, especially when such endorsements come from well-known figures. This underscores the possibility of deepfakes being utilised for financial benefit, as well as the significance of examining information that appears to be too good to be true.
How to Protect Yourself Against Deepfakes
As deepfake technology advances, it is critical to be aware of potential signals of manipulation. Here are some pointers to help you spot deepfake videos:
- Look for artificial facial movements and expressions, as well as lip sync difficulties.
- Body motions and Posture: Take note of any uncomfortable body motions or discrepancies in the individual's posture.
- Lip Sync and Audio Quality: Look for mismatches between the audio and lip motions.
- background and Content: Consider the video's background, especially if it has a popular figure supporting something in an unexpected way.
- Verify the legitimacy of the video by verifying the official channels or accounts of the prominent person.
Conclusion
The popularity of deepfake videos endangers the legitimacy of social media material. Sachin Tendulkar's response to the deepfake in which he appears serves as a warning to consumers to remain careful and report questionable material. As technology advances, it is critical that individuals and authorities collaborate to counteract the exploitation of AI-generated material and safeguard the integrity of online information.
Reference
- https://www.news18.com/tech/sachin-tendulkar-disturbed-by-his-new-deepfake-video-wants-swift-action-8740846.html
- https://www.livemint.com/news/india/sachin-tendulkar-becomes-latest-victim-of-deepfake-video-disturbing-to-see-11705308366864.html

Related Blogs
The Expanding Governance Challenge of Artificial Intelligence
Artificial intelligence (AI) systems are increasingly embedded in economic and social infrastructure. They are being adopted in financial services, healthcare diagnostics, hiring systems, and public administration. But while these systems improve efficiency and decision-making, they also introduce new forms of technological risk.
Unlike conventional software, AI systems learn patterns from data and continue to evolve as they run. This poses governance issues since risks can arise throughout the AI life cycle, whether at the coding level or in their implementation.
The latest regulatory frameworks, such as the European Union’s AI Act (EU AI Act) and the UNESCO Recommendation on the Ethics of Artificial Intelligence, note that responsible AI governance depends on the realisation of where risks emerge across the development process.
This article maps the AI system lifecycle, identifies the risks that emerge at each stage and evaluates the policy tools used to mitigate them using the lifecycle framework developed by the Organisation of Economic Co-operation and Development (OECD).
The Lifecycle of an AI System
AI systems are developed through a structured process that includes problem definition, dataset collection and preparation, model development, testing and validation, deployment, and monitoring.
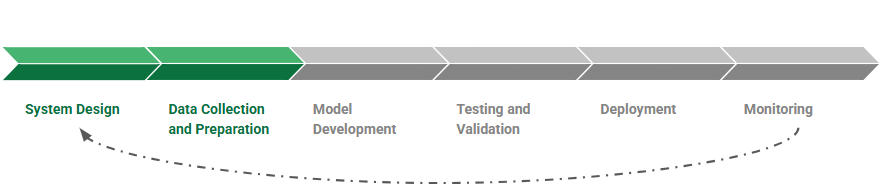
The OECD conceptualises this development process as the AI system lifecycle. Each stage entails various technical and administrative procedures, since choices made during these stages will dictate the goals and limits of an AI system. Further, the quality and representativeness of training sets will have a strong effect on the behaviour of models after implementation.
Since this is an iterative and not a linear procedure, risks can be introduced at each stage of the AI lifecycle. New data can be retrained into different models, and systems are regularly updated once they have been deployed, to address performance degradation, model errors, or unintended outputs. This iterative process means governance must address risks across the entire lifecycle, not just at deployment.
Where AI Risks Emerge
AI risks usually emerge earlier in the development process, especially in the phases when system objectives are formulated and training data are chosen. The EU AI Act and the UNESCO Recommendation on the Ethics of AI outline the following risks: bias and discrimination, privacy and data security violations, the absence of transparency in automated decision-making, and risks to fundamental rights.
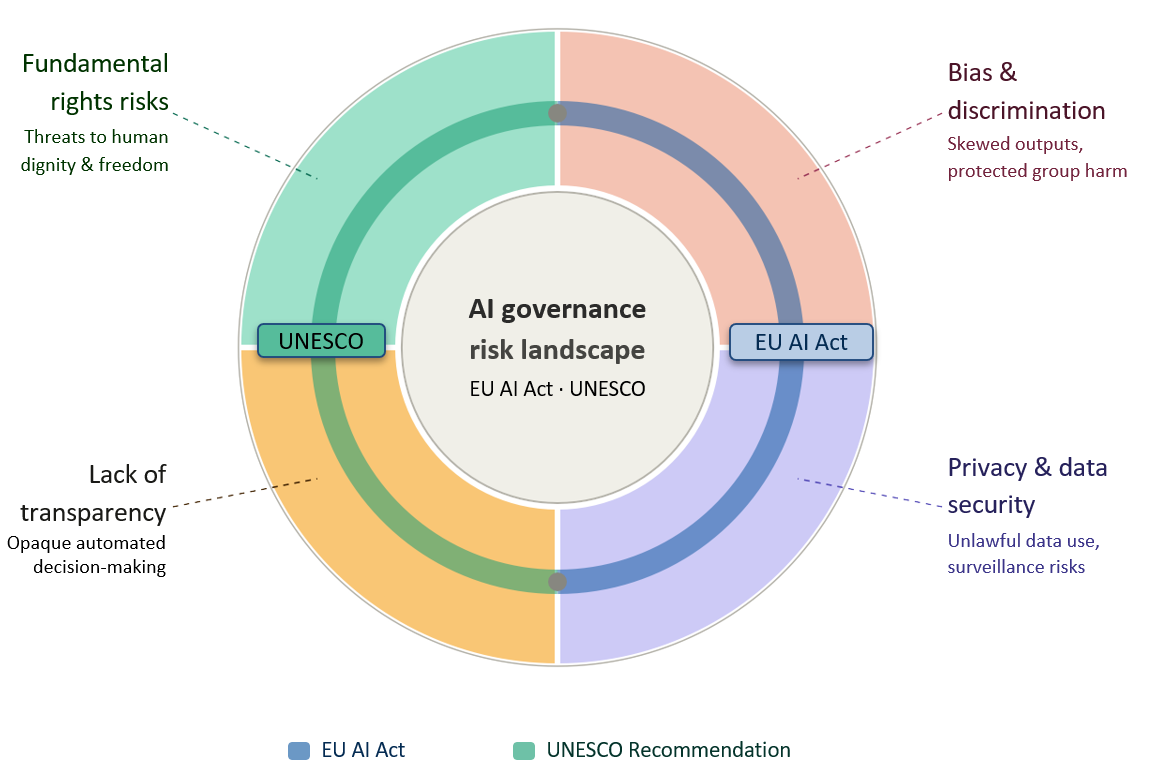
AI Governance Risk Landscape: Core Risk Categories Under International Frameworks
Risk categories jointly identified by the EU AI Act and UNESCO Recommendation on the Ethics of Artificial Intelligence
Outlining the risks throughout the AI lifecycle helps understand the areas where governance interventions are most necessary. For example, discriminatory outcomes often result from biased or unrepresentative training data, while safety failures are typically linked to inadequate testing before deployment. Risks such as misinformation arise post the development process, when generative AI systems are deployed at scale on digital platforms.
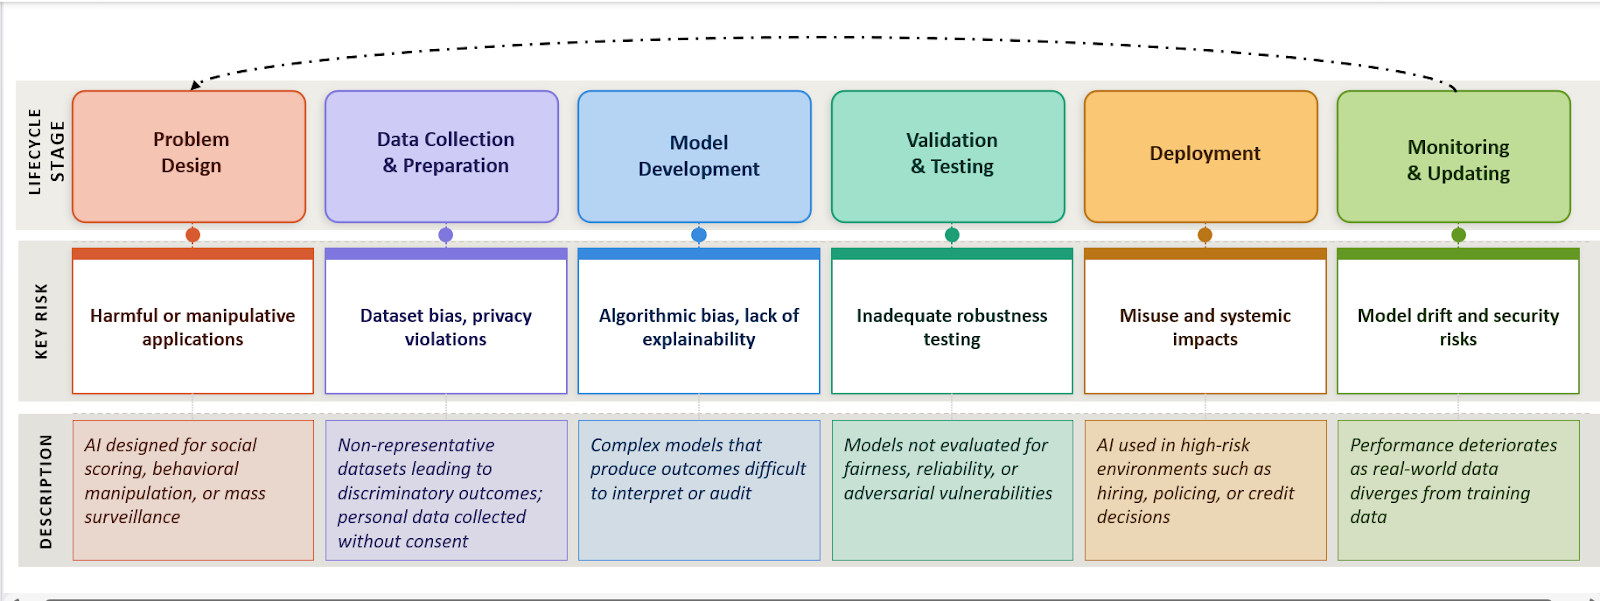
AI System Lifecycle: Key Risks at Each Stage
Risks identified per the EU AI Act and UNESCO Recommendation on the Ethics of AI
Understanding where risks emerge across the lifecycle explains why governance frameworks classify AI systems by risk and apply oversight at multiple stages.
Policy Tools for Mitigating AI Risks
Governments and international organisations have developed regulatory tools to help mitigate AI risks in the lifecycle. These tools are meant to make sure that AI technologies are identified as up to standard in safety, accountability and fairness prior to and after deployment.
For example, the OECD AI Policy Observatory recommends that governments adopt policy instruments such as risk evaluations, algorithmic auditing necessities, regulatory sandboxes, and transparency necessities of AI systems. The European Union’s Artificial Intelligence Act (AI Act) is one of the most comprehensive systems of governance that introduces a risk-oriented regulation strategy. It mandates adherence to requirements concerning data governance, documentation, human oversight, and robustness, and cybersecurity. Such requirements bring regulatory checkpoints to the lifecycle of AI systems.
Mapping these policy tools across the lifecycle illustrates how governance mechanisms can intervene at different stages of AI development.
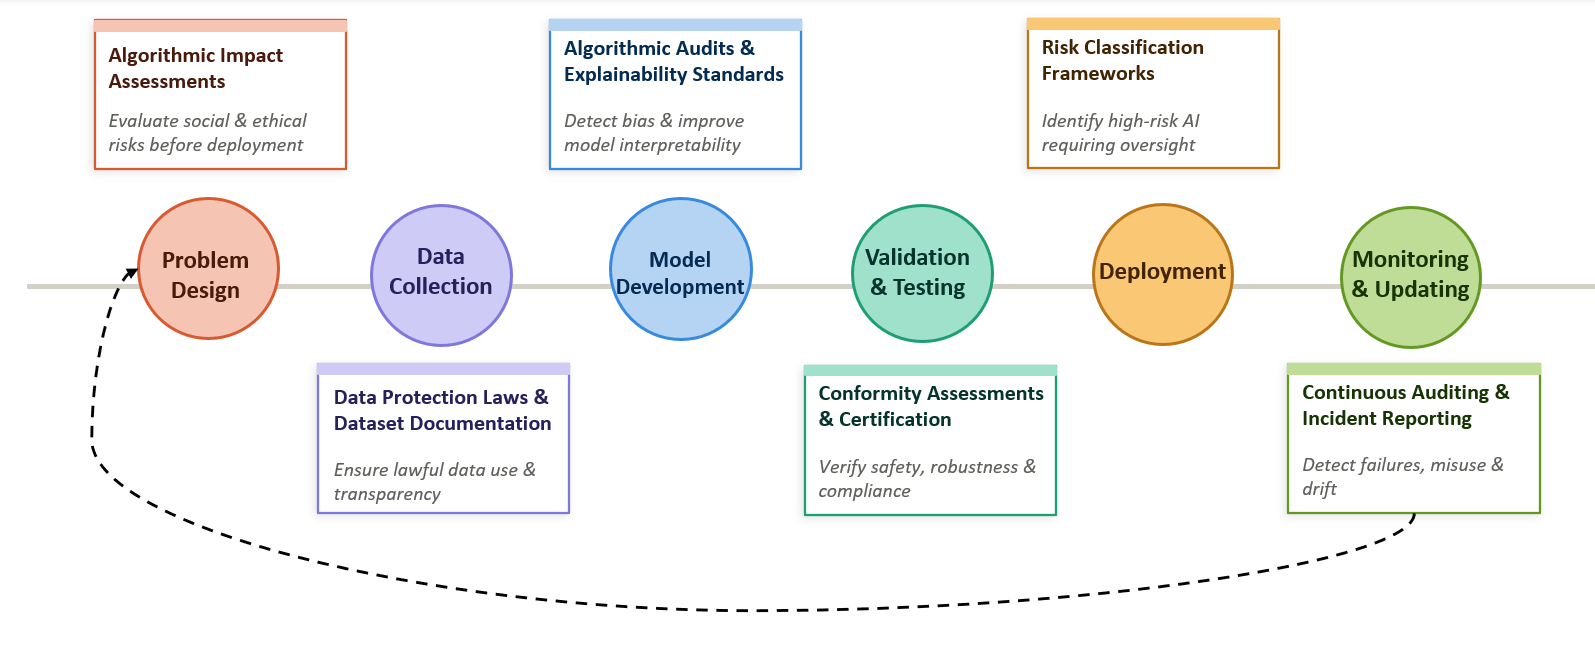
Governance Overlay: Policy Interventions Across the AI Lifecycle
Regulatory tools mapped at each stage of AI development per the EU AI Act and UNESCO Recommendation on the Ethics of AI
Several policy tools are directed at the risks that occur in the pre-developmental stages. In one example, algorithmic impact assessment has been applied in various jurisdictions to measure the possible consequences of automated decision systems on society before implementation. On the same note, the requirements of dataset documentation, including dataset transparency requirements and model cards, are aimed at enhancing accountability during the training and development stages of the AI systems. Therefore, lifecycle-based policy design allows regulators to intervene before harmful outcomes occur, rather than responding only after AI systems have caused damage in real-world environments.
The Policy Gap in AI Governance
The misalignment between risks and governance tools across the AI lifecycle indicates a critical structural gap in existing regulations. Numerous governance processes become activated after AI systems are classified as “high risk” or after they are implemented in the real world. But the most serious sources of damage have their roots in earlier stages of the development procedure.
An example is that prejudiced or unbalanced training data is almost inevitably a source of discriminative results in automated decision systems. When these types of models are applied in areas like staffing, credit rating, or in providing services to the public, such biases can quickly spread to large populations and undermine democratic rights. In the same way, the lack of transparency in model design might result in the fact that the regulator or individuals are affected by the decision-making process. This reflects a broader timing gap in AI governance, where risks originate during design and development, but regulatory intervention typically occurs only after deployment.
Analysis
1. Key risks originate before deployment: As depicted in the lifecycle mapping, the data collection and model development phase presents several significant governance risks as opposed to the deployment phase. Structural issues can be entrenched within AI systems even before they are deployed in practice due to bias in data sets, incomplete reporting of training sets, and obscured network designs.
2. Data governance is a primary point of vulnerability: Most of the instances of algorithmic discrimination listed above are associated with training material that is not representative of some population groups or is historical. Since machine learning models are optimisations of patterns that exist in datasets, these biases can be carried through the whole lifecycle and reproduced after deployment.
3. Regulatory approaches remain mismatched across jurisdictions: Different countries adopt varying approaches to AI governance, ranging from risk-based frameworks such as the EU AI Act to more sector-specific or voluntary guidelines in other regions. This divergence creates inconsistencies in safety, accountability, and enforcement standards, allowing risks to persist across borders and potentially undermining the protection of users in globally deployed AI systems.
4. Governance interventions remain uneven across the lifecycle: Whereas the various regulatory instruments aim at deployment and monitoring, fewer instruments systematically tackle the risks that are posed by the previous design and development phases.
Recommendations
1. Introduce mandatory lifecycle risk assessments: The regulatory systems need to demand systemic risk evaluation at the beginning of AI development, especially at the problem design and dataset selection phases. This would assist in detecting possible harmful applications in advance, before systems are constructed and installed.
2. Strengthen dataset governance standards: Training datasets must be supplemented with documentation as to their provenance, composition and limitations. Standardised documentation frameworks of data sets can assist in the discovery by regulators and auditors of the potential sources of bias or privacy threats.
3. Expand independent algorithmic auditing: AI systems can be assessed by regular third-party audits based on fairness, strength, and security weaknesses. The auditing mechanisms especially apply to high-risk systems employed in employment, finance or the public services.
4. Integrate continuous monitoring requirements: AI systems may be monitored regularly after implementation to identify model drift, unforeseen consequences, or abuse. Reporting systems can facilitate the process where the regulators can see the emerging risks and modify the governance systems.
Conclusion - The Need for Global AI Governance
Despite growing regulatory attention, global air governance remains fragmented. Different jurisdictions adopt varying approaches to risk classification, oversight, and enforcement, leading to inconsistencies in safety and accountability standards. Given that AI systems are often developed, deployed, and used across borders, this lack of coordination allows risks to persist beyond national regulatory frameworks.
Addressing these challenges requires a shift towards greater international cooperation and lifecycle-based governance. Developing shared standards, improving cross-border regulatory alignment, and embedding oversight across all stages of AI development will be essential to ensuring that AI systems are safe, transparent, and accountable in a globally interconnected environment.
References
- OECD AI lifecycle
- OECD AI system lifecycle description
- OECD AI governance lifecycle framework
- EU AI Act overview
- EU AI Act risk categories
- UNESCO Recommendation on the Ethics of AI
- AI governance lifecycle analysis
- OECD AI policy tools database

In what is being stated by experts to be one of the largest data breaches of all time, approximately 16 billion passwords were exposed online last week. According to various news reports, the leak contains credentials spanning a broad array of online services, including Facebook, Instagram, Gmail, etc., creating a serious alarm across the globe. Cybersecurity specialists have noted that this leak poses immense risks of account takeovers, identity theft, and enabling phishing scams. The leaked data is being described as a “collection-of-collections,” with multiple previously breached databases compiled into one easy-to-access repository for cybercriminals.
Infostealer Malware and Why It’s a Serious Threat
This incident brought to light a type of malware that experts refer to as the Infostealer. Just as the name suggests, this is a malware program made expressly to take personal information from compromised computers and devices, including cookies, session tokens, browser data, login credentials, and more. It targets high-value credentials, as opposed to ransomware, which encrypts files for ransom, or spyware that passively watches users. Once installed, they silently gather passwords, screenshots, and other information while hiding inside unassuming software, such as a game, utility, or browser plugin. Once stolen, these credentials are then combined by hackers to create databases, which are then offered for sale on dark web forums or even made public, as was the case in this breach. This is particularly risky since, if session tokens or other browser data are also taken, these credentials can be used to get around even two-factor authentication. As a result, the leak would also enable the rise of other crimes such as phishing.
Guidelines for protection
In response to this breach, India’s Computer Emergency Response Team (CERT-IN) issued an advisory, urging all internet users to take immediate action to protect their accounts. Although this is in response to the specific data leak, these are some key measures advised to be followed to maintain a general standard of cyber hygiene at all times.
- Reset your passwords: In case of incidents such as the above, users are advised to change the passwords of their accounts immediately. More so of the ones that have been compromised and need to be prioritised, such as email, online banking, and social media etc.
- Use strong, unique passwords and password manager features: Avoid password reuse across platforms. Using a password manager on a trusted platform can aid in storing and recalling them for different accounts.
- Monitor account activity: Check activity logs, especially for signs of unrecognised login attempts or password-reset notifications.
- Enable Multi-Factor Authentication (MFA): The user is advised to enable two-step verification (via an app like Google Authenticator or a hardware key), which will add an extra security layer.
- Phishing attacks: Cybercriminals will likely attempt to use leaked credentials to impersonate legitimate companies and send phishing emails. Read carefully before clicking on any links or attachments received.
- Scan devices for malware: Run updated antivirus or anti-malware scans to catch and remove infostealers or other malicious software lurking on your device.
Why This Data Breach is a Wake-Up Call
With 16 billion credentials exposed, this breach highlights the critical need for robust personal cybersecurity hygiene. It also reveals the persistent role of infostealer malware in feeding a global cybercrime economy, one where credentials are the most valuable assets. As Infosecurity Europe and other analysts highlight, infostealers are lightweight, often distributed via phishing or malicious downloads, and are highly effective at lifting data in the background without alerting the user. Even up-to-date antivirus software can struggle to catch new variants, making proactive security practices with respect to such malware all the more essential. In a time where data is everything, access to credentials can derive power and safety, regarding it must be kept in check.
Conclusion
This breach is a reminder that cybersecurity is a shared responsibility. Even with protective systems in place with respect to the industries and official authorities, every internet user must do their part in protecting themselves through cyber hygiene practices such as resetting passwords, using multi-factor authentication, staying vigilant against phishing scams, and ensuring devices are regularly scanned for malware. While breaches like this can seem overwhelming and might create a surge of panic, practical measures go a long way in mitigating exposure. Staying informed and proactive is the best defence one can adopt in a rapidly evolving threat landscape.
References
- https://economictimes.indiatimes.com/news/international/us/16-billion-passwords-exposed-in-unprecedented-cyber-leak-of-2025-experts-raise-global-alarm/articleshow/121961165.cms?from=mdr
- https://timesofindia.indiatimes.com/technology/tech-news/16-billion-passwords-leaked-on-internet-what-you-need-to-know-to-protect-your-facebook-instagram-gmail-and-other-accounts/articleshow/121967191.cms
- https://indianexpress.com/article/technology/tech-news-technology/16-billion-passwords-leaked-online-what-we-know-10077546/
- https://indianexpress.com/article/technology/tech-news-technology/16-billion-passwords-leaked-online-what-we-know-10077546/
- https://www.hindustantimes.com/business/certin-issues-advisory-after-data-breach-of-16-billion-credentials-asks-people-to-change-passwords-101750779940872.html
- https://www.cert-in.org.in/s2cMainServlet?pageid=PUBVLNOTES02&VLCODE=CIAD-2025-0024
- https://www.infosecurityeurope.com/en-gb/blog/threat-vectors/guide-infostealer-malware.html
Executive Summary
During the protests against Chief Election Commissioner (CEC) Gyanesh Kumar that began on October 10, the Delhi Police had detained thousands of people. Some of those detained alleged that the police assaulted them while they were in custody. CyberPeace Research found that the viral video dates back to 2017 and shows army personnel thrashing a student of Pulwama Degree College in Kashmir. The video has no connection with the protests held in Delhi.
Claim
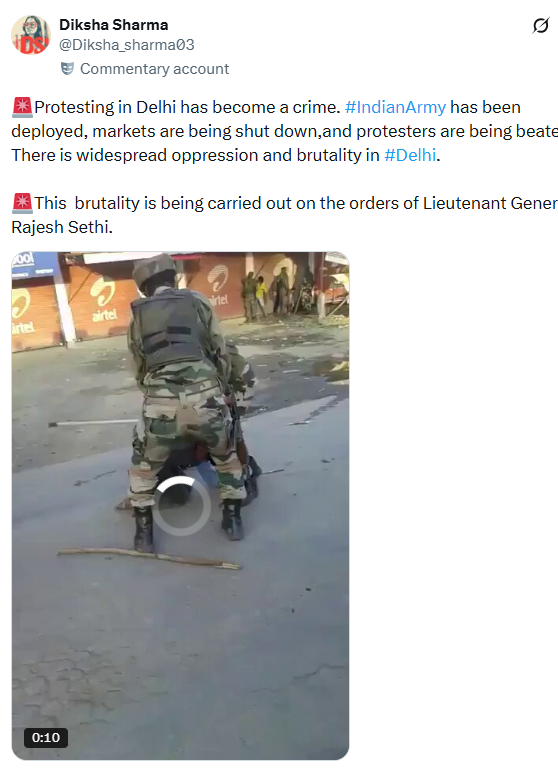
A video is now going viral on social media showing two army personnel thrashing a man pinned to the ground. An X user shared the video with the caption, “Protesting in Delhi has become a crime. The Indian Army has been deployed, markets are being shut down, and protesters are being beaten. There is widespread oppression and brutality in Delhi. This brutality is being carried out on the orders of Lieutenant General Rajesh Sethi.”
https://x.com/Diksha_sharma03/status/2109891097283756401
Fact Check
A reverse search of keyframes from the video led us to the account of journalist Shahid Tantray, who shared a longer version of the video on April 15, 2017. The video shows two more army personnel joining the two soldiers who were already thrashing the man. In his post, Tantray claimed that the man had been beaten by Indian Army personnel in South Kashmir.
https://x.com/shahidtantray/status/853184476272144384?s=20
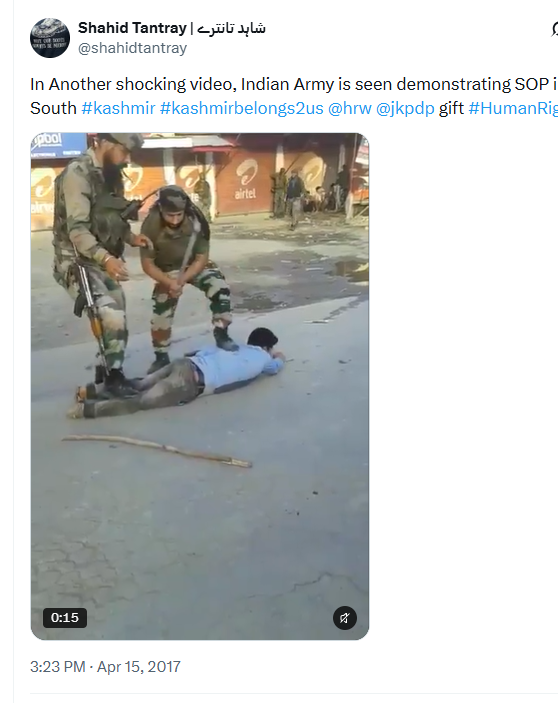
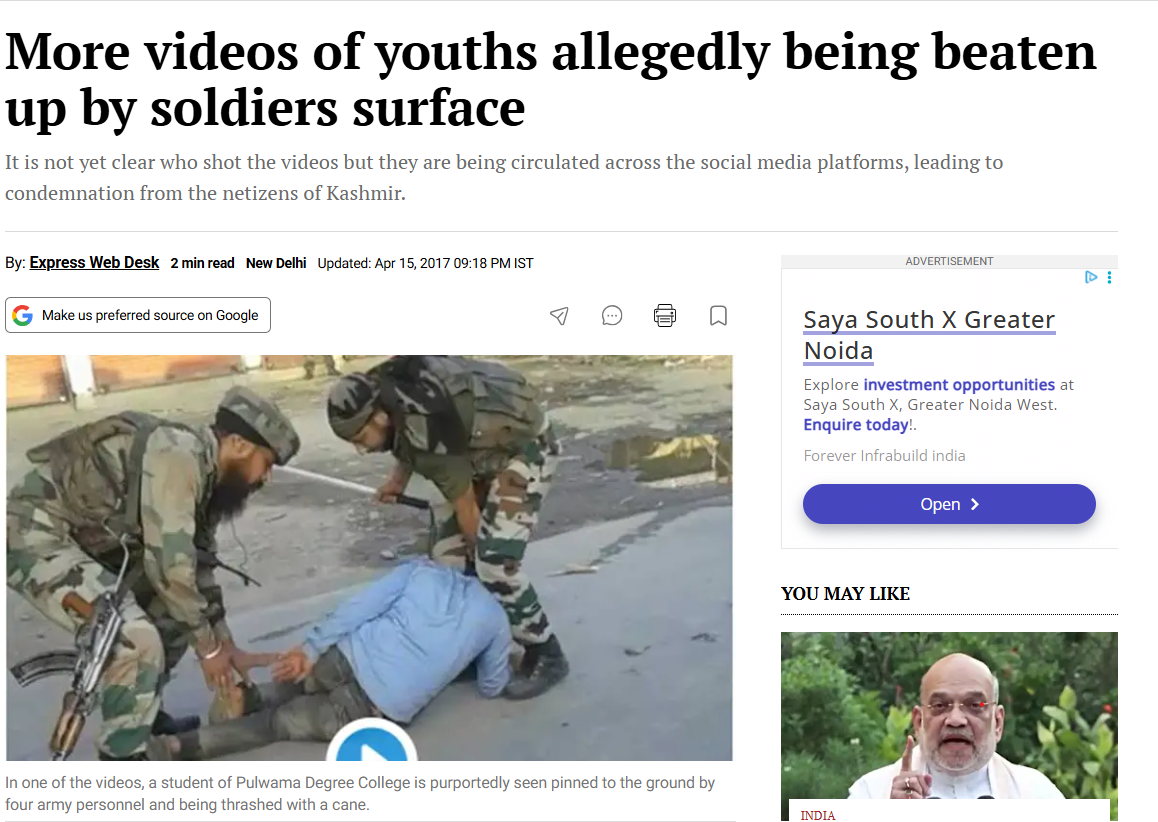
A report published by The Indian Express on April 15, 2017, featured a screenshot from the video. According to the report, four Indian Army personnel allegedly beat up a student of Pulwama Degree College in Jammu and Kashmir.
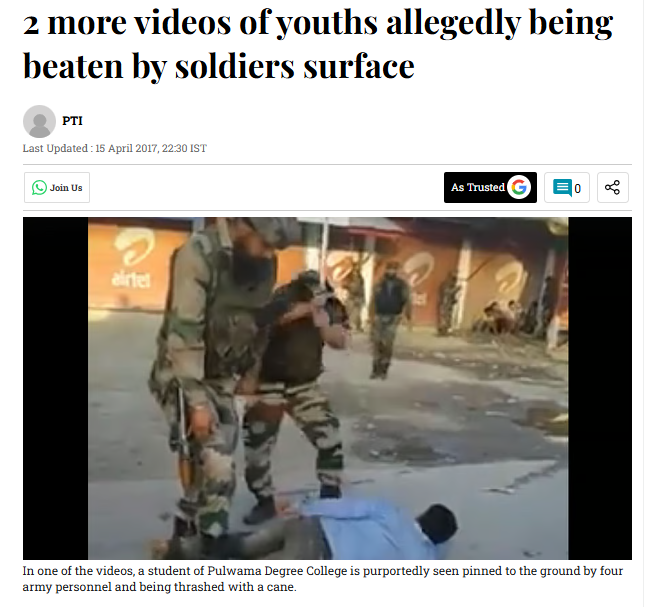
We also found a screenshot from the video in a report published by Deccan Herald on April 15, 2017. The report stated that the person beaten by the four army personnel was a student of Pulwama Degree College.
https://www.deccanherald.com/content/606516/2-more-videos-youths-allegedly.html
Conclusion
Our research found that the viral video dates back to 2017 and shows army personnel thrashing a student of Pulwama Degree College in Kashmir. The video has no connection with the protests held in Delhi.
